
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Twitter account of Jack Dorsey, Twitter CEO and co-founder, has been hacked

Hackers compromised the Twitter account of Jack Dorsey, CEO at Twitter, and published and retweeted offensive and racist messages. No one is secure online, news of the day is that hackers compromised the Twitter account of Jack Dorsey, CEO at Twitter and co-founder, and published and retweeted offensive and racist tweets. The hack tool place […]

Twitter CEO hack

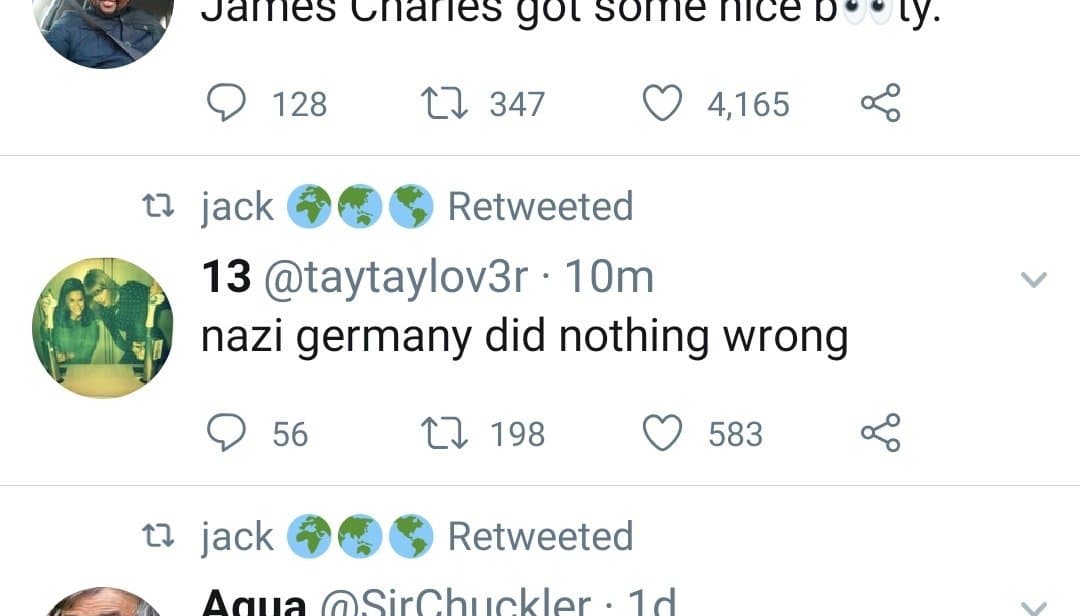
Hackers compromised the Twitter account of Jack Dorsey, CEO at Twitter, and published and retweeted offensive and racist messages.

No one is secure online, news of the day is that hackers compromised the Twitter account of Jack Dorsey, CEO at Twitter and co-founder, and published and retweeted offensive and racist tweets.

Jack Dorsey account

The hack tool place yesterday, the company quickly removed any tweet and retweet made by the attackers. Just after the account was hacked, the Twitter’s CEO name ‘Jack‘ started trending on Twitter.

“Yes, Jack’s account was compromised,” said Brandon Borrman, Vice President Global Communications at Twitter. “We’re working on it and investigating what happened.” said a Twitter spokesperson.

A group referring to itself as the Chuckling Squad took credit for the hack of the profile that has more than four million followers.

“A chat channel on Discord, a separate website, was apparently set up by the group to discuss and joke about the attack – but was quickly shut down.” reported the BBC.

“The Chuckling Squad has taken credit for a number of attacks on high-profile Twitter accounts recently, including beauty vlogger James Charles and an account belonging to YouTube personality Desmond Amofah, known as @Etika, who died earlier this year in an apparent suicide.“

Twitter clarified that its systems were not compromised, instead, the company blamed an unnamed mobile operator.

“The phone number associated with the account was compromised due to a security oversight by the mobile provider,” reads a statement from Twitter.

“This allowed an unauthorised person to compose and send tweets via text message from the phone number. That issue is now resolved.”

The offensive messages sent from the hacked account remained on the Dorsey’s profile page for around 30 minutes.

One tweet sent from the Jack Dorsey’s account also made a bomb threat, the hacker claiming they have placed a bomb at Twitter’s headquarters.

A Twitter user speculated that the tweets were sent due to the hack of CloudHopper, a company owned by Twitter that allows users to send out tweets using SMS messages.

https://twitter.com/Hooray/status/1167525255600058371

If confirmed there are two possible scenarios for this hack:

  • attackers hacked the CloudHopper infrastructure;
  • Jack Dorsey was the victim of a SIM swapping attack, the hackers replaced his phone number with one under their control and used it to send SMS messages that authorized the racist tweets.

I believe that Jack Dorsey was the victim of a SIM swapping attack, hackers used this technique to take over Dorsey’s account associated with his phone number and operate on his behalf.

Authorities are currently investigating the incident.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – Jack Dorsey, hacking)

[adrotate banner=”5″]

[adrotate banner=”13″]


