
Security Affairs
Russian APT29 Targets Mobile Users with Watering Hole Attacks|U.S. CISA adds Apple flaw to its Known Exploited Vulnerabilities catalog|U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|Russian APT29 Targets Mobile Users with Watering Hole Attacks|U.S. CISA adds Apple flaw to its Known Exploited Vulnerabilities catalog|U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Hackers stole credit card data from JM Bullion online bullion dealer

JM Bullion, the leading online bullion dealer in the United States, has disclosed a data breach, hackers stole customers’ credit card information. JM Bullion, the online retailer of products made of precious metals (i.e. gold, silver, copper, platinum, and palladium) has disclosed a data breach. JM Bullion has sent a ‘Notice of Data Security Incident‘ to its […]

Hackers stole credit card data from JM Bullion online bullion dealer

JM Bullion, the leading online bullion dealer in the United States, has disclosed a data breach, hackers stole customers’ credit card information.

JM Bullion, the online retailer of products made of precious metals (i.e. gold, silver, copper, platinum, and palladium) has disclosed a data breach.

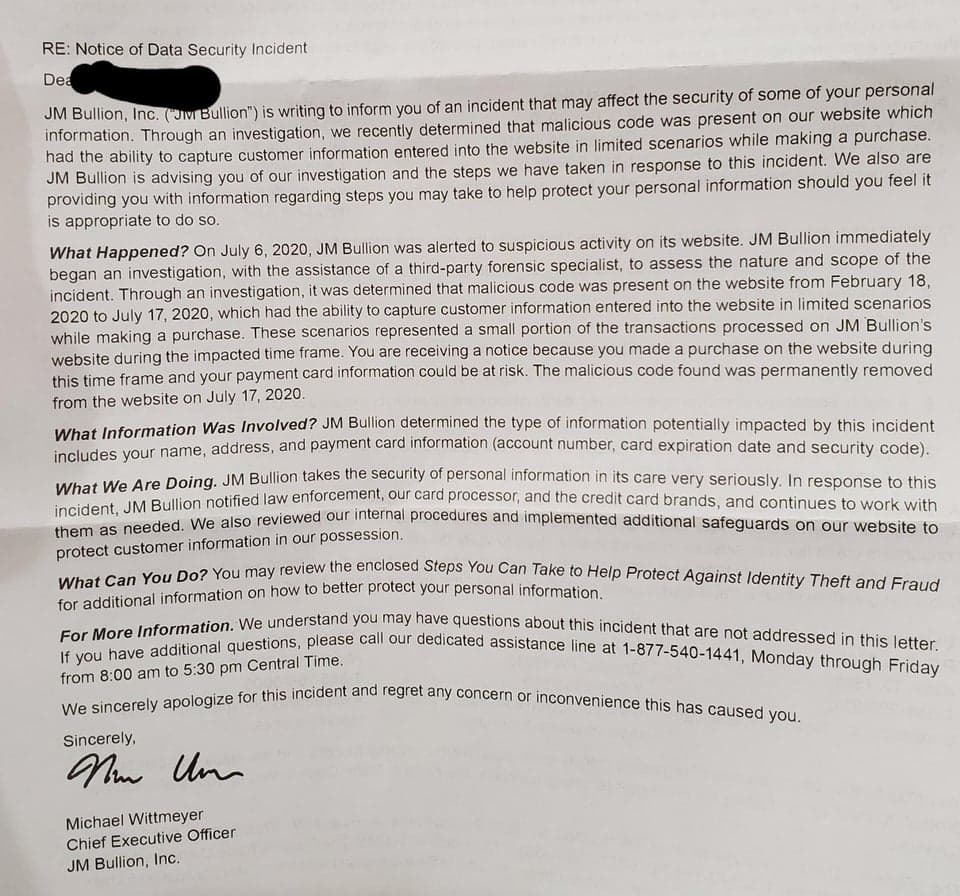
JM Bullion has sent a ‘Notice of Data Security Incident‘ to its customers, the security breach took place on February 18, 2020, when its staff discovered a malicious script on its website.

“On July 6, 2020, JM Bullion was alerted to suspicious activity on its website. JM Bullion immediately began an investigation, with the assistance of a third-party forensic specialist, to assess the nature and scope of the incident. Through an investigation, it was determined that malicious code was present on the website from February 18, 2020 to July 17, 2020, which had the ability to capture customer information entered into the website in limited scenarios while making a purchase,” reads the JM Bullion’s notice.

It is a classic Magecart attack, threat actors planted a malicious script on the website which was used to steal information entered by users while making a purchase. The company was alerted of the compromise on July 6, 2020 and immediately launched an investigation with the help of a third-party forensic firm.

Published by Reddit user r/Silverbugs

The information stolen in this attack includes customers’ names, addresses, and payment card information, including the account number, expiration date, and security codes.

Customers who made purchases on JM Bullion’s site between February 18th, 2020, to July 17th, 2020, have been impacted and are recommended to remain vigilant on credit card statements for fraudulent activity.

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, JM Bullion)

[adrotate banner=”5″]

[adrotate banner=”13″]


