
Security Affairs
U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

New JNEC.a Ransomware delivered through WinRAR exploit

A new strain of ransomware tracked as JNEC.a is spreading through an exploit that triggers the recently discovered vulnerability in WinRAR. The ransomware was involved in the attacks observed by the Qihoo 360 Threat Intelligence Center in the wild, threat actors used an archive named “vk_4221345.rar” that delivers JNEC.a when its contents are extracted with […]

JNEC.a _ransom-note

A new strain of ransomware tracked as JNEC.a is spreading through an exploit that triggers the recently discovered vulnerability in WinRAR.

The ransomware was involved in the attacks observed by the Qihoo 360 Threat Intelligence Center in the wild, threat actors used an archive named “vk_4221345.rar” that delivers JNEC.a when its contents are extracted with a vulnerable version of WinRAR.

The vulnerability, tracked as CVE-2018-20250, was discovered by experts at Check Point in February, it could allow an attacker to gain control of the target system.

Over 500 million users worldwide use the popular software and are potentially impacted by the flaw that affects all versions of released in the last 19 years.

The flaw is an “Absolute Path Traversal” issue in the library that could be exploited to execute arbitrary code by using a specially-crafted file archive.

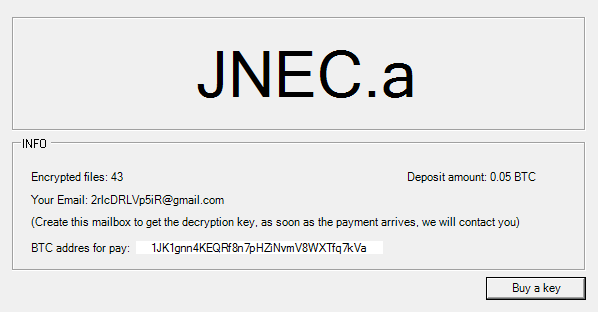
The ransomware encrypts data on the victim’s machine and appends the .Jnec extension to the encrypted data asking a ransom 0.05 bitcoins (about $200).

Once the ransomware has encrypted the files on the victim’s computer, it will generate a Gmail address that victims need to create in order to receive the file decryption key once they will pay the ransom.

JNEC.a _ransom-note

This way to identify infected machines represents a novelty in the threat landscape, victims must register the Gmail account provided by the ransomware in order to receive the decryption keys.

The JNEC.a ransomware also drops a ransom note (JNEC.README.TXT) on the infected computer to provide instructions on how to make the payment.

JNEC.a is written in .NET, when the archive is decompressed it shows a corrupted image of a girl that triggers an error and shows an incomplete picture, meanwhile the ransomware is already delivered to the computer.

The attackers renamed the malware dropped in the Startup folder as ‘GoogleUpdate.exe’ in the attempt to deceive the victims.

A few days ago, McAfee reported that attackers are continuing in exploiting the WinRAR flaw in the wild, they identified more than “100 unique exploits and counting” in the first week since the vulnerability was publicly disclosed.

The JNEC.a ransomware still has a low detection rate, it was identified as malicious by 31/71 antivirus of the VirusTotal services.

At the moment of writing, 29 antivirus engines detect JNEC.a as threat, according to the popular malware researcher Michael Gillespie a bug in its code makes it impossible to decrypt files even for the developer.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – JNEC.a ransomware, hacking )

[adrotate banner=”5″]

[adrotate banner=”13″]


