
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Emsisoft released a free Decrypter for JSWorm 2.0

Good news for the victims of the JSWorm 2.0 ransomware, thanks to experts at Emsisoft they can decrypt their file for free. Experts at Emsisoft malware research team released a decrypter for a recently discovered ransomware tracked as JSWorm 2.0. JSWorm 2.0 is written in C++ and implements Blowfish encryption. The first version of the […]

JSWorm decrypter

Good news for the victims of the JSWorm 2.0 ransomware, thanks to experts at Emsisoft they can decrypt their file for free.

Experts at Emsisoft malware research team released a decrypter for a recently discovered ransomware tracked as JSWorm 2.0.

JSWorm 2.0 is written in C++ and implements Blowfish encryption. The first version of the malware was written in C# and used the “.JSWORM” extension. Researchers believe both versions were developed by the same author.

Researchers found notable callouts in two different malware samples naming ID Ransomware and several prominent malware researchers:

“:HI SIRI, DEMONSLAY AND AMIIIIGO!!! HOW ARE YOU?”

and

“:ID-RANSOMWARE, IT’S JUST THE BEGINING [sic] OF SOMETHING NEW…”

Experts pointed out that there have been multiple confirmed submissions to the online service ID Ransomware that allows victims to upload their encrypted files to identify the ransomware that infected their machines. Since January 2019, experts observed encrypted files uploaded from South Africa, Italy, France, Iran, Vietnam, Argentina, United States, and other countries.

“Its files have the “.[ID-<numbers>][<email>].JSWORM” extension and the ransom note file named “JSWORM-DECRYPT.txt.”” reads the post published by Emsisoft.

Once infected a computer, the JSWorm 2.0 ransomware will perform the following actions:

  • Sets the “EnableLinkedConnections” registry key, which allows it to attack mapped drives when ran as admin.
  • Restarts SMB services (lanmanworkstation) to take effect (we are investigating if there’s more to the SMB vector).
  • Stops services for databases (MSSQL, MySQL, QuickBooks), kills shadow copies, disables recovery mode.

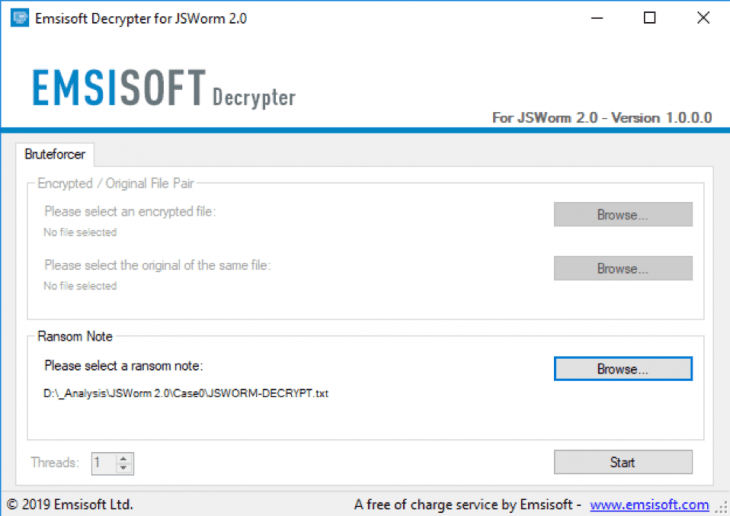
Victims of the JSWorm ransomware have to follow the instructions below to decrypt their files for free:

  1. Download the Emsisoft JSWorm 2.0 Decrypter.
  2. Run the executable and confirm the license agreement when asked.
  3. Click “Browse” and select the ransom note file on your computer.
  4. Click “Start” to decrypt your files. Note that this may take a while.
JSWorm decrypter

Done!

If you appreciate my effort in spreading cybersecurity awareness, please vote for Security Affairs in the section “Your Vote for the Best EU Security Tweeter”

Thank you

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – JSWorm 2.0. ransomware)

[adrotate banner=”5″]

[adrotate banner=”13″]


