
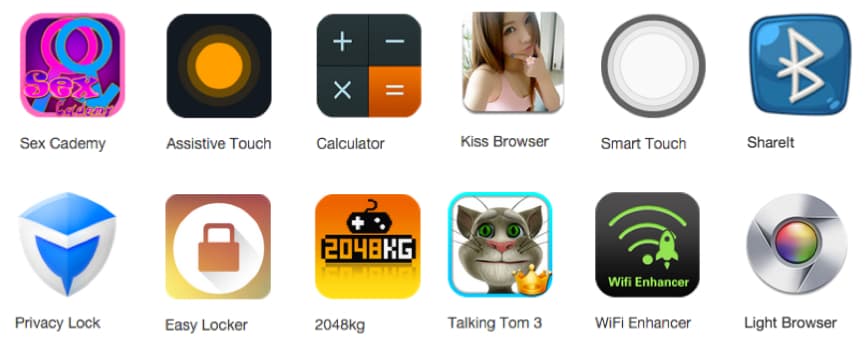
Researchers at FireEye spotted a new malicious adware campaign (Kemoge threat) that has infected Android mobile devices in more than 20 countries.
Security researchers at Fireeye have uncovered a malicious adware campaign which relies on a threat dubbed “Kemoge” based on the name of its command and control (C&C) domain aps.kemoge.net.
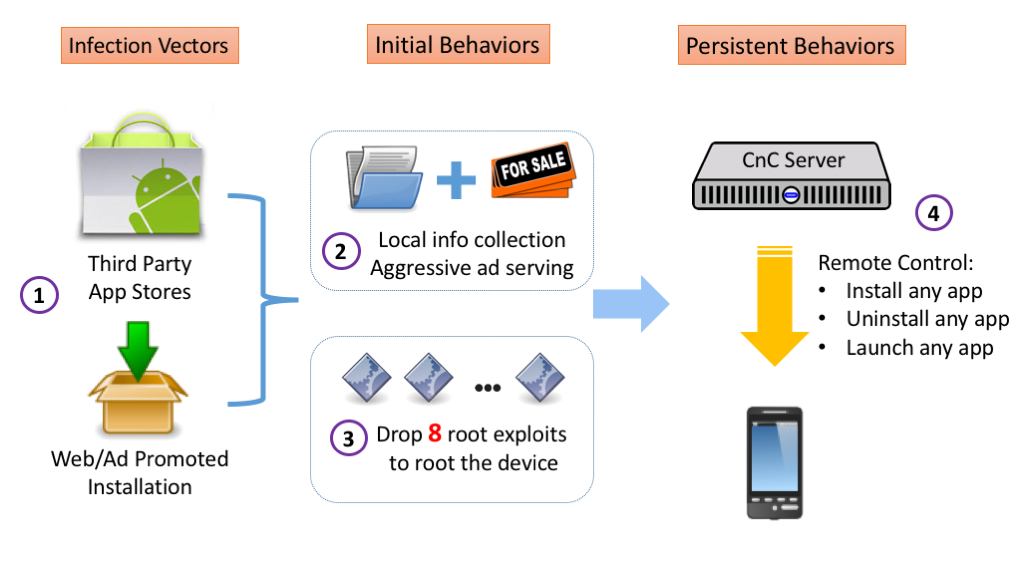
The Kemoge malware is packaged with various popular Android mobile apps such as games, calculators and device lockers, which are deployed to third-party app stores. The threat actors behind the malicious campaign promoted the trojanized apps through in-app ads and download links posted on various websites.
The experts at FireEye suspect that malicious adware might be a malicious code developed by a Chinese programmer, the name of the developer who uploaded it to Google Play is Zhang Long.
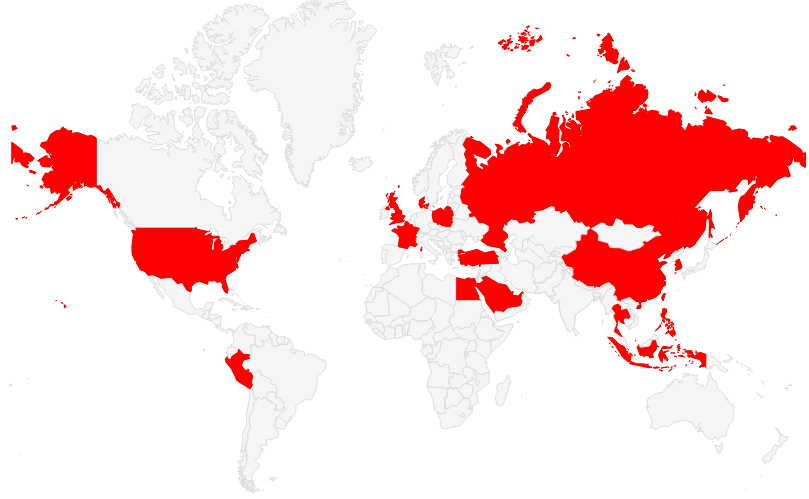
FireEye discovered Kemoge infections in over 20 countries, including China, Egypt, France, Indonesia, Malaysia, Peru, Poland, Russia, Saudi Arabia, the United Kingdom, and the United States.
The most worrying aspect related to Kemoga threat is that it can be served automatically via aggressive advertising networks that can gain root privileges to the victim’s mobile device.
Once infected a mobile device, Kemoge collects information on the smartphone and starts serving ads that are visible even without any apps running.
According to the researchers at FireEye, the most interesting feature of the Kemoge malware is its ability in operating system changing to the system settings to be able to automatically be launched every time the screen or the network connectivity is changed.
“Initially Kemoge is just annoying, but it soon turns evil. As shown in Figure 4, it registers MyReceiver in the AndroidManifest to automatically launch when the user unlocks the device screen or the network connectivity changes. ” states a blog post published by FireEye.
After launching the MyService looks, the malware searches for a ZIP file disguised as a MP4 from which it extracts eight exploits that are used to root a wide range of devices.
“The root methods include mempodroid, motochopper, perf_swevent exploit, sock_diag exploit, and put_user exploit. Some of the exploits seem to be compiled from open source projects (e.g. [2] [3]), but some come from the commercial tool “Root Dashi” (or “Root Master”), mentioned in our previous blog.” continues FireEye.
Once the device is rooted by the exploit, the malicious agent injects an APK (AndroidRTService.apk) into the system partition disguised as a legitimate system service.
The service tries to connect the aps.kemoge.net on the first launch and then every 24 hours from the previous command in order to avoid detection.
FireEye discovered one of the malicious apps on Google Play that was downloaded between 100,000 and 500,000 times. This version did not contain the root exploits or the C&C behavior, its code was signed with the same digital certificate used to sign the version uploaded on non official stores.
(Security Affairs –Kemoge , adware)


