
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Keytronic confirms data breach after ransomware attack

Printed circuit board assembly (PCBA) manufacturer Keytronic disclosed a data breach after a ransomware attack. Keytronic has confirmed a data breach after a ransomware group leaked allegedly stolen personal information from its systems. The company did not provide any info on the ransomware operation that hit its network, however Black Basta ransomware group leaked over […]

Keytronic Blackbasta ransomware

Printed circuit board assembly (PCBA) manufacturer Keytronic disclosed a data breach after a ransomware attack.

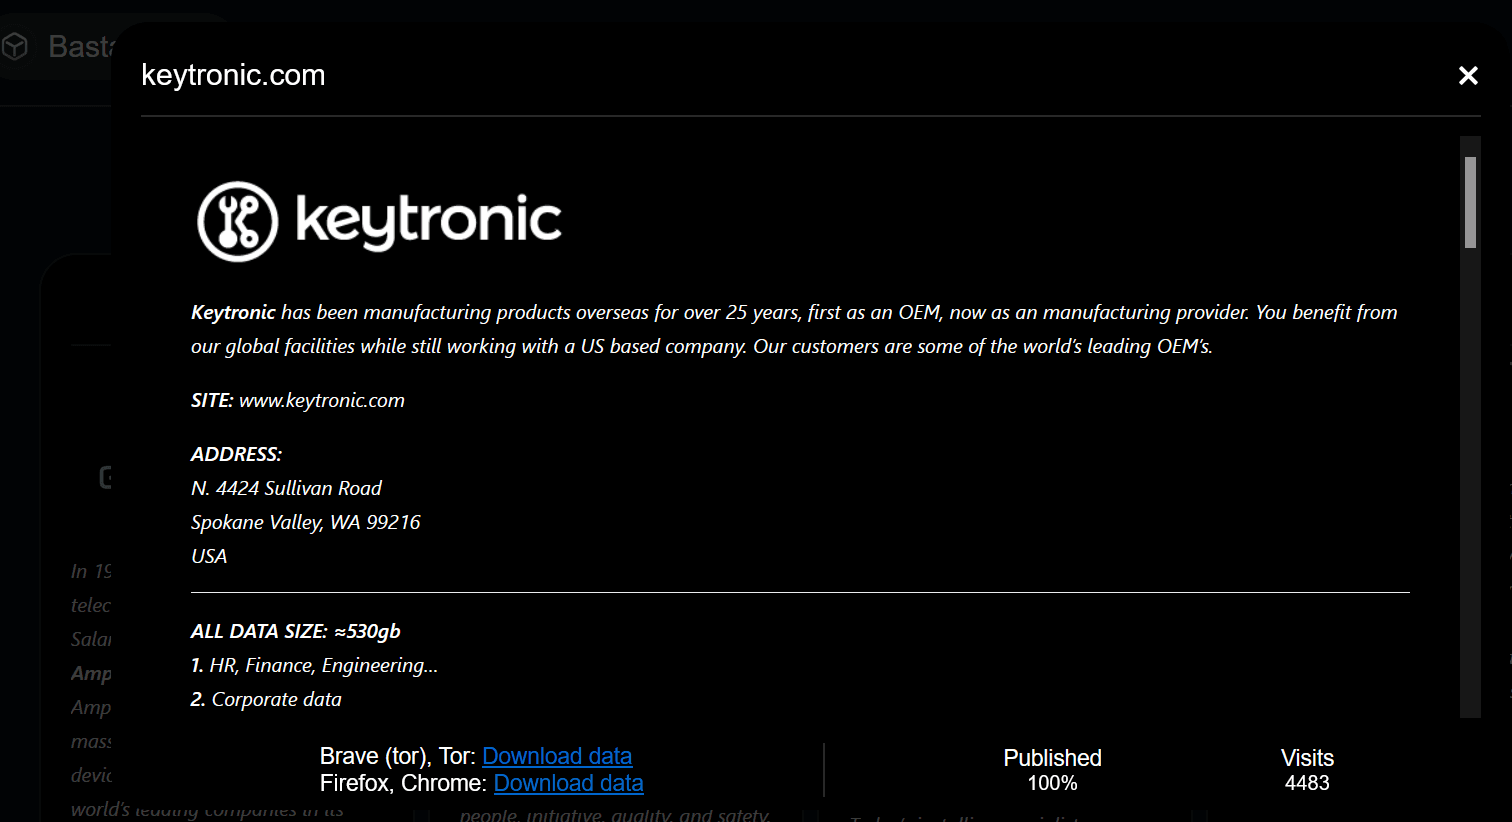
Keytronic has confirmed a data breach after a ransomware group leaked allegedly stolen personal information from its systems. The company did not provide any info on the ransomware operation that hit its network, however Black Basta ransomware group leaked over 500 gigabytes of data allegedly stolen from the company. Black Basta ransomware group claims to have stolen ≈530 GB of data, including HR, Finance, Engineering documents, Corporate data, and home users data.

Keytronic Blackbasta ransomware

On May 6, 2024, the company detected unauthorized access to portions of its information technology systems. Keytronic immediately launched an investigation into the incident with the help of external cybersecurity experts and notified law enforcement.

The company was forced to halt domestic and Mexico operations for approximately two weeks.

“The cybersecurity incident caused disruptions, and limitation of access, to portions of the Company’s business applications supporting aspects of the Company’s operations and corporate functions, including financial and operating reporting systems.” reads the FORM 8-K/A filed with SEC. “Since the date of the Original Report, the Company has determined that the threat actor accessed and exfiltrated limited data from the Company’s environment, which includes some personally identifiable information.”

As of the date of the FORM 8-K filing, the company has restored its operations and corporate functions and locked out the unauthorized third party.

Keytronic is notifying potentially affected parties and regulatory agencies.

The company confirmed that it has already incurred $600,000 in expenses related to the cybersecurity incident to date. The bad news is that financial losses are greater due to lost production for approximately two weeks in its domestic and Mexico operations.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, Keytronic)


