
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Watch out! European Consumer Organisation warns of some kid GPS smartwatches have security flaws

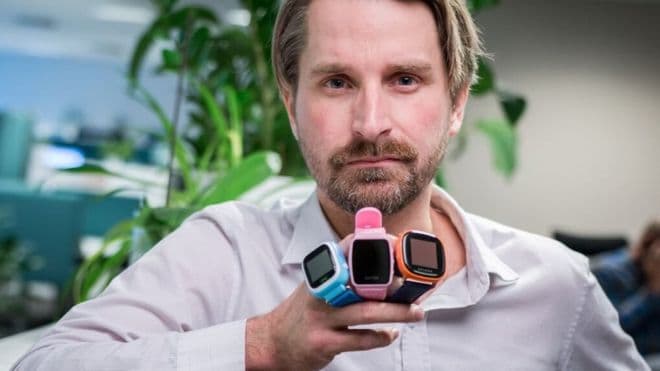
Some kid smartwatches available for sale in Europe pose security and privacy risks, including potentially allowing hackers to take control over them. The European Consumer Organisation (BEUC) warns that most children’s GPS-tracking smartwatches represent a threat for them. Many devices are affected by security vulnerabilities that could be exploited by an attacker to take control over […]

smartwatches security issues

Some kid smartwatches available for sale in Europe pose security and privacy risks, including potentially allowing hackers to take control over them.

The European Consumer Organisation (BEUC) warns that most children’s GPS-tracking smartwatches represent a threat for them. Many devices are affected by security vulnerabilities that could be exploited by an attacker to take control over the smartwatches, spy on conversations, or abuse the smartwatch camera to take picture and clips. An attacker can track GPS location, spoof GPS coordinates sent to watch’s paired app, misleading parents about the exact location of their children.

BEUC issued a public service announcement on the security and privacy risks related the children’s smartwatches. BEUC also pointed out that SOS button on some of these smartwatches is not reliable because hackers could replace the emergency phone number with their own.

The European Consumer Organization report has been drawn up by the Norwegian Consumer Council, it includes findings of security audits for popular brands of children’s smartwatches such as Gator 2, Tinitell, Viksfjord, and Xplora.

“What we see with these connected products is they are brought to the market too quickly, and they are not in line with EU laws when it comes to privacy and security,” said Johannes Kleis, the director of the communications department at BEUC.

Smartwatches represent a serious threat also for child’s privacy, vendors are potentially allowed to collect child data without giving parents the ability to monitor and stop these activities.

“These watches should not find their way into our shops,” Monique Goyens, Director General of BEUC, said in a press release.

“Parents buy them to protect their children. However, they are probably unaware that instead of protecting them they are making their children more vulnerable,” she added. “The EU urgently needs to regulate mandatory security standards for connected products. Producers should immediately fix these flaws or they should find their products withdrawn from the market.”

The security researcher Roy Solberg also published an analysis of the Gator 2 that includes details of security flaws he discovered.

“Gator Watch – a GPS watch for kids – is leaking data in all ends and anyone on the Internet can live track your kid. We’re not talking about a security vulnerability, we’re talking about non-existing security.” wrote Solberg.

This isn’t the first time that security experts warn of dangers related to kid smartwatches, in February 2016, security firm Rapid7 published a report on a vulnerability found in hereO kids’ GPS-tracking watches.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini 

(Security Affairs – Smartwatches, hacking)

[adrotate banner=”5″]

[adrotate banner=”13″]


