
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Killnet claims to have breached Lockheed Martin

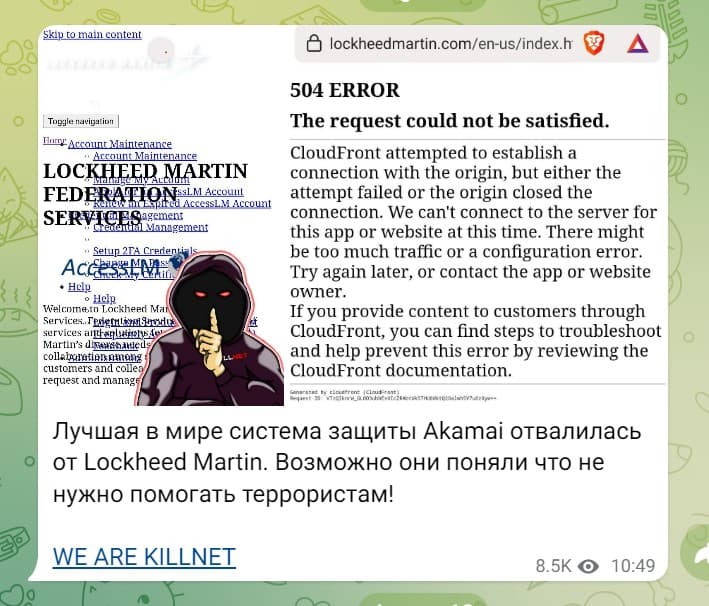
Russian hacker group Killnet claims to have launched a DDoS attack on the aerospace and defense giant Lockheed Martin.  The Moscow Times first reported that the Pro-Russia hacker group Killnet is claiming responsibility for a recent DDoS attack that hit the aerospace and defense giant Lockheed Martin. The Killnet group also claims to have stolen […]

killnet

Russian hacker group Killnet claims to have launched a DDoS attack on the aerospace and defense giant Lockheed Martin. 

The Moscow Times first reported that the Pro-Russia hacker group Killnet is claiming responsibility for a recent DDoS attack that hit the aerospace and defense giant Lockheed Martin.

The Killnet group also claims to have stolen data from a Lockheed Martin employee and threatened to share it.

killnet

The group has been active since March, it launched DDoS attacks against governments that expressed support to Ukraine, including Italy, Romania, Moldova, the Czech Republic, Lithuania, Norway, and Latvia.

In a video shared by the group on Telegram, the group claimed to have stolen the personal information of the Lockheed Martin employees, including names, email addresses, phone numbers, and pictures.

The group also shared two spreadsheets containing a message in Russian:

“If you have nothing to do, you can email Lockheed Martin Terrorists – photos and videos of the consequences of their manufactured weapons! Let them realize what they create and what they contribute to.” (Tanslated with Google).

At this time it is impossible to determine the real source of these data. Lockheed Martin is aware of the Killnet claims, but it did not comment on them.

Follow me on Twitter: @securityaffairs and Facebook

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, Killnet)

[adrotate banner=”5″]

[adrotate banner=”13″]


