
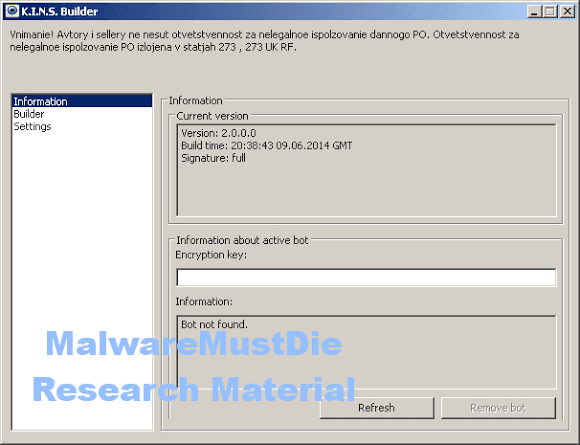
Researchers at MalwareMustDie group have discovered a KINS Malware builder leaked online, it is easy to predict a rapid diffusion of the banking trojan.
Security experts at the MalwareMustDie revealed that the source code of the popular KINS malware was leaked online.
Early 2013, experts at RSA discovered traces the banking trojan named KINS by analyzing the offer for malware in the underground communities. RSA researchers discovered an announcement on the Russian black market for the new KINS Trojan toolkit.
The advertisement for the sale of the KINS malware was published on a closed Russian-speaking underground forum.
On June 26, the experts at the MalwareMustDie discovered online a package that includes the KINS 2.0.0.0 builder, dubbed “KINS Builder,” and the source code for the control panel. The package was available on the Web, a circumstance that would allow the rapid diffusion of the banking trojan. Criminal crews can create their samples of the malware and using the available code to build a customized command & control center for the KINS botnet.
Researchers have pointed out that the developers of the malware builder call the tool “KINS Builder.” The experts that analyzed the KINS builder discovered that it generates binaries of a banking malware named ZeusVM, this means that authors of KINS malware have integrated the ZeusVM code into their trojan.
According to the researchers, the malware generated by the KINS builder is completely different from previous KINS detected in the wild.
Experts say this shows that KINS developers have integrated ZeusVM technology into their creation, for example the new KINS uses steganography to hide malware configuration data in a .JPG image file.
Experts at MalwareMustDie have published technical details and source code for the leaked KINS builder.
*Updated. The original version of the story incorrectly stated that the source code for both the builder and the control panel was made available. Only the source code for the control panel has been leaked. ” states the post from MalwareMustDie.
Currently, the MalwareMustDie research group is working with other experts, including the French Xylit0l and the Japanese unixfreaxjp, to prevent KINS spreading online by removing the package from several websites.

MalwareMustDie also revealed to have discovered version 3 of the KINS malware, which is offered for sale for $5,000 in underground forums.
Experts that desire to analyze the new variant of KINS malware can contact the researchers at MalwareMustDie.
(Security Affairs – KINS malware, cybercrime)


