
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Korean Davolink routers are easy exploitable due to poor cyber hygene

Davolink dvw 3200 routers have their login portal up on port 88, the access is password protected, but the password is hardcoded in the HTLM of login page. The story started in 2018 when Anubhav noticed a very basic flaw the routers of the Korean vendor Davolink. These Davolink dvw 3200 routers have their login […]

Death botnet

Davolink dvw 3200 routers have their login portal up on port 88, the access is password protected, but the password is hardcoded in the HTLM of login page.

The story started in 2018 when Anubhav noticed a very basic flaw the routers of the Korean vendor Davolink.

These Davolink dvw 3200 routers have their login portal up on port 88, the access is password protected.

Analyzing the code of the page the expert has noticed a function named “clickApply” that included the password in standard base 64 coding.

function clickApply(sel) 
{ 
var user_passwd="YWRtaW4="; 
var super_passwd="(null)"; 
document.forms[0].http_passwd.value = encode(document.forms[0].tmp_http_passwd.value);

Davolink dvw
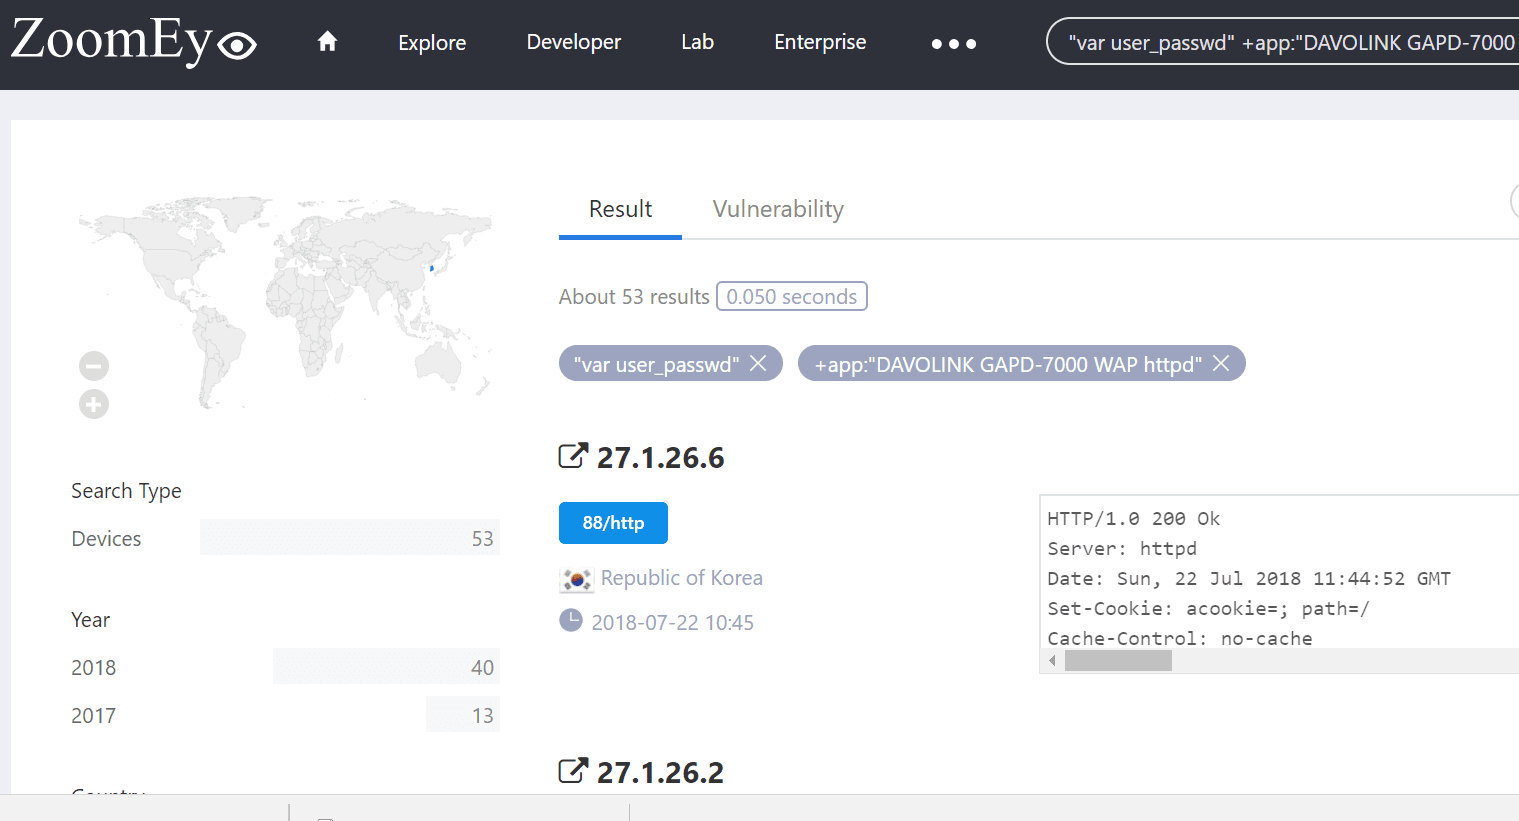
Scanning the Internet for similar devices using the search engine Zoomeye, he discovered more than 50 routers in Korea are exposed only and are accessible providing the hardcoded password.
Davolink

The expert reported the issue to the vendor that quickly acknowledged it and responded that they have discontinued the product. The vendor added that a working patch is already available.

The expert published the exploit code on exploit-db.

“Many IoT vendors are not doing the basics right as keeping the password in the HTML source, it is a very basic security issue” concluded Anubhav

“and it is a relevant issue as users in Korea are using it”

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(Security Affairs – Davolink, hacking)

[adrotate banner=”5″]

[adrotate banner=”13″]


