
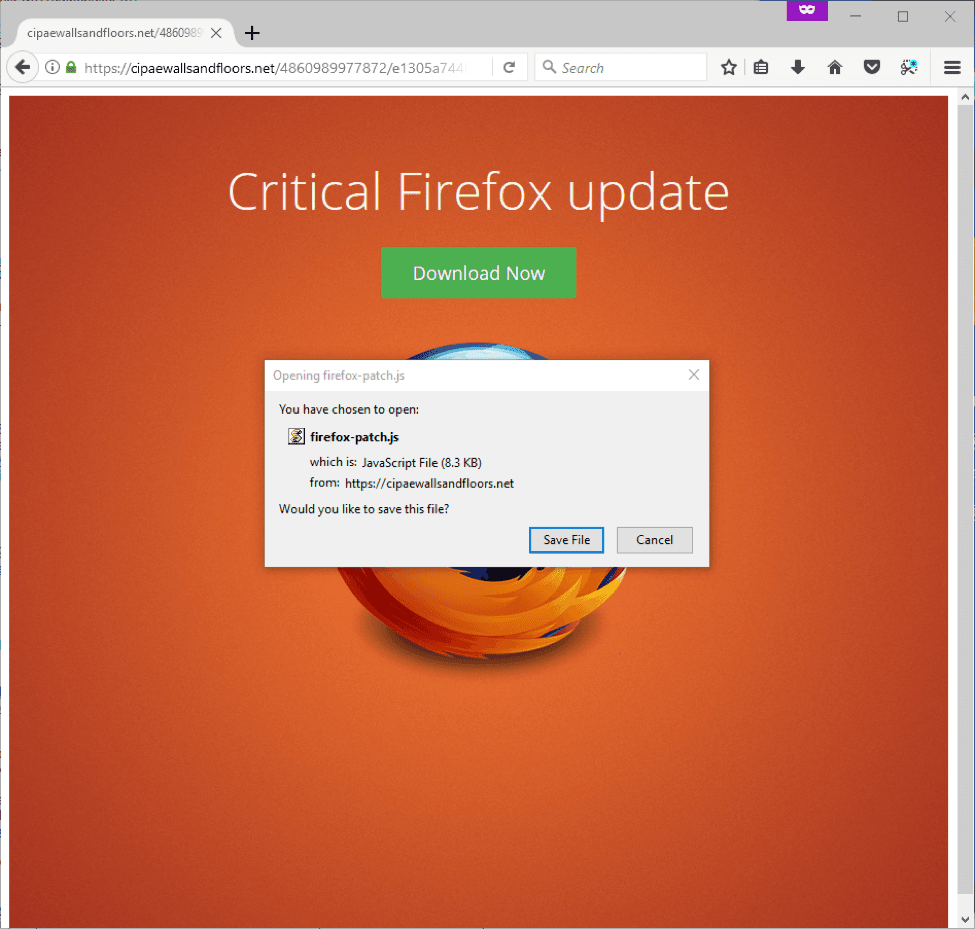
Security experts from Proofpoint have uncovered a malvertising actor named KovCoreG group that is spreading the Kovter malware via fake browser and Flash updates.
Security researchers from Proofpoint have uncovered a malvertising group dubbed KovCoreG that is spreading the Kovter malware via fake browser and Flash updates.
The Kovter malware is used in Ad fraud campaigns, victims were infected by simply clicking on online advertisements and generate revenue for the websites that host the ads.
Even if exploit kit activity drastically declined over the last year, malvertising remains a profitable business for crooks.
Crooks leveraged malicious ads on PornHub to redirect users to a scam site that was displaying users an urgent update, the messages are served depending on visitors browser.
IE and Edge users landing on this page were asked to download a Flash update, while Chrome and Firefox users were asked to download a browser update.
“Proofpoint researchers recently detected a large-scale malvertising attack by the so-called KovCoreG group, best known for distributing Kovter ad fraud malware and sitting atop the affiliate model that distributes Kovter more widely.” states ProofPoint.
“The attack has been active for more than a year and is ongoing elsewhere, but this particular infection pathway was shut down when the site operator and ad network were notified of the activity.”

The files served by the compromised website were JavaScript for Chrome and Firefox users, while IE and Edge are served with HTA files.
The malvertising impressions seem to be restricted by both geographical and ISP filtering, the KovCoreG group was focused on UK, US, Canadian, and Australian users.
“The infection chain in this campaign appeared on PornHub (Alexa US Rank 21 and world rank 38 as of this writing) and abused the Traffic Junky advertising network. It should be noted that both PornHub and Traffic Junky acted swiftly to remediate this threat upon notification.” continues ProofPoint.
Both Pornhub and Traffic Junky ad network shut down the malicious ads, once informed by Proofpoint.
The KovCoreG group, like other malvertising actors, recently are focusing on redirecting users to social engineering sites (i.e. fake download), instead of redirect users to websites hosting exploit kits.
“Once again, we see actors exploiting the human factor even as they adapt tools and approaches to a landscape in which traditional exploit kit attacks are less effective. While the payload in this case is ad fraud malware, it could just as easily have been ransomware, an information stealer, or any other malware.” concluded Proofpoint.
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(Security Affairs – malvertising campaign, KovCoreG group)
[adrotate banner=”5″]
[adrotate banner=”13″]


