
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

A leaked document raises a doubt about NSA knew the #Krack attack since 2010

An NSA leaked document about the BADDECISION hacking tool raises the doubt about National Security Agency knew the Krack attack since 2010. Security experts are questioning the NSA about the recently disclosed Krack attack the allows an attacker to decrypt information included in protected WPA2 traffic. Security experts believe that the National Security Agency was aware of the […]

Baddecision NSA Krack attack

An NSA leaked document about the BADDECISION hacking tool raises the doubt about National Security Agency knew the Krack attack since 2010.

Security experts are questioning the NSA about the recently disclosed Krack attack the allows an attacker to decrypt information included in protected WPA2 traffic.

Security experts believe that the National Security Agency was aware of the flaw and its arsenal included a specific exploit.

An NSA spokesperson did not comment the claims, this is normal for the US intelligence agencies, but according to ZDNet, rumors that it knew something about the vulnerability in the WPA2 protocol are circulating in the intelligence community.

In some cases, the US intelligence even is informed of a vulnerability doesn’t disclose it in the attempt to exploit it for intelligence operations.

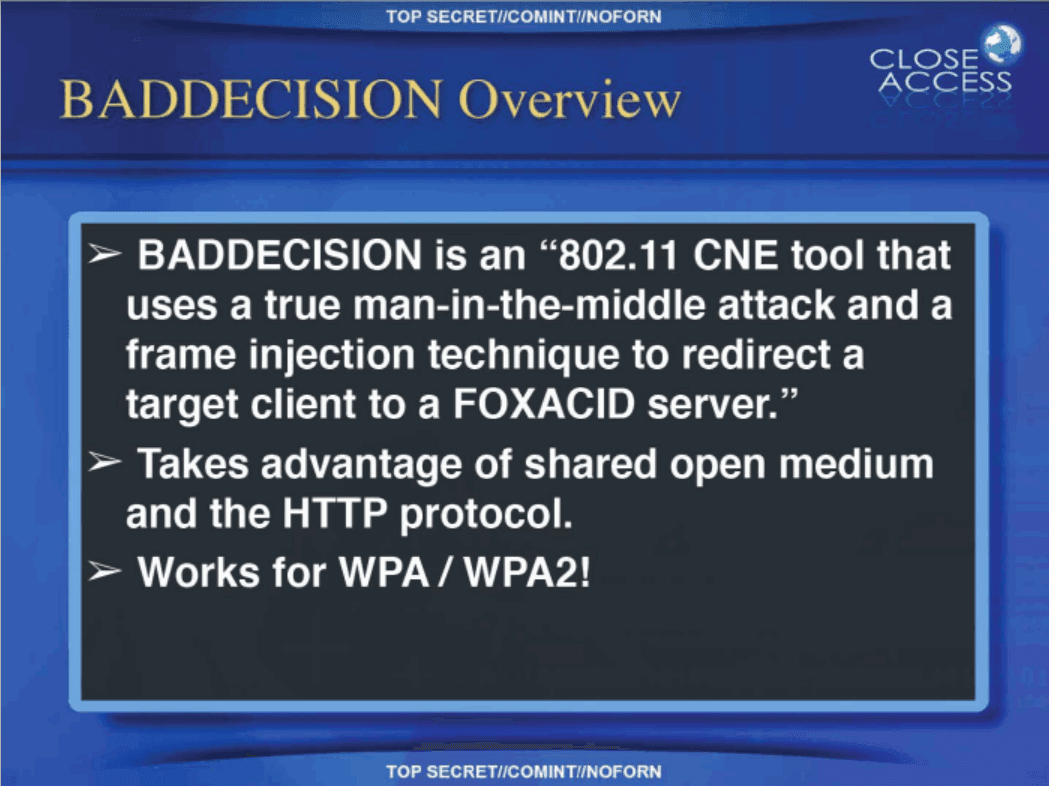
According to a top secret document leaked by the Edward Snowden and dated back 2010, the NSA arsenal included a hacking tool called BADDECISION classified as an “802.11 CNE tool. that used a true Man-in-the-middle attack and frame injection technique to redirect a target client to a FOXACID server.”

Baddecision NSA Krack attack

The NSA exploit was designed to target wireless networks by using a man-in-the-middle attack within range of the network, according to the Top-Secret slides it works for WPA and WAP2 networks, this implies that BADDECISION could bypass the encryption.

The FOXACID platform allows NSA operators to automatically supply the best malware for a specific target.

The slide said the hacking tool “works for WPA/WPA2,” suggesting that BADDECISION could bypass the encryption.

Cue the conspiracy theories. No wonder some thought the hacking tool was an early NSA-only version of KRACK.

Is BADDECISION the Krack attack tool?

Difficult to say, but many security researchers believe BADDECISION doesn’t exploit the KRACK attack.

According to former NSA staffers cited by ZDNet the NSA BADDECISION exploit is a sort of Ettercap tool that conducts man-in-the-middle attacks to carry out address resolution protocol (ARP) spoofing or poisoning.

Anyway, even if NSA BADDECISION doesn’t rely on the Krack attack, it is impossible to totally exclude that the agency was not aware of the vulnerability recently disclosed.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(Security Affairs – NSA, Krack attack)

[adrotate banner=”5″]

[adrotate banner=”13″]


