
A flaw in Argo CD tool for Kubernetes could be exploited by attackers to steal sensitive data from Kubernetes Apps.
A zero-day vulnerability, tracked as CVE-2022-24348, in the Argo CD tool for Kubernetes could be exploited by attackers to steal sensitive data from Kubernetes Apps, including passwords and API keys.
The flaw received a CVSS score of 7.7 and affects all versions, it was addressed with the release of versions 2.3.0, 2.2.4, and 2.1.9.
Argo CD (Continuous Deployment) automates the deployment of the desired application states in the specified target environments.
Argo CD is used by hundreds of organizations, including Alibaba Group, BMW Group, Deloitte, IBM, Intuit, Red Hat, Skyscanner, and Swisscom.
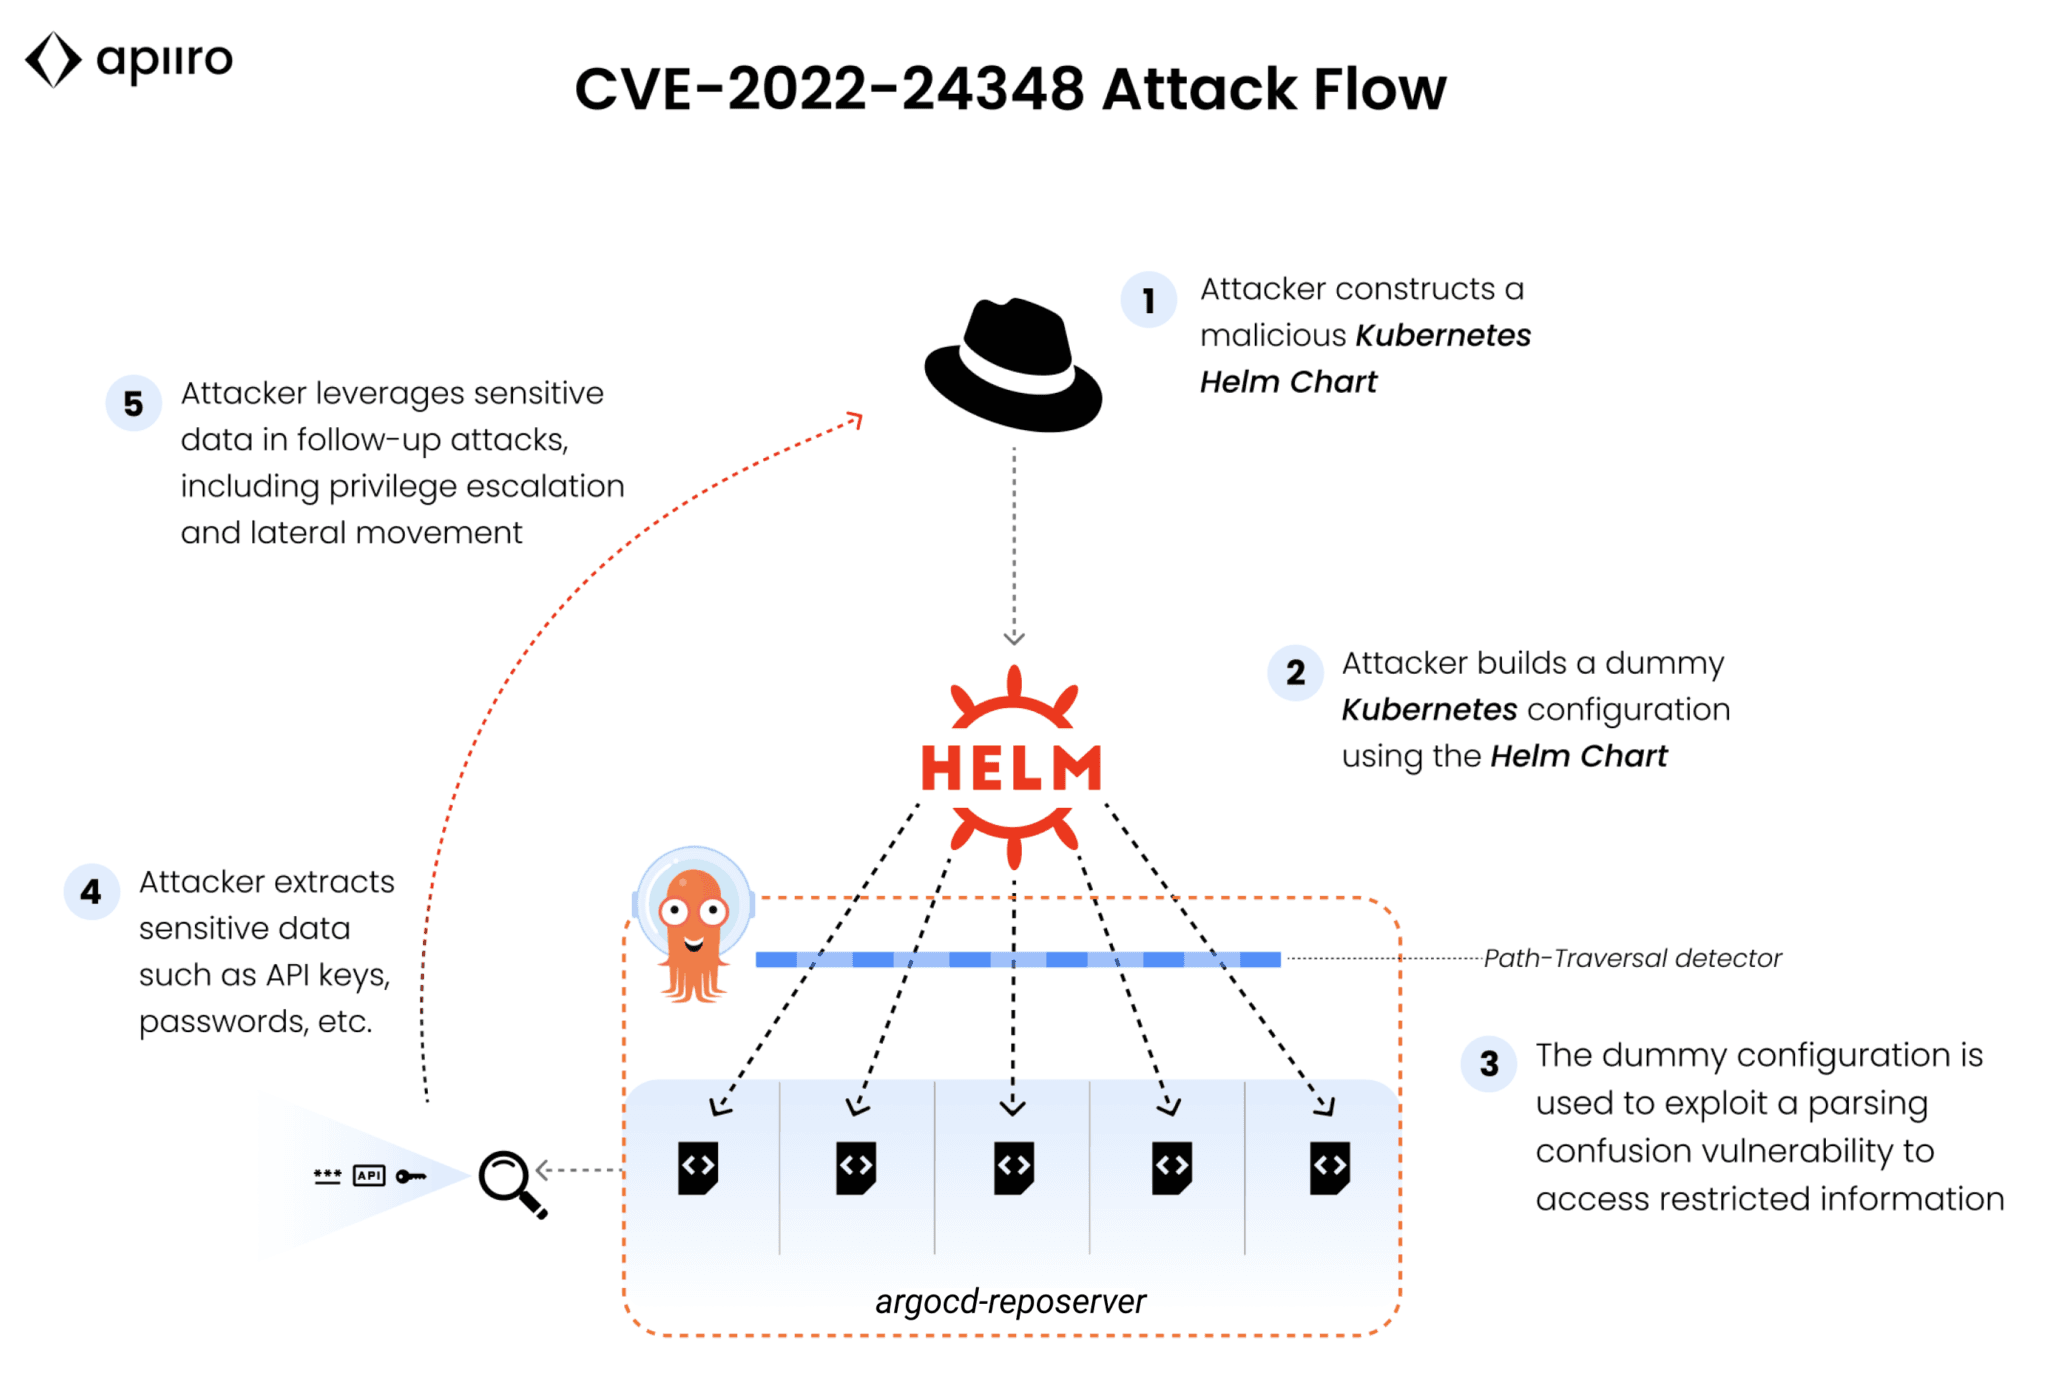
The vulnerability is a path-traversal vulnerability that could allow attackers to pass arbitrary values files to be consumed by Helm charts.
“Additionally, it is possible to craft special Helm chart packages containing value files that are actually symbolic links, pointing to arbitrary files outside the repository’s root directory.” reads the advisory published by security firm Apiiro that discovered the bug. “If an attacker with permissions to create or update Applications knows or can guess the full path to a file containing valid YAML, they can create a malicious Helm chart to consume that YAML as values files, thereby gaining access to data they would otherwise have no access to. The impact can especially become critical in environments that make use of encrypted value files (e.g. using plugins with git-crypt or SOPS) containing sensitive or confidential data, and decrypt these secrets to disk before rendering the Helm chart.”

Threat actors can exploit the vulnerability by loading a malicious Kubernetes Helm Chart YAML file, which describes a set of Kubernetes resources that are used to deploy an application onto the target system, and access confidential information from other apps.
Information contained in application files can be also used by attackers for lateral movements.
“First, there are the direct implications of contents read from other files present on the reposerver, which can contain sensitive information. This by itself can impact an organization.” continues the advisory.” Second, because application files usually contain an assortment of transitive values of secrets, tokens, and environmental sensitive settings – this can effectively be used by the attacker to further expand their campaign by moving laterally through different services and escalating their privileges to gain more ground on the system and target organization’s resources.”
Let’s close with the timeline for this vulnerability:
- 30-Jan-2022 : Vulnerability reported to vendor
- 30-Jan-2022 : Vendor verified and acknowledged the bug
- 31-Jan-2022 : Mutual continued triage to understand and discuss vulnerability’s extent and impact
- 01-Feb-2022 : Vendor reported on progressive work on patch and fix and release schedule
- 03-Feb-2022 : Synchronous release of advisories, patch, and blog
Follow me on Twitter: @securityaffairs and Facebook
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – hacking, Kubernetes)
[adrotate banner=”5″]
[adrotate banner=”13″]


