
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Lapsus$ extortion gang claims to have stolen sensitive data from Okta

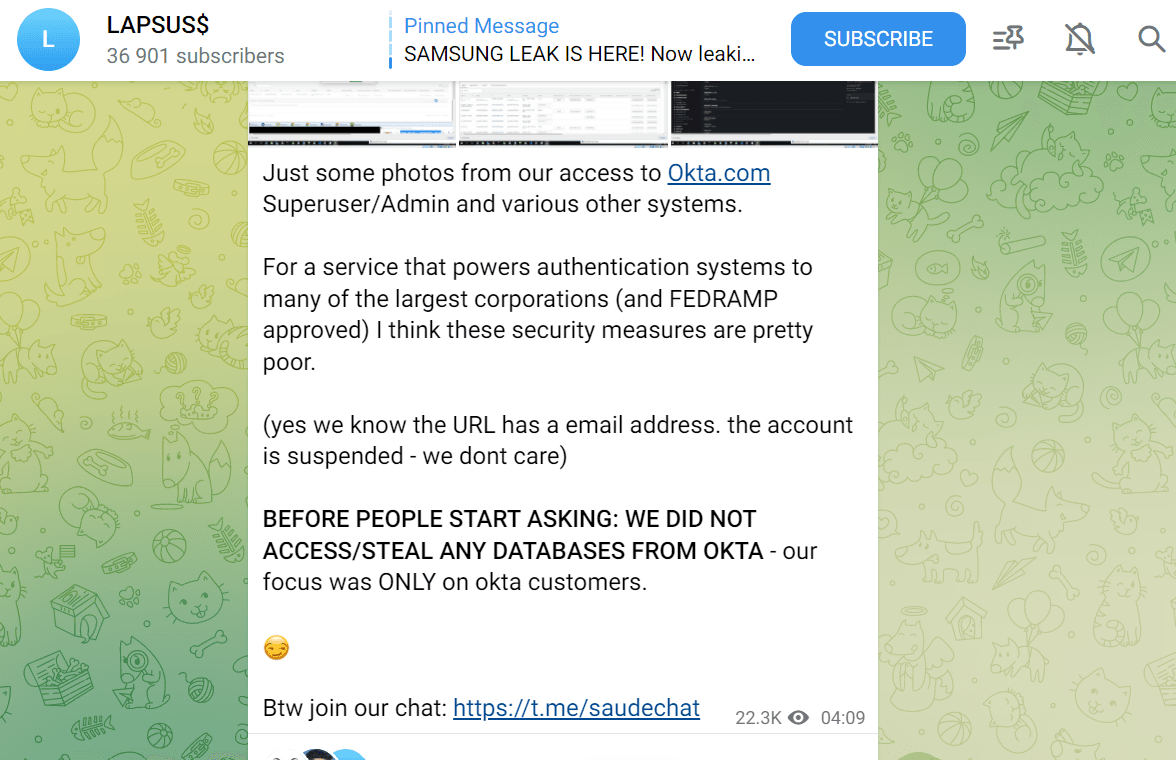
The Lapsus$ extortion group claims to have stolen sensitive data from the identity and access management giant Okta solutions. The gang announced the alleged hack through its Telegram channel and shared a series of screenshots as proof of the hack. Some of the images published by the threat actors appear to be related to the company’s […]

Lapsus$

The Lapsus$ extortion group claims to have stolen sensitive data from the identity and access management giant Okta solutions.

The gang announced the alleged hack through its Telegram channel and shared a series of screenshots as proof of the hack. Some of the images published by the threat actors appear to be related to the company’s customer data.

The message published by the group claims that the gang had Superuser and Admin access to multiple systems of the company.

okta

The company is investigating claims of a data breach which, if confirmed, could pose serious risks to the customers of the company.

“Okta is aware of the reports and is currently investigating,” states a spokesperson for the company. “We will provide updates as more information becomes available.”

Todd McKinnon, CEO at Okta, confirmed that in late January 2022, the company detected an attempt to compromise the account of a third party customer support engineer working for one of its subprocessors.

McKinnon added that there is no evidence of ongoing malicious activity that resulted from the activity detected in January.

A few hours ago, Lapsus$ also leaked data stolen from Microsoft‘s internal Azure DevOps server. The gang leaked an archive containing 37GB of source code allegedly belonging to Microsoft.

Over the last months, the Lapsus$ gang compromised other prominent companies such as NVIDIA, Samsung, Ubisoft, Mercado Libre, and Vodafone.

On Thursday, March 10, the group announced they’re starting to recruit insiders employed within major technology giants and ISPs, such companies include Microsoft, Apple, EA Games and IBM. Their scope of interests includes – major telecommunications companies such as Claro, Telefonica and AT&T.

Notably, the actors are looking to buy remote VPN access and asking potential insiders to contact them privately via Telegram, they then reward them by paying for the access granted.

Follow me on Twitter: @securityaffairs and Facebook

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, BazarLoader)

[adrotate banner=”5″]

[adrotate banner=”13″]


