
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Lapsus$ extortion gang claims to have hacked IT Giant Globant

The Lapsus$ extortion group claims to have hacked IT giant Globant and leaked tens of gigabytes of stolen data. The Lapsus$ extortion group claims to have hacked IT giant Globant and leaked roughly 70 Gb of stolen data. The gang claims that the company has implemented poor security practices that allowed them to hack their […]

Lapsus$ Globant

The Lapsus$ extortion group claims to have hacked IT giant Globant and leaked tens of gigabytes of stolen data.

The Lapsus$ extortion group claims to have hacked IT giant Globant and leaked roughly 70 Gb of stolen data. The gang claims that the company has implemented poor security practices that allowed them to hack their infrastructure.

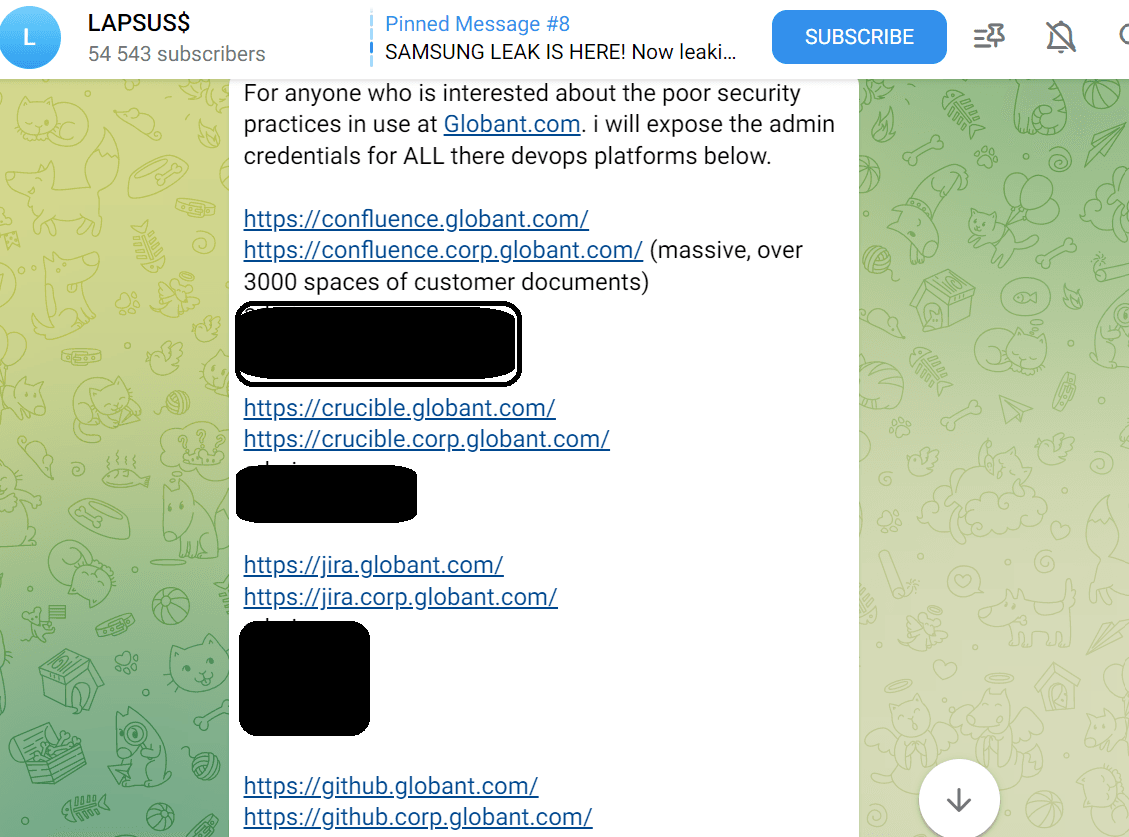
“For anyone who is interested about the poor security practices in use at Globant.com. i will expose the admin credentials for ALL there devops platforms below.” reads the message published on the Telegram Channel of the group.

Lapsus Globant

According to the gang, the stolen data includes customer source code and published a list of credentials to access source code sharing platforms used by the company, including GitHub, Jira, Crucible and Confluence.

Lapsus$ Globant 2

The hack of Globant comes a few days the City of London Police announced to have arrested seven teenagers suspected of being members of the notorious Lapsus$ extortion gang, which is believed to be based in South America. UK police suspect that a 16-year-old from Oxford is one of the leaders of the popular Lapsus$ extortion group.

Over the last months, the Lapsus$ gang compromised many prominent companies such as NVIDIA, Samsung, Ubisoft, Mercado Libre, Vodafone. Last week, the group announced the hack of Microsoft and Okta.

Follow me on Twitter: @securityaffairs and Facebook

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, Lapsus$)

[adrotate banner=”5″]

[adrotate banner=”13″]


