
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Lenovo fixes serious flaw in pre-installed Lenovo Solution Center

Lenovo fixed the Lenovo Solution Center, once again the company faces problems with pre-installed bloatware causing major security problems for users. Lenovo has fixed a security vulnerability in the Lenovo Solution Center (LSC) support tool that could be exploited by attackers to execute code with system privileges and take over the machine. Lenovo Solution Center […]

Lenovo fixes serious flaw in pre-installed Lenovo Solution Center

Lenovo fixed the Lenovo Solution Center, once again the company faces problems with pre-installed bloatware causing major security problems for users.

Lenovo has fixed a security vulnerability in the Lenovo Solution Center (LSC) support tool that could be exploited by attackers to execute code with system privileges and take over the machine.

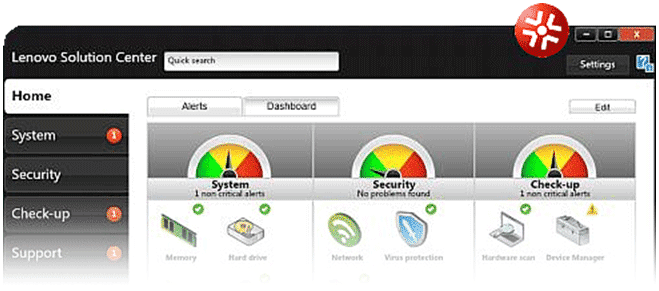
Lenovo Solution Center (LSC) software is pre-installed by Lenovo on many laptops and desktops, it is used by users to check their system information, manage updates and backups, check battery status, manage registration info and perform hardware tests.

The Lenovo Solution Center application is composed of two main components, the UI and the LSCTaskService service that always runs in the background.

Lenovo Solution Center

The company released on April 25 the Lenovo Solution Center version 3.3.002 that includes a fix for a local privilege escalation vulnerability reported by Trustwave. The flaw could be exploited by a local Windows user to run malicious code with system privileges and take over the computer.

“Vulnerabilities were identified within LSC’s backend service process that may allow a local user to execute arbitrary code with SYSTEM level privileges. In addition, a cross-site request forgery (CSRF) vulnerability exists that may allow exploitation of these vulnerabilities if a user opens a malicious  web site or crafted URL while the LSC backend service is running on a user’s machine.  The user’s computer may still be vulnerable even if the LSC user interface is not running.” reads the advisory from Lenovo”

This incident is the last in order of time that is related to flaw affecting software pre-installed by manufacturers on their PCs. In December, another flaw was discovered in the Lenovo LSC application.

It is important to note that in order to apply the fix users should download the latest version manually from the company website.

[adrotate banner=”9″]

Pierluigi Paganini

(Security Affairs – Lenovo, Lenovo Solution Center)


