
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Foreign adversary hacked email communications of the Library of Congress says

The Library of Congress discloses the compromise of some of its IT systems, an alleged foreign threat actor hacked their emails. The Library of Congress informed lawmakers about a security breach, an alleged foreign adversary compromised some of their IT systems and gained access to email communications between congressional offices and some library staff, including […]

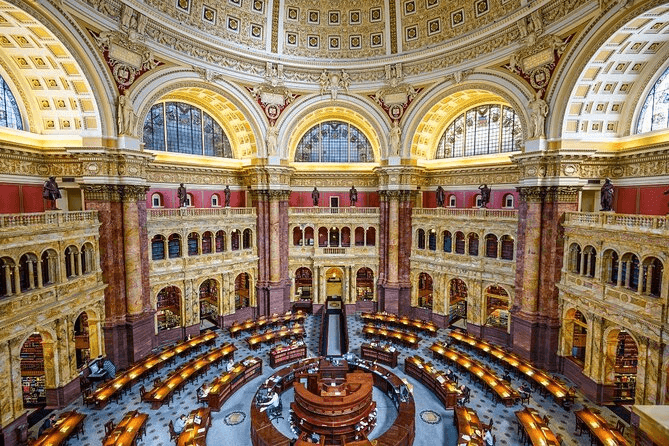
Library of Congress

The Library of Congress discloses the compromise of some of its IT systems, an alleged foreign threat actor hacked their emails.

The Library of Congress informed lawmakers about a security breach, an alleged foreign adversary compromised some of their IT systems and gained access to email communications between congressional offices and some library staff, including the Congressional Research Service.

Only email communications between congressional offices and some library staff, including the Congressional Research Service, from January to September, were affected.

The Library of Congress (LOC) is a research library in the federal national capital city of Washington, D.C. (District of Columbia), that serves as the library and research service for the two chambers of the United States Congress and the de facto national library of the United States of America. It also administers copyright law through the United States Copyright Office.

The Library of Congress notified law enforcement and the investigation is still ongoing.

The threat actor accessed email messages between January and September.

“An unidentified “adversary” hacked into the email system for the Library of Congress, accessing information sent via email between January and September 2024, the Library said.” reported the NBC News.

“The library shared news of the “cyber breach” with some Congressional offices, and NBC News obtained a copy of the message on Saturday morning. Law enforcement and the Capitol are investigating the hack. It is not yet clear who the adversary is or when precisely the hack took place.”

“The Library has mitigated the vulnerability that the adversary used to access the environment and has taken measures to prevent such incidents in the future,” reads a statement in the library’s notification.

The Library of Congress confirmed that House and Senate email networks, as well as the U.S. Copyright Office systems, were not impacted by the incident.

The library is investigating the incident to determine which email communications were compromised and impacted government officials and staff members.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, Congress)


