Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Doctor Web discovers the first Linux Trojan that is written in Rust language

Experts from Dr Web discovered a new Linux Trojan called Linux.BackDoor.Irc.16 that is written in the Rust programming language. It is a prolific period for Vxers working on Linux Trojan, a new strain was recently spotted by experts from Doctor Web. The new Linux Trojan has been named Linux.BackDoor.Irc.16 and is written in the Rust programming language.Rust […]

Doctor Web discovers the first Linux Trojan that is written in Rust language

Experts from Dr Web discovered a new Linux Trojan called Linux.BackDoor.Irc.16 that is written in the Rust programming language.

It is a prolific period for Vxers working on Linux Trojan, a new strain was recently spotted by experts from Doctor Web. The new Linux Trojan has been named Linux.BackDoor.Irc.16 and is written in the Rust programming language.Rust is a general-purpose, multi-paradigm, compiled programming language promoted by Mozilla Research. It is designed to be a “safe, concurrent, practical language.”

“Rust is a systems programming language that runs blazingly fast, prevents segfaults, and guarantees thread safety. “

“Unlike the majority of its counterparts, Linux.BackDoor.Irc.16 is written in Rust, a programming language whose creation was sponsored by Mozilla Research. ” reported Dr. Web in a blog post.

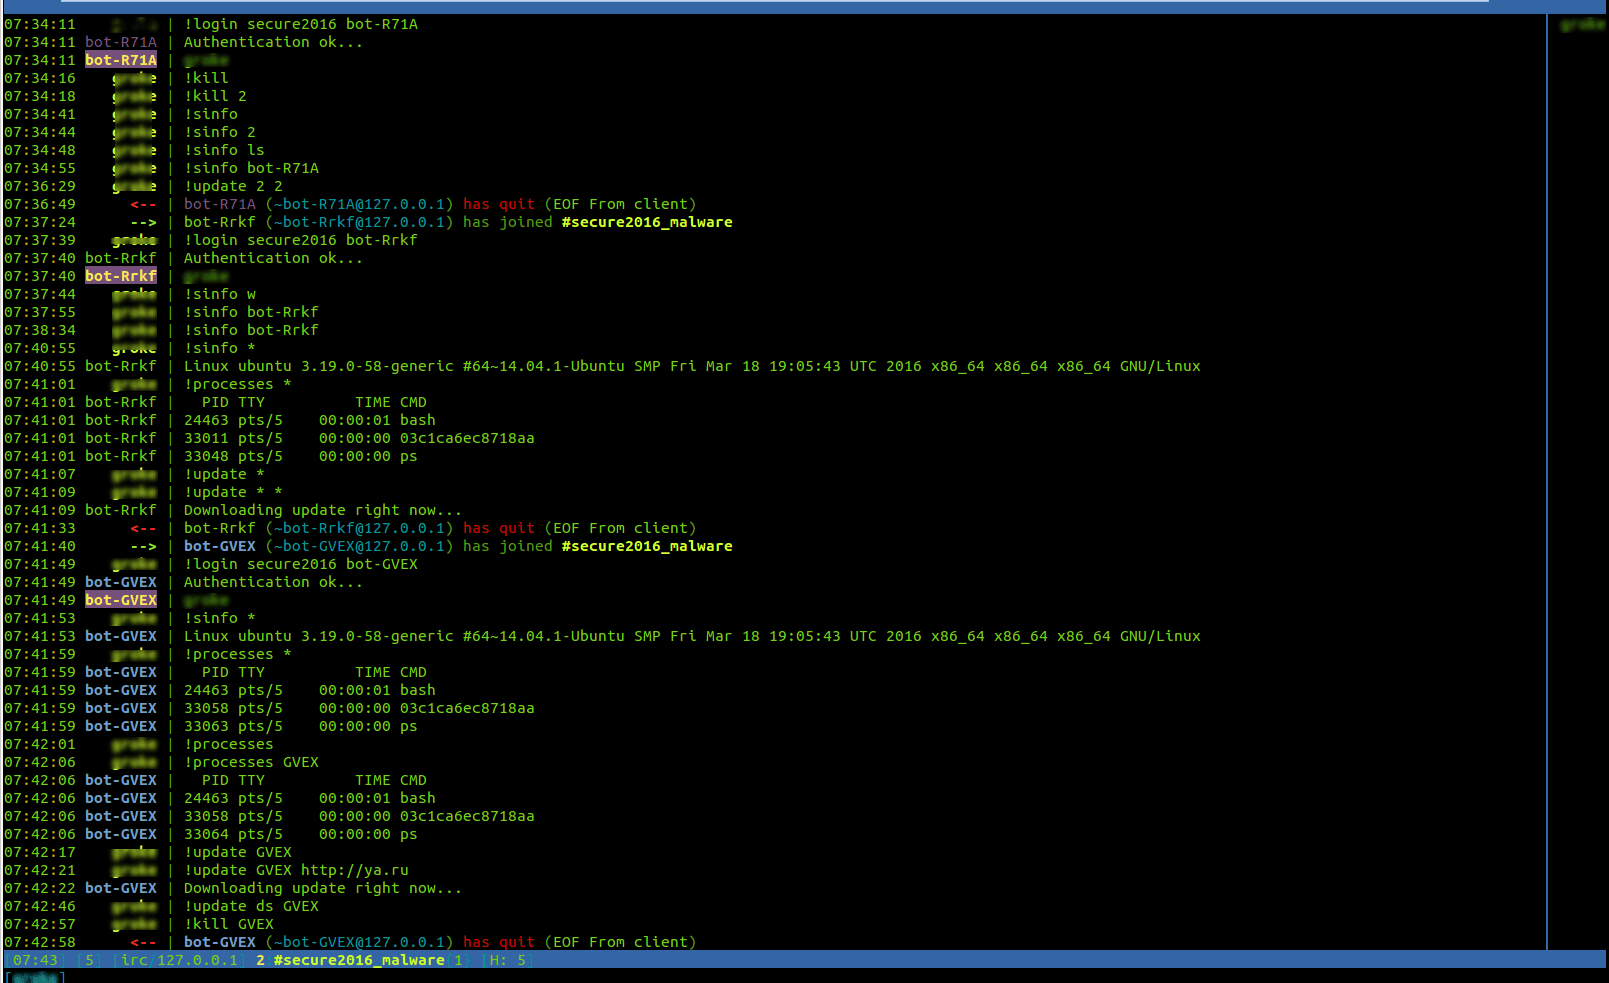
The Linux.BackDoor.Irc.16 Linux Trojan implements the features of a classical backdoor that allow attackers to remotely control the infected system by sending it via the IRC (Internet Relay Chat) protocol.

Once the Linux Trojan is executed it connects to a specific public chat channel that is indicated in its configuration, then it waits for commands.

linux trojan linux_backdoor_irc16-1

According to malware researchers from DrWeb, the Linux Trojan is able to execute just four commands:

  • Connect to a specified chat channel;
  • Gather information on the infected host and send them back to the crooks;
  • Send crooks data about the applications running in the system;
  • Delete itself from an infected machine;

The experts spotted a first stable version in 2015, according to Dr Web, the Linux.BackDoor.Irc.16 backdoor was designed to be a cross-platform malware. The experts who have analyzed the threat speculate it is a prototype for an ongoing project, they noticed in fact that it Linux Trojan is not able to replicate itself and the IRC channel used as C&C infrastructure are no more active.

“Doctor Web’s analysts believe that Linux.BackDoor.Irc.16 is, in fact, a prototype (Proof of Concept), because it cannot replicate itself, and the IRC channel used by the Trojan to receive commands from cybercriminals is not currently active.” reported Dr Web.

Recently other Linux malware were spotted in the wild by security experts such as the Linux.Rex.1 that is capable of self-spreading and create a peer-to-peer botnet and Linux.Lady that is used by crooks to mine cryptocurrency.

[adrotate banner=”9″]

Pierluigi Paganini

(Security Affairs – Linux.BackDoor.Irc.16,  Linux Trojan)