
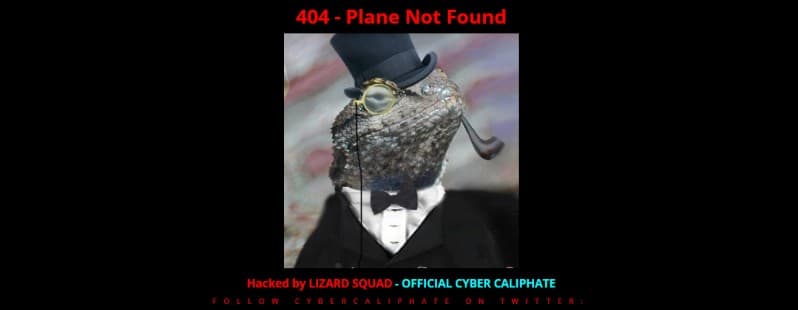
A joint operation of international law enforcement agencies allowed the arrest of suspected Lizard Squad Hackers in the US and Netherlands.
Law enforcement in the US and in the Netherlands have arrested last month two teenagers suspected of being members of the dreaded hacking groups Lizard Squad and PoodleCorp.
Both hacking teams are known for powerful DDoS DDoS attacks that shut down services of many companies in the gaming industry. The hacker successfully targeted the PlayStation Network, Xbox Live, EA and Blizzard.
Zachary Buchta (19), of Fallston, Maryland, and Bradley Jan Willem van Rooy (19), of Leiden, the Netherlands, have been charged with conspiracy to have hacked and damage protected computers.
“ZACHARY BUCHTA, 19, of Fallston, Md., and BRADLEY JAN WILLEM VAN ROOY, 19, of Leiden, the Netherlands, are charged with conspiring to cause damage to protected computers. The charges are the result of an international investigation into the computer hacking groups “Lizard Squad” and “PoodleCorp,” according to a criminal complaint and affidavit filed in U.S. District Court in Chicago.” reads the announcement issued by the US Department of Justice “Buchta and van Rooy allegedly conspired with others to launch destructive cyber attacks around the world, and trafficked payment accounts that had been stolen from unsuspecting victims in Illinois and elsewhere.”
In addition to the charges, the authorities seized the domains associated with the alleged conspiracy that are shenron.lizardsquad.org, lizardsquad.org, stresser.poodlecorp.org, and poodlecorp.org.

According to the US Department of Justice, Buchta used various online monikers, including “@fbiarelosers,” “pein,” “xotehpoodle” and “lizard,” while van Rooy was also known as “Uchiha,”“@UchihaLS,” “dragon” and “fox.”
They have been accused to have operated a platform offered for rent to users that used them to launch distributed denial-of-service (DDoS) attacks.
The authorities also suspected the duo were selling stolen payment card data on the black market.
The two teenagers face a sentence of up to 10 years.
The complaint also refers two other individuals, alleged members of the Lizard Squad and PoodleCorp crews, known with the online monikers “Chippyshell” and “AppleJ4ck.”
According to the complaint, Buchta used the @fbiarelosers account, which exchanged private message with other members of LizardSquad via Twitter discussing DDoS attacks.
Records from Comcast demonstrated that the suspect’s IP connected to an overseas VPN service that had been used to access the @fbiarelosers account and the websites managed by the both Lizard Squad and PoodleCorp groups.
The other suspect, Van Rooy, did not use any precaution to hide his IP while accessing his Twitter accounts that were also used by Lizard Squad.
Stay Tuned.
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(Security Affairs – Lizard Squad, cybercrime)
[adrotate banner=”5″]
[adrotate banner=”13″]


