
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

LockBit ransomware gang claims the attack on the sandwich chain Subway

The LockBit ransomware gang claimed to have hacked Subway, the American multinational fast food restaurant franchise.  Subway IP LLC is an American multinational fast-food restaurant franchise that specializes in submarine sandwiches (subs), wraps, salads, and drinks. The Lockbit ransomware group added Subway to the list of victims on its Tor data leak site and threatened to leak […]

Lockbit ransomware Subway

The LockBit ransomware gang claimed to have hacked Subway, the American multinational fast food restaurant franchise. 

Subway IP LLC is an American multinational fast-food restaurant franchise that specializes in submarine sandwiches (subs), wraps, salads, and drinks.

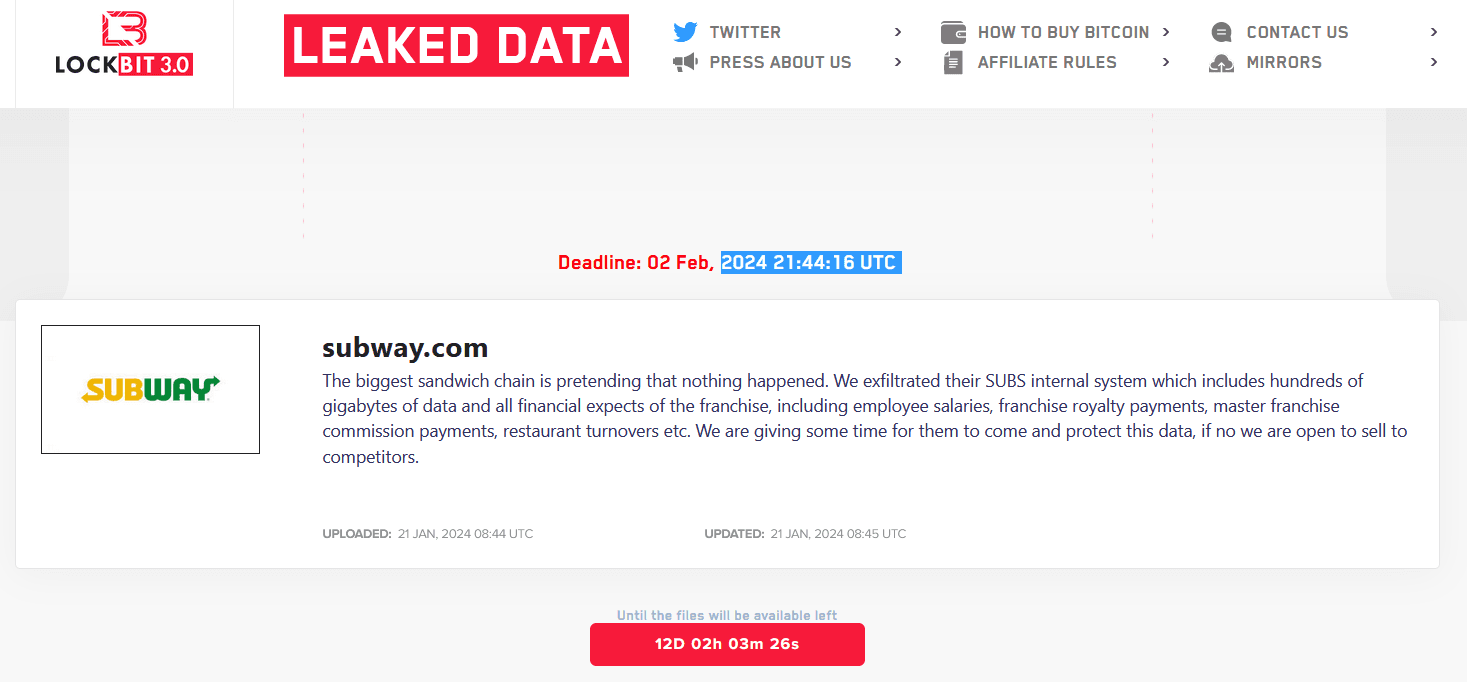
The Lockbit ransomware group added Subway to the list of victims on its Tor data leak site and threatened to leak the stolen data on February 02, 2024 at 21:44:16 UTC. The group claims to have stolen hundreds of gigabytes of sensitive data. The gang said that stolen data includes employee salaries, franchise royalty payments, master franchise commission payments, restaurant turnovers, and more

“The biggest sandwich chain is pretending that nothing happened. We exfiltrated their SUBS internal system which includes hundreds of gigabytes of data and all financial expects of the franchise, including employee salaries, franchise royalty payments, master franchise commission payments, restaurant turnovers etc. We are giving some time for them to come and protect this data, if no we are open to sell to competitors.” reads the message published on the Tor leak site.

Lockbit ransomware Subway

At this time, it is unknown what ransom the Lockbit group has demanded from the victim.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, ransomware)


