
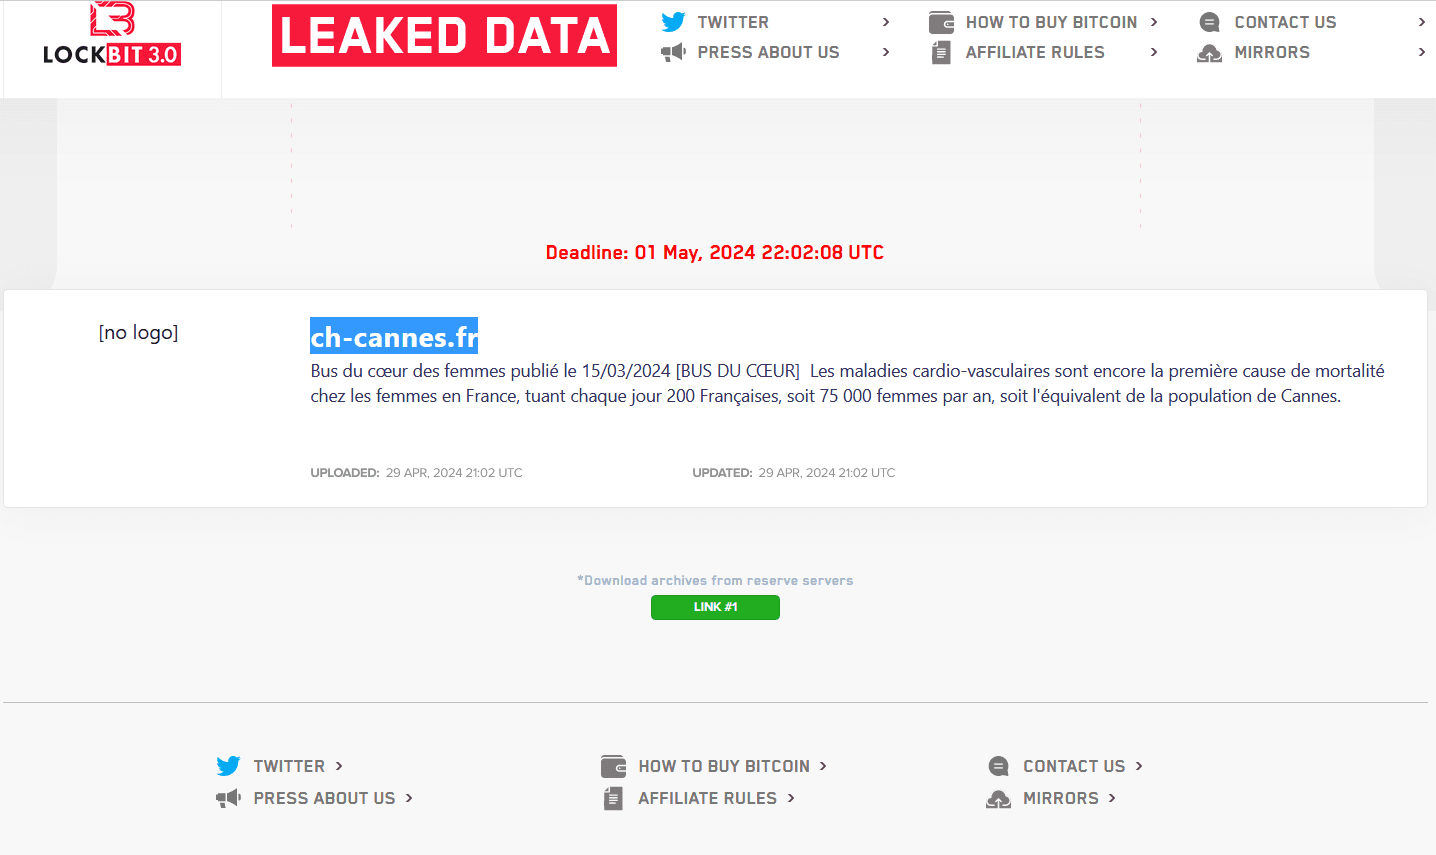
LockBit ransomware operators have published sensitive data allegedly stolen from the Simone Veil hospital in Cannes.
In April, a cyber attack hit the Hospital Simone Veil in Cannes (CHC-SV), impacting medical procedures and forcing personnel to return to pen and paper.
Non-urgent surgical procedures and consultations scheduled at the time of the attack were postponed.
The French hospital was forced to take all computers offline while the telephone lines were not impacted The hospital is investigating the incident with the help of ANSSI, Cert Santé, Orange CyberDéfense, and GHT06.
The Hospital Simone Veil in Cannes is a public hospital located in Cannes, France. The hospital provides a range of medical services and healthcare facilities to the local community and surrounding areas.
CHC-SV has more than 2,000 employees and has a capacity of more than 800 beds.
The LockBit ransomware group claimed responsibility for the attack and on May 1st published stolen confidential data after the hospital refused to pay the ransom.

Yesterday the Cannes Simone Veil hospital center published a statement on its website to confirm that the data published by the ransomware group belongs to it.
“The qualification of the exfiltrated data continues and detailed and personalized feedback will be provided in the coming days to the people and institutions concerned. This feedback will also include cybersecurity advice to follow in these circumstances. Accompanied by CERT-Santé and various partners specializing in cybersecurity, the management of the hospital center confirms having filed a complaint and is actively contributing to the ongoing investigation. An alert was also sent to the CNIL and ANSSI.” reads the statement. “Furthermore, the hospital’s activity has resumed its almost normal course. The normal functioning of its information system is being restored at a sustained pace in accordance with the action plan defined at the start of the crisis.”
In the past, other French hospitals were victims of cyber attacks.
In December 2022, the Hospital Centre of Versailles was hit by a cyber attack that forced it to cancel operations and transfer some patients in other hospitals.
In August 2022, the Center Hospitalier Sud Francilien (CHSF), a hospital southeast of Paris, suffered a ransomware attack over the weekend. The attack disrupted the emergency services and surgeries and forced the hospital to refer patients to other structures. According to local media, threat actors demand a $10 million ransom to provide the decryption key to restore encrypted data.
Follow me on Twitter: @securityaffairs and Facebook
(SecurityAffairs – hacking, ransomware)


