
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

LockBit ransomware gang hit the Commission des services electriques de Montréal (CSEM)

The LockBit ransomware gang claims to have breached the Commission des services electriques de Montréal (CSEM). The LockBit ransomware group continues to be one of the most active extortion gangs in the threat landscape. This week the gang claimed to have hacked the Commission des services electriques de Montréal (CSEM). The Commission des services électriques […]

Lockbit ransomware

The LockBit ransomware gang claims to have breached the Commission des services electriques de Montréal (CSEM).

The LockBit ransomware group continues to be one of the most active extortion gangs in the threat landscape. This week the gang claimed to have hacked the Commission des services electriques de Montréal (CSEM).

The Commission des services électriques de Montréal (CSEM) is a public agency responsible for the undergrounding of electrical wires in the city of Montreal, Quebec, Canada. It was created in 1910 by a partnership between the city and the private sector.

The CSEM’s mission is to provide a safe, reliable, and sustainable underground electrical network for the city of Montreal. The main activities carried out by the organization are planning and coordinating the undergrounding of electrical wires, managing and maintaining the underground electrical network, and providing information and education about underground electrical networks.

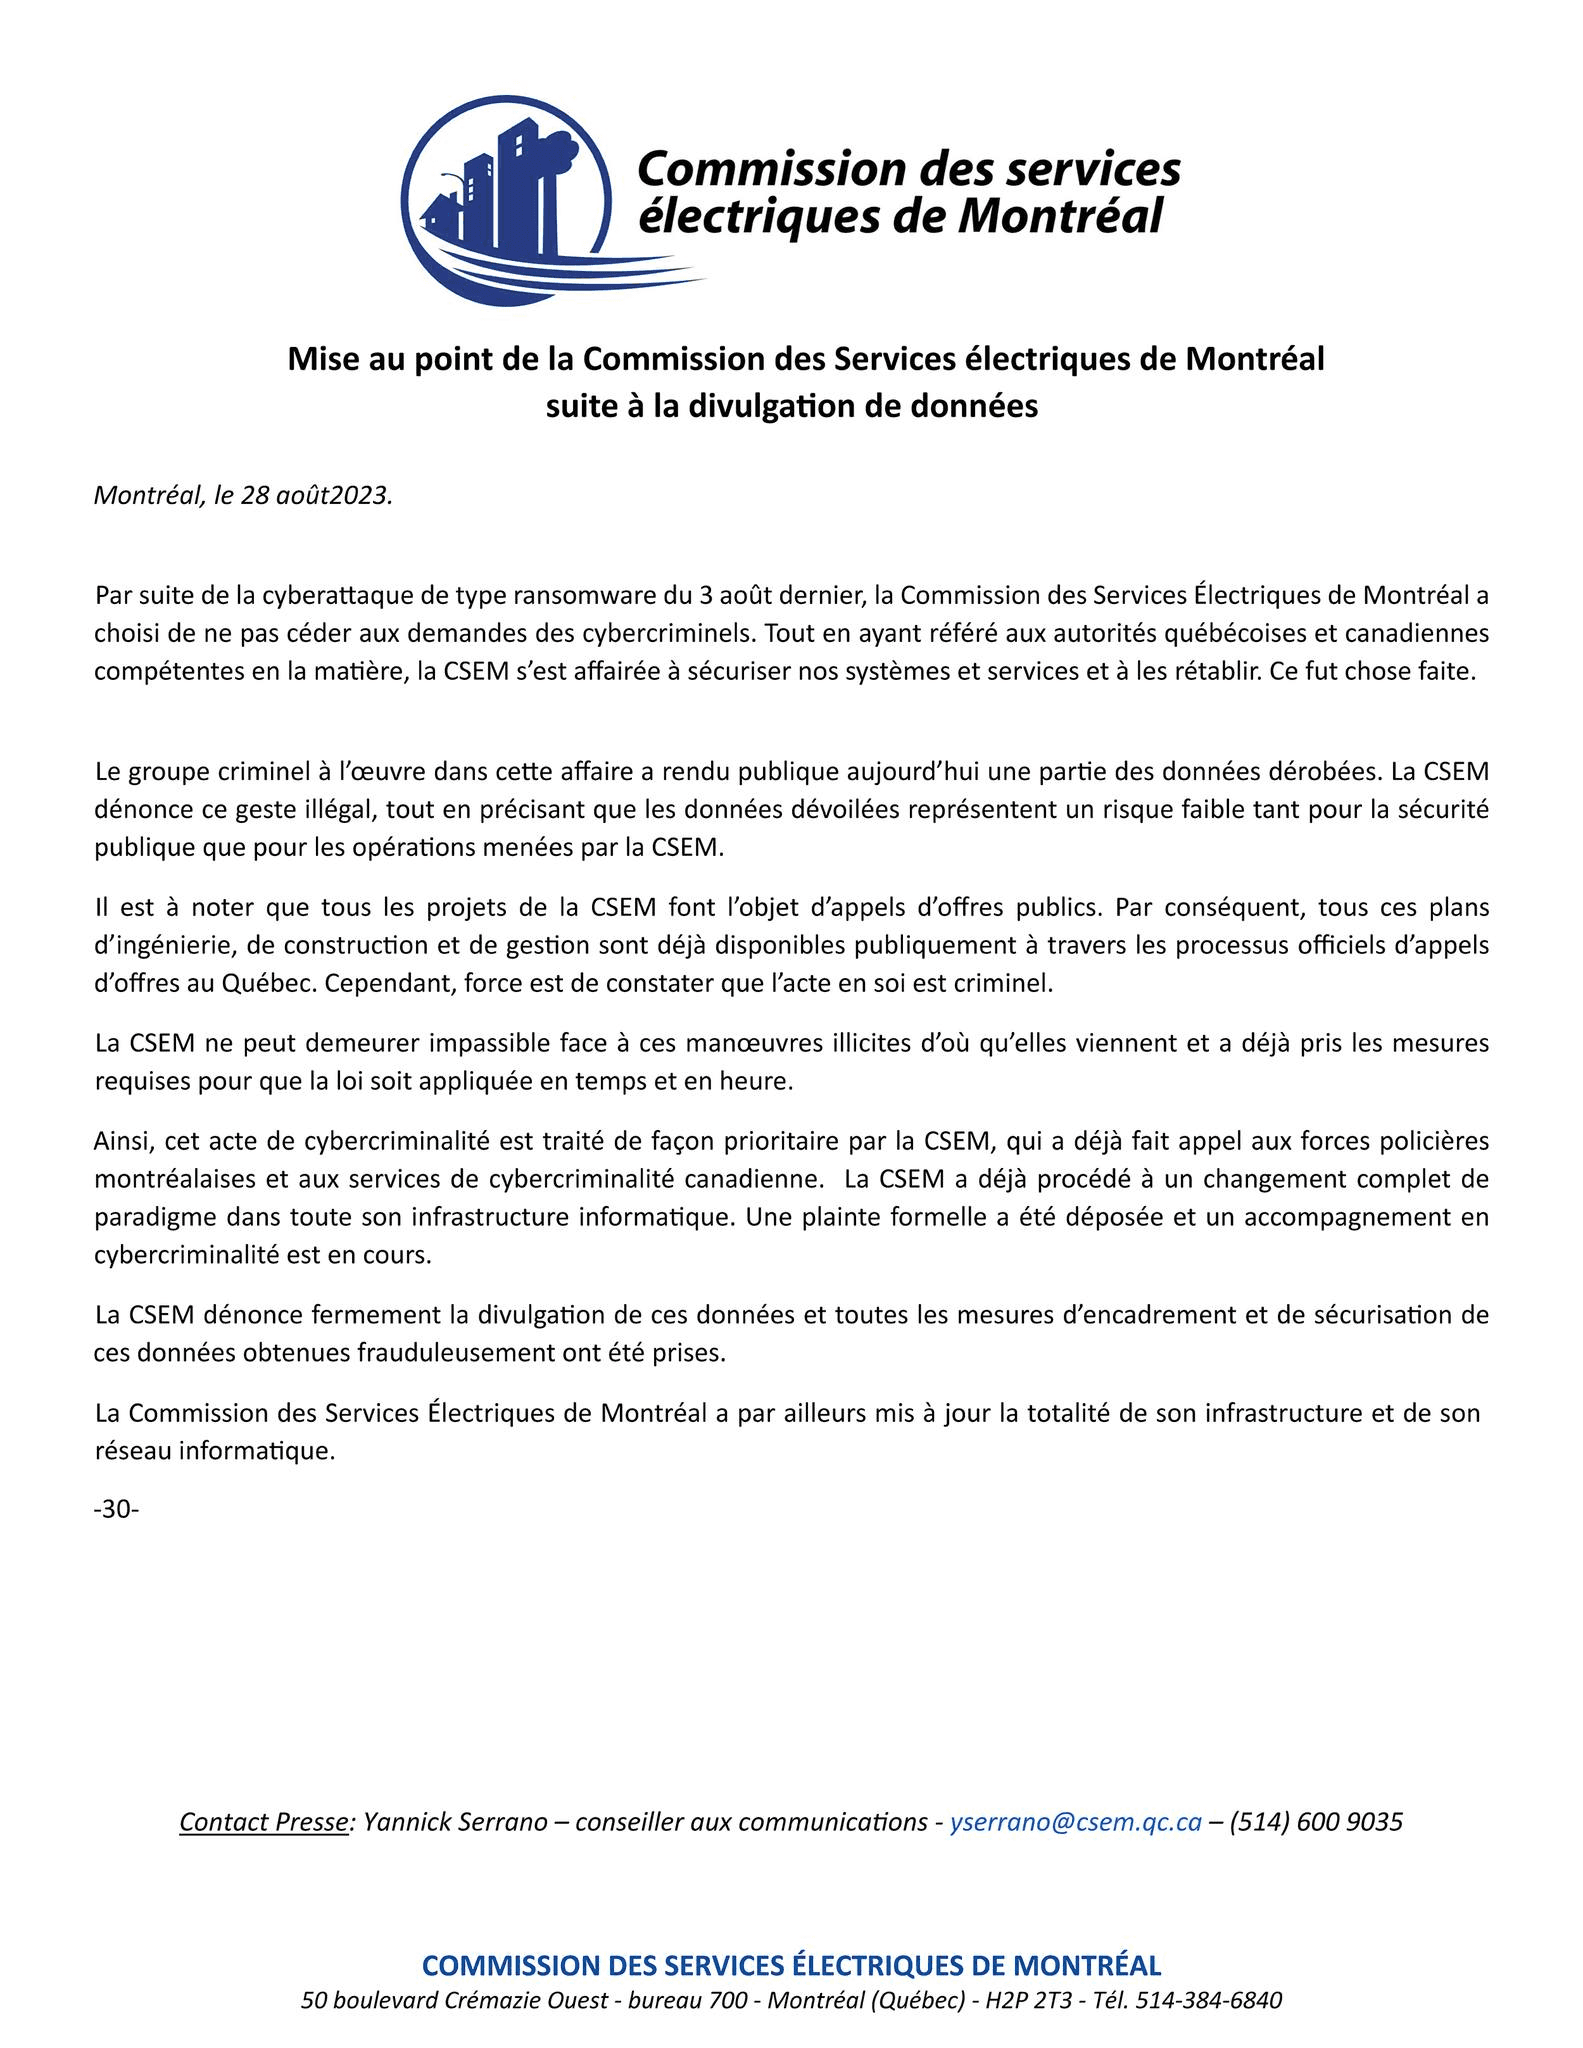
CSEM confirmed the security breach, the company confirmed the attack took place on August 3rd, 2023. The Canadian company confirmed that it has refused to pay the ransom.

The organization immediately launched an investigation into the security breach with the help of law enforcement in Quebec. At the time of this writing, CSEM has recovered impacted systems.

The LockBit ransomware group published the stolen data on August 30, 2023.

The organizations attempted to downplay the impact of the security breach explaining that CSEM projects are the subject of public documents.

“It should be noted that all CSEM projects are the subject of public documents. Therefore, all these plans – engineering, construction and management – are already publicly available through the official process offices in Quebec.” states the company.

Since August 1st, the LockBit 3 operation has already hit 140 organizations worldwide.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, Lockbit 3.0)


