
Security Affairs
CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|FBI Blames North Korea for $6 Billion Binance Crypto Theft|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|FBI Blames North Korea for $6 Billion Binance Crypto Theft|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

LockBit ransomware gang claims to have stolen data from PayBito crypto exchange

LockBit ransomware gang claims to have stolen customers’ data from the PayBito crypto exchange. PayBito is a bitcoin and cryptocurrency exchange for major cryptocurrencies including Bitcoin Cash, Bitcoin, Ethereum, HCX, Litecoin, Ethereum Classic. The exchange is operated by global blockchain and IT services company HashCash. LockBit ransomware operators claim to have stolen customers’ data from the PayBito crypto exchange, […]

lockbit paybito

LockBit ransomware gang claims to have stolen customers’ data from the PayBito crypto exchange.

PayBito is a bitcoin and cryptocurrency exchange for major cryptocurrencies including Bitcoin Cash, Bitcoin, Ethereum, HCX, Litecoin, Ethereum Classic. The exchange is operated by global blockchain and IT services company HashCash.

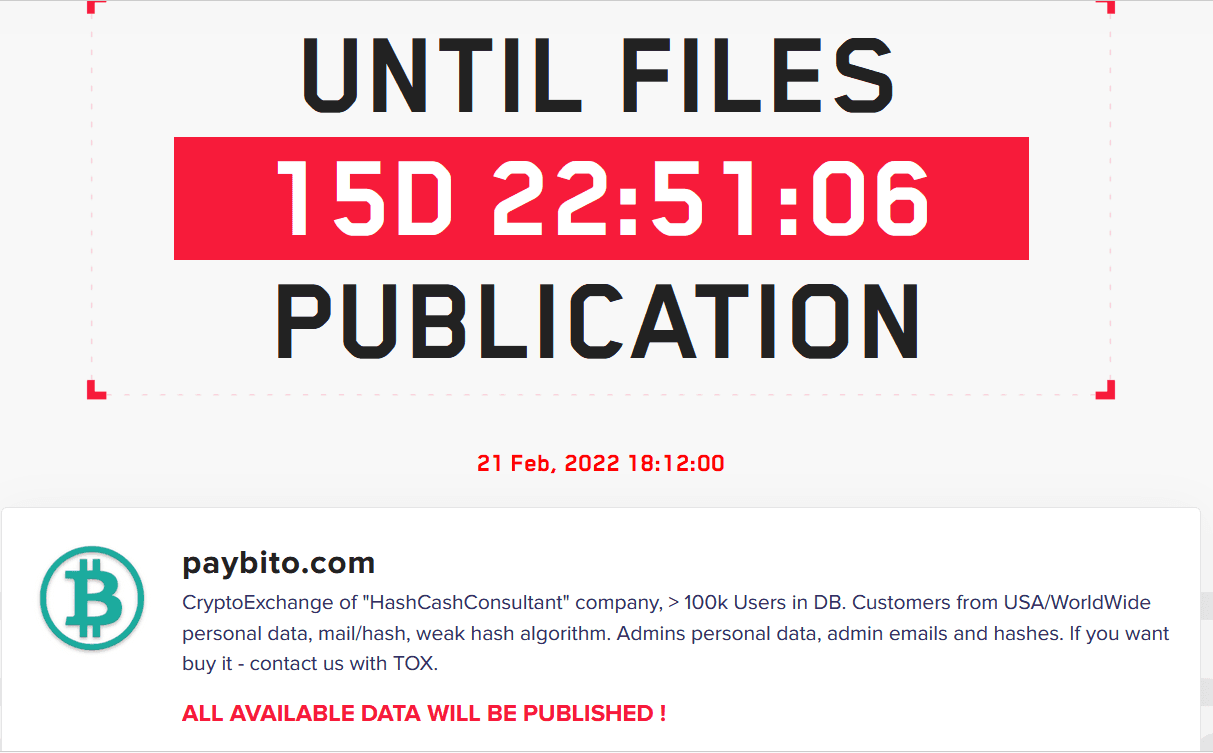
LockBit ransomware operators claim to have stolen customers’ data from the PayBito crypto exchange, the name of the company was published on the gang’s Tor leak site.

“CryptoExchange of “HashCashConsultant” company, > 100k Users in DB. Customers from USA/WorldWide personal data, mail/hash, weak hash algorithm. Admins personal data, admin emails and hashes. If you want buy it – contact us with TOX.” reads the announcement published on the leak site.

lockbit paybito

Lockbit ransomware operators claim to have stolen a database containing personal data belonging to more than 100,000 customers worldwide.

The group also claims to have stolen email and password hashes that can be easily decrypted due to the use of a “weak hash algorithm.” The group also stole the admin’s personal data.

Stolen data will be published on February 21st, 2022 if the company will not pay the ransom.

The LockBit ransomware gang has been active since September 2019, in June 2021 the group announced the LockBit 2.0 RaaS. Like other ransomware gangs, Lockbit 2.0 determines the system and
user language settings and only targets those not matching a set list of languages that are
Eastern European.

After ransomware ads were banned on hacking forum, the LockBit operators set up their own leak site promoting the latest variant and advertising the LockBit 2.0 affiliate program. 

This week, the FBI released a flash alert containing technical details associated with the LockBit ransomware operation.

Follow me on Twitter: @securityaffairs and Facebook

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, PayBito)

[adrotate banner=”5″]

[adrotate banner=”13″]


