
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Bitdefender releases Universal LockerGoga ransomware decryptor

Bitdefender has released a free decryptor to allow the victims of the LockerGoga ransomware to recover their files without paying a ransom. The cybersecurity firm Bitdefender has released a free decryptor to allow LockerGoga ransomware victims to recover their encrypted files without paying a ransom. “We’re pleased to announce the availability of a new decryptor […]

LockerGoga ransomware decryptor

Bitdefender has released a free decryptor to allow the victims of the LockerGoga ransomware to recover their files without paying a ransom.

The cybersecurity firm Bitdefender has released a free decryptor to allow LockerGoga ransomware victims to recover their encrypted files without paying a ransom.

“We’re pleased to announce the availability of a new decryptor for LockerGoga, a strain of ransomware that rose to fame in 2019 with the attack of the Norsk Hydro company.” reads the announcement published by the security firm. “The new decryptor is a joint effort between Bitdefender, Europol, the NoMoreRansom Project, the Zürich Public Prosecutor’s Office and the Zürich Cantonal Police.”

LockerGoga ransomware decryptor

The company developed the tool with the help of international law enforcement agencies, including Europol, the Zürich Public Prosecutor’s Office, and the Zürich Cantonal Police.

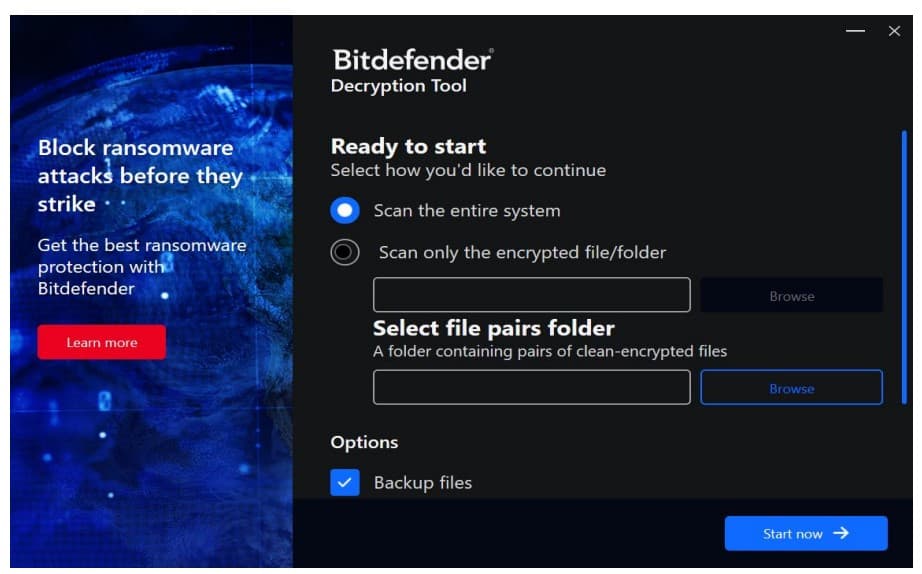
In order to decrypt the files, users have to provide the path containing pairs of clean-encrypted files.

The decryptor can scan your entire file system or single files or folders.

The tool can also be executed silently via a command line, this feature was implemented to
automate the deployment of the tool inside a large network.

The decryptor has the “backup files” feature, enabled by default that could be used in case there will be any problem with the decryption process.

The LockerGoga ransomware operation has been active since January 2019, it targeted organizations worldwide, including the aluminum giant Norsk Hydro.

The ransomware gang was dismantled in October 2021 with the arrest of its operators and the seizure of the systems containing the master private keys used in the encryption process.

“Its operator, who has been detained since October 2021 pending trial, is part of a larger cybercrime ring that used LockerGoga and MegaCortext ransomware to infect more than 1,800 persons and institutions in 71 countries to cause an estimated damage of $US 104 million.” continues the announcement.

Therefore, this decryptor will mostly be for past victims who refused to pay the ransom and have been waiting to recover their files for free.

Follow me on Twitter: @securityaffairs and Facebook

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, LockerGoga ransomware)

[adrotate banner=”5″]

[adrotate banner=”13″]


