
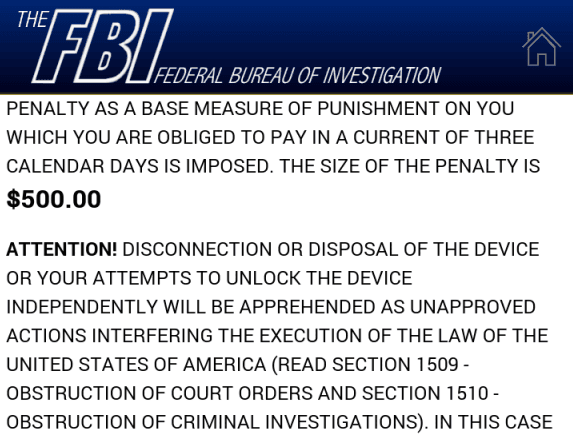
Lockerpin is the first known Android lock-screen ransomware to set a phone’s PIN lock that is targeting mainly US mobile users.
Once again here we are to discuss a new mobile ransomware, this time the malicious Android app dubbed Android/Lockerpin.A locks out victims by changing lock screen PIN until owners pay a $US500 ransom.
Android/Lockerpin.A, the app first tricks users into granting it administrator privileges by displaying a bogus patch installation window on top of an activation notice.

When victims click on the “continue” button, they grant the malicious app the administrator privileges which allow the app to modify the Android settings.
The Lockerpin ransomware changes the PIN used to unlock the screen lock, then the user only can do a factory reset to regain control over the smartphone.
“The trojan app has obtained administrator rights silently and now can lock [the] device—and even worse, it set[s] a new PIN for the lock screen. Not long after, the user will be prompted to pay a $US500 ransom for allegedly viewing and harboring forbidden pornographic material.” wrote in a blog post Lukas Stefanko, researcher at Eset firm.
Differently from other ransomware, restarting the mobile device in safe mode will not allow the owner to disable the malicious Lockerpin app. According to ESET, Lockerpin is the first known Android lock-screen ransomware to set a phone’s PIN lock. It relies on the fear of the users to lose all of their data due to the factory reset.
“In previous Android LockScreen Trojans, the screen-locking functionality was usually achieved by constantly bringing the ransom window to the foreground in an infinite loop. While various self-defense mechanisms were implemented to keep the device user locked out, it wasn’t too difficult to get rid of the malware thus unlocking the device by using Android Debug Bridge (ADB) or deactivating Administrator rights and uninstalling the malicious application in Safe Mode.” continues the post.
Lockerpin is distributed through third-party app stores and masquerades as an app for providing adult content.
According to data provided by ESET, most of the infected Android devices are in the USA (75%), with a percentage share of over 75 per cent.
“This is part of a trend where Android malware writers are shifting from mostly targeting Russian and Ukrainian users to largely targeting victims in America, where arguably they can make bigger profits.” states ESET.
When malware is spread through official channels, App store and Play store, the situation could be much more dangerous for users due to the larger audience impacted as happened recently with the Android Adult Player malicious app.
(Security Affairs – Lockerpin, ransomware)


