
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

A new LOCKY ransomware campaign targets the healthcare

Malware researchers at FireEye security firm have spotted a new Locky ransomware campaign mainly  targeting the healthcare sector. Security experts from FireEye have spotted a Locky ransomware campaign mainly targeting the healthcare sector, Telecom and Transportation industries. Attackers launched  a massive phishing campaign to deliver the threat. The campaign bit organizations worldwide, mostly in the US, […]

A new LOCKY ransomware campaign targets the healthcare

Malware researchers at FireEye security firm have spotted a new Locky ransomware campaign mainly  targeting the healthcare sector.

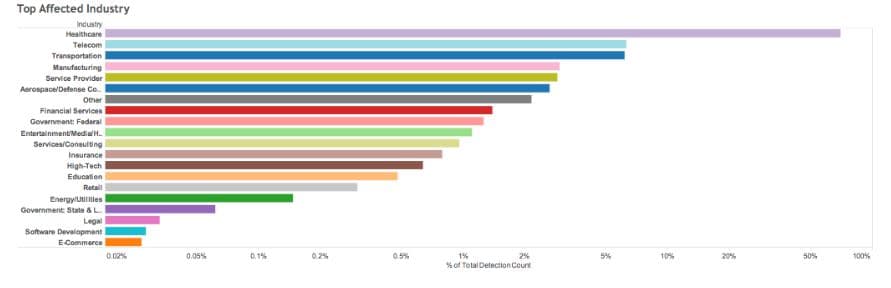
Security experts from FireEye have spotted a Locky ransomware campaign mainly targeting the healthcare sector, Telecom and Transportation industries.

Locky campaign August healthcare 2

Attackers launched  a massive phishing campaign to deliver the threat. The campaign bit organizations worldwide, mostly in the US, Japan, South Korea.

Threat actors behind this Locky campaign leveraged on DOCM FORMAT email attachments to deliver the ransomware, instead Javascript based downloaders.

“From our trend analysis, Locky ransomware started being delivered via DOCM format email attachments more extensively beginning in August. This marks a change from the large campaigns we observed in March, where a JavaScript based downloader was generally being used to infect systems.” reads the report published by FireEye.

“These detection spikes and change in tactics suggest that the cybercriminals are investing more to infect systems and maximize their profits. Additionally, we have observed that the delivery of Dridex via this distribution channel seems to have stopped, or nearly so, which could explain why we are seeing the Locky uptick.”

The researchers believe crooks are investing to compromise systems maximizing their efforts. Another interesting trend reported by FireEye is the pause in the distribution of the Dridex banking Trojan through the same channel.

Experts noticed many similarities in the macro code used by Attackers in three distinct Locky campaigns running on Aug. 9, Aug. 11 and Aug. 15.

The following are the key comparisons:

  1. Each email campaign has a specific “one-off” campaign code that is used to download the Locky ransomware payload from the malicious malware server.
  2. The malicious URL embedded within macro code is encoded using the same encoding function, but with a different key for each campaign. Each character is encoded by multiplying its ASCII code with a specified key (an integer). Hence, its decoder would perform a division using the specified integer.
  3. The downloaded payload is encoded using 32 bytes rolling XOR key. A different key is used for each campaign. Rolling XOR is described as follows:

Plain [i] = Cipher [i] ^ Key [i % length of Key], where Plain is the computed plain text, Cipher is the cipher text, Key is the xor key, and i is the byte offset.

The evidence collected by the researchers suggest the involvement of a single or multiple attackers in a coordinated effort.

[adrotate banner=”9″]

Pierluigi Paganini

(Security Affairs – Locky Ransomware, critical infrastructure)


