
Security Affairs
U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Prototype Pollution flaw discovered in all versions of Lodash Library

Liran Tal, a developer advocate at open-source security platform Snyk, discovered a high-severity prototype pollution security flaw that affects all versions of lodash. Lodash is a JavaScript library which provides utility functions for common programming tasks using the functional programming paradigm. Liran Tal, a developer advocate at Snyk, discovered a high-severity prototype pollution vulnerability, tracked as CVE-2019-10744, that affects all […]

lodash prototype pollution

Liran Tal, a developer advocate at open-source security platform Snyk, discovered a high-severity prototype pollution security flaw that affects all versions of lodash.

Lodash is a JavaScript library which provides utility functions for common programming tasks using the functional programming paradigm.

Liran Tal, a developer advocate at Snyk, discovered a high-severity prototype pollution vulnerability, tracked as CVE-2019-10744, that affects all versions of Lodash.

The flaw could be exploited by hackers to compromise the security of affected services using the library.

The popular library is currently used in more than 4 million projects on GitHub.

Liran Tal also developed a proof-of-concept exploit for the flaw.

“The popular npm library is used by 4.35 million projects on GitHub alone. Just shy of 40k GitHub project stars, the library is downloaded over 80 million times each month. Needless to say, a high severity vulnerability in a library as popular as lodash affects a large proportion of npm users.” reads a blog post published by the company.

Prototypes are used to define a JavaScript object’s default structure and default values, they are essential to specify an expected structure when no values are set.

An attacker that is able to modify a JavaScript object prototype can make an application crash and change behavior if it doesn’t receive the expected values.

Due to the diffusion of JavaScript, the exploitation of prototype pollution flaws could have serious consequences on web applications.

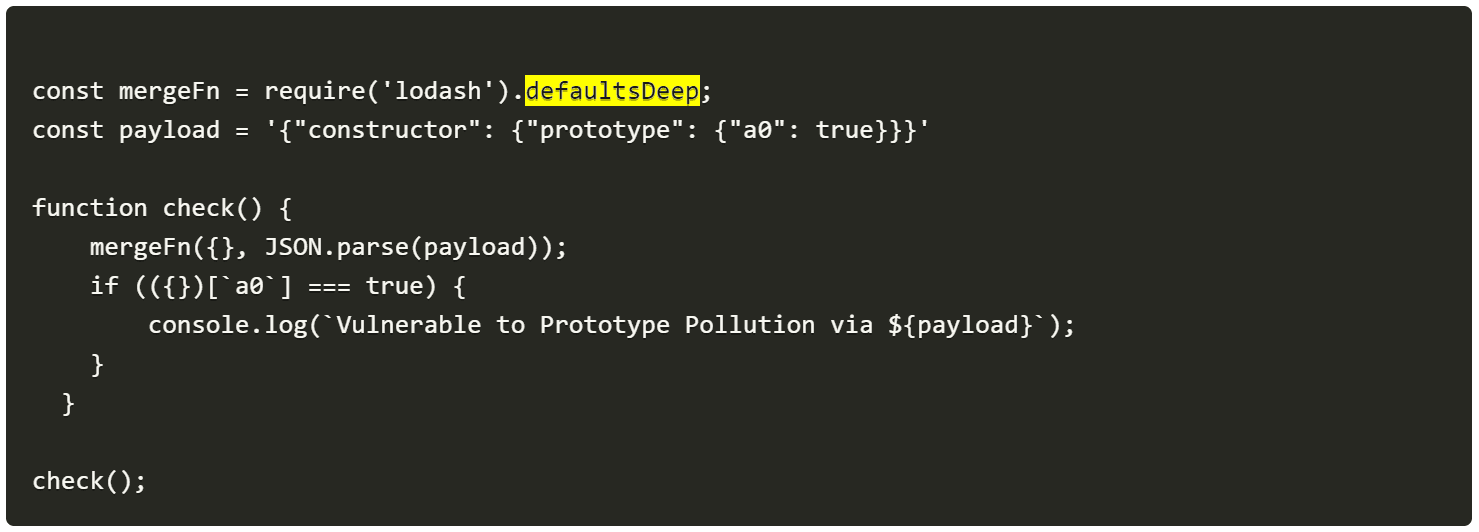
Tal discovered that the “defaultsDeep” function implemented in the Lodash library could be tricked into adding or modifying properties of Object.prototype using a constructor payload. In this way it is possible to force crashing the web application or altering its behavior.

lodash prototype pollution

Tal shared his findings with John Dalton, maintainer of lodash.

“The process included a collaboration with John in a private repository to confirm our findings and Snyk’s proposed fixes to remediate the vulnerabilities. Involved in this process was Kirill, one of Snyk’s software engineers, who raised pull requests ([1], [2]) with the fixes to lodash, both of which were merged on June 24th.” wrote the expert.

In April, experts at Snyk discovered another rare prototype pollution vulnerability in the popular jQuery JavaScript library that could allow attackers to modify a JavaScript object’s prototype.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – Lodash, hacking)

[adrotate banner=”5″]

[adrotate banner=”13″]


