Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Experts monitor ongoing attacks using exploits for Log4j library flaws

Researchers from DrWeb monitored attacks leveraging exploits for vulnerabilities in the Apache Log4j library Researchers from DrWeb monitored attacks leveraging exploits for vulnerabilities (CVE-2021-44228, CVE-2021-45046, CVE2021-4104, and CVE-2021-42550) in the Apache Log4j library warning of the need to adopt protective measures. The vulnerabilities can allow threat actors to execute arbitrary code on the target systems, […]

log4j

Researchers from DrWeb monitored attacks leveraging exploits for vulnerabilities in the Apache Log4j library

Researchers from DrWeb monitored attacks leveraging exploits for vulnerabilities (CVE-2021-44228, CVE-2021-45046, CVE2021-4104, and CVE-2021-42550) in the Apache Log4j library warning of the need to adopt protective measures.

The vulnerabilities can allow threat actors to execute arbitrary code on the target systems, trigger a Denial of Service condition, or disclose confidential information.

Dr. Web set up one of its honeypots to analyze the impact of the Log4J vulnerabilities on systems exposed online and discovered an intense activity between December 17th-20th.

log4j

“We record attacks using exploits for the vulnerabilities on one of our honeypots–a special server used by Doctor Web specialists as bait for fraudsters. The most active threat occurred between December 17th-20th, but attacks still continue.” reads the analysis published by DrWeb.

DayNumber of attacks
December 107
December 1120
December 1225
December 1315
December 1432
December 1521
December 1624
December 1747
December 1851
December 1933
December 2032
December 2114
December 2235
December 2336

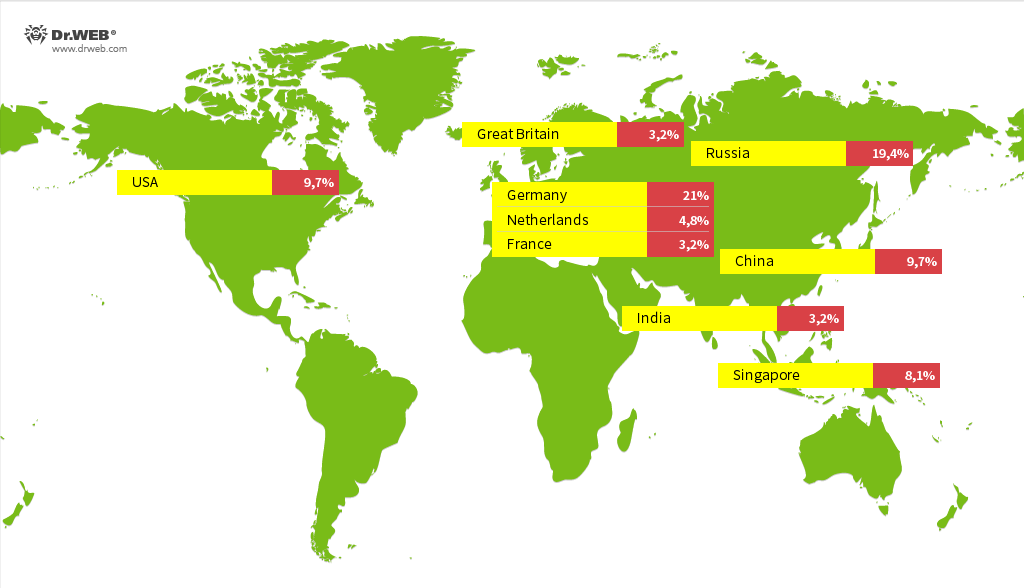
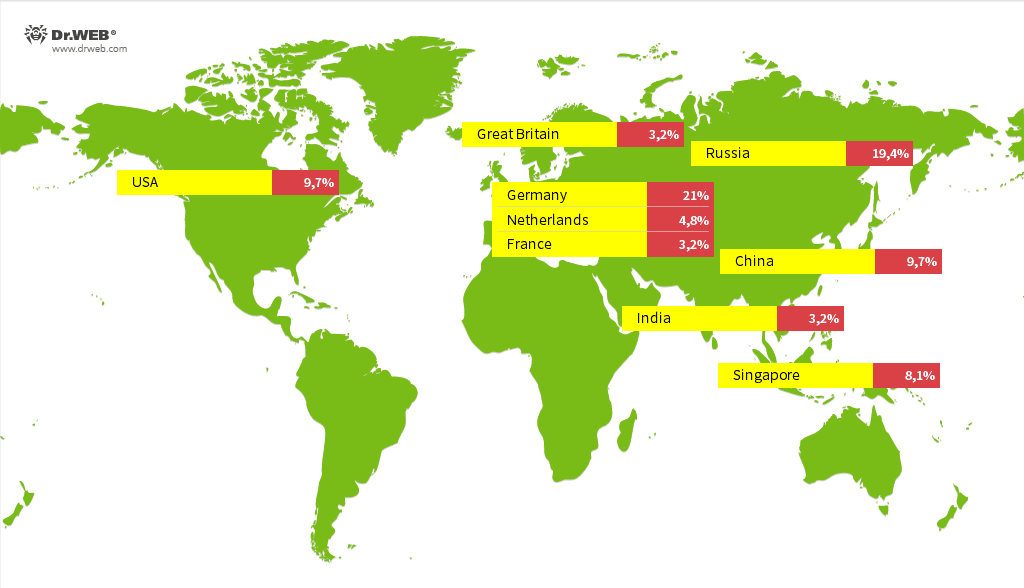
The attacks are carried out from 72 different IP addresses, most of them were German IP addresses (21%), followed by Russia (19.4%), the USA and China (9.7%).

log4j

Experts pointed out the difficulty in asses potentially vulnerable systems because some projects don’t have a direct dependence on Log4j.

“One way or another, vulnerabilities affect the performance of many projects worldwide. You need to closely watch the release of software updates that use the Log4j 2 library and install them as soon as possible.” concludes the experts.

Follow me on Twitter: @securityaffairs and Facebook

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, Log4j)

[adrotate banner=”5″]

[adrotate banner=”13″]