
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Lojas Renner, Brazilian largest clothing store chain, was hit by ransomware

Lojas Renner, the largest Brazilian department stores clothing company, suffered a ransomware attack that impacted its IT infrastructure. Lojas Renner, the largest Brazilian department stores clothing company, announced to have suffered a ransomware attack that impacted its IT infrastructure. According to Brazilian news outlets, the company was forced to shut down all its physical stores […]

Lojas Renner, Brazilian largest clothing store chain, was hit by ransomware

Lojas Renner, the largest Brazilian department stores clothing company, suffered a ransomware attack that impacted its IT infrastructure.

Lojas Renner, the largest Brazilian department stores clothing company, announced to have suffered a ransomware attack that impacted its IT infrastructure.

According to Brazilian news outlets, the company was forced to shut down all its physical stores across the country in response to the attack, but Lojas Renner denied having closed the stores and pointed out that the infection only impacted its e-store.

“The teams remain mobilized, executing the protection and recovery plan, with all their control and security protocols, and working to re-establish all company operations.” reads a statement from the company

Renner operates more than 600 stores across three countries under brands such as Renner, Camicado, Youcom, and Ashua.

The retailer also reported that its main databases were not impacted. 

“The company first disclosed the incident in a filing with the Brazilian stock market on Thursday.” reported the TheRecord website.

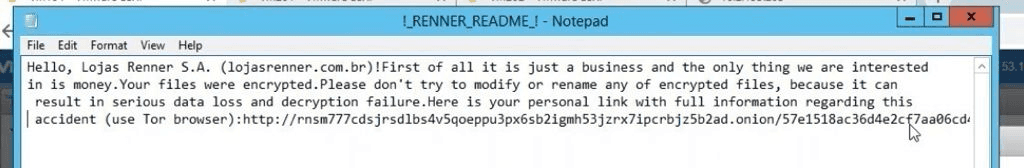
According to the Brazilian blog TecMundo, the attack against Lojas Renner was orchestrated by RansomExx operators.

Some experts speculated that the ransomware gang hit the company compromising one of its IT services providers, Tivit. However, Tivit explained it has not suffered any attacks on its infrastructure.

At the time of this writing, it is unclear if the retailer has suffered a data breach, the leak site of the RansomExx gang has yet to include the Brazilian group among the list of targeted organizations.

One possible reason is that there is an ongoing negotiation between the ransomware gang and the victim or because Renner opted to pay the ransom as reported by Cointimes.

“Information from unofficial sources said Renner paid R$20 million in cryptocurrencies as a ransom. Initially, the hacker group would have asked for US$1 billion, but after negotiations the amount was reduced (to US$20 million ).” reported the Cointimes.

Follow me on Twitter: @securityaffairs and Facebook

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, ransomware)

[adrotate banner=”5″]

[adrotate banner=”13″]


