
Security Affairs
U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Emsisoft releases the third decryptor in a few days, this time for LooCipher ransomware

Security experts at Emsisoft released the third decryptor in a few days, this time announced a free one for the LooCipher ransomware. A few days ago, the experts at Emsisoft released two free decryptors for the ZeroFucks ransomware and Ims00rry ransomware, now the malware team announced the released of a decryptor for the LooCipher ransomware. […]

LooCipher decryptor Emsisoft

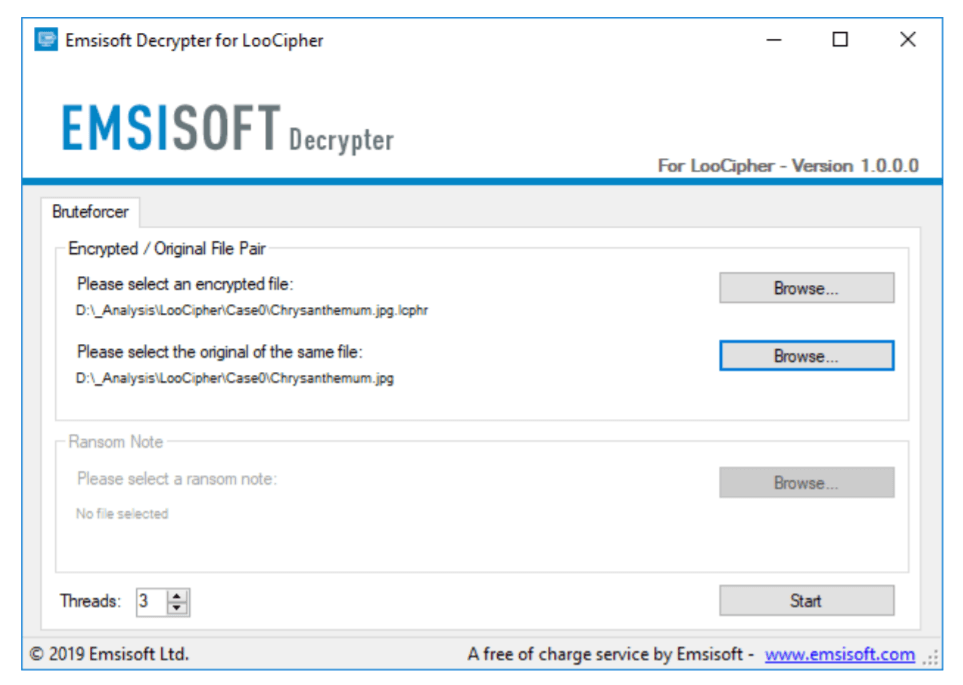
Security experts at Emsisoft released the third decryptor in a few days, this time announced a free one for the LooCipher ransomware.

A few days ago, the experts at Emsisoft released two free decryptors for the ZeroFucks ransomware and Ims00rry ransomware, now the malware team announced the released of a decryptor for the LooCipher ransomware.

Victims of the LooCipher ransomware don’t have to pay the ransom, they only need to download the decryptor from the link below:

Loocipher is a new threat that is rapidly spreading, its functionalities are pretty straight forward as effective, common to many other ransomware families.

Recently experts at Yoroi-Cybaze ZLab published a detailed analysis of the ransomware, below the key findings of the analysis:

  • The ransomware spreads using weaponized Word document.
  • The Command and Control is hosted on the TOR Network, at the following onion address “hxxp://hcwyo5rfapkytajg[.]onion” .
  • The attackers leverage several Tor2Web proxy services to easily allow the access to the Tor C2.
  • The binary can work both as cryptor and decryptor.
  • The C2 dynamically generates a different Bitcoin address for each infection.

“LooCipher encrypts the victim’s files using AES-128 ECB, and adds the extension “.lcphr“.” states Eminsoft.

“No ransom note file is left, but the malware does leave a screen telling the victim to make a BitCoin payment and then use the same malware to decrypt their files once payment is complete.”

LooCipher decryptor Emsisoft

Emsisoft also published a Detailed usage guide for its decryptor.

A couple of weeks ago experts at Yoroi-Cybaze ZLab also released a free decryptor for Loocipher Ransomware

Enjoy it!

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – ransomware, malware)

[adrotate banner=”5″]

[adrotate banner=”13″]


