
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Lufthansa customers were targeted by a cyber attack

Unknown hackers have gained access to the user personal accounts of the website of Lufthansa airline (LH.com) and used frequent-flyer miles. Unknown hackers have breached the system of the German flag carrier Lufthansa, the news was reported first by the German magazine Der Spiegel. The attackers accessed individual passenger accounts on the company’s website LH.com as […]

Lufthansa customers were targeted by a cyber attack

Unknown hackers have gained access to the user personal accounts of the website of Lufthansa airline (LH.com) and used frequent-flyer miles.

Unknown hackers have breached the system of the German flag carrier Lufthansa, the news was reported first by the German magazine Der Spiegel.

The attackers accessed individual passenger accounts on the company’s website LH.com as confirmed by the company on Friday.

Lufthansa immediately started the operations to mitigate the risks of exposure in compliance to its incident response plan.

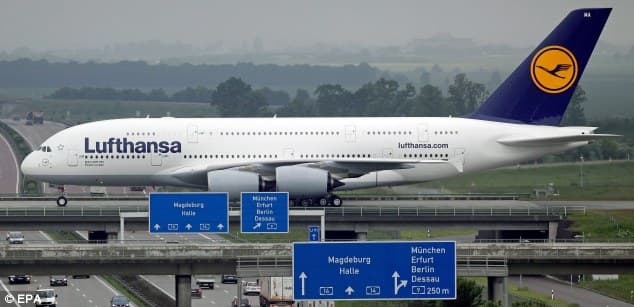
lufthansa hacked 2

Lufthansa has taken prompt countermeasures, but it “had not been able to prevent illicit access to some customer files,” according to company’s representatives that confirmed that hackers may have accessed hundred customers, but highlighted that no data was exfiltrated from Lufthansa’s systems.

“We had to lock several hundred customer pages,” a Lufthansa spokesman told DPA news agency. “We believe to have the problem generally under control,” he said.

The attackers run a massive brute-force attack against the system of the company, rumors confirm the involvement of a botnet that was used by hackers to target Lufthansa.

“This has been achieved through the use of so-called botnets: There was a large number of username and password combinations automatically tried until a Login succeeded.” reports the Der Spiegel magazine.

Once accessed the company’s database, the attackers used frequent-flyer miles to obtain vouchers and redeem rewards, they focused their activity on vouchers that don’t need to be delivered by mail.

In one case, the hackers have ordered watches and a tablet for a value of 2700 Euro, the destination address used by the attackers was London, meanwhile the billing address was in Berlin.

Lufthansa confirmed that a “small, single-digit number” of Lufthansa’s top client accounts was the victims of the attack. These clients are called by the company “HON Circle” members, which are customers who have flown at least 600,000 HON miles in two years exclusively in the Business and First Class.

Of course, the company restored the account miles following the cyber attack.

Stay tuned ….

Pierluigi Paganini

(Security Affairs –  Lufthansa , hackers)


