
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Windows App runs on Mac to download MacOS malware

Experts at Trend Micro have detected a new strain of MacOS malware that hides inside a Windows executable to avoid detection. Security experts at Trend Micro have spotted a new strain of MacOS malware disguises itself as a Windows executable file to evade detection. The malware is carried via .EXE file that will not execute […]

MacOS malware

Experts at Trend Micro have detected a new strain of MacOS malware that hides inside a Windows executable to avoid detection.

Security experts at Trend Micro have spotted a new strain of MacOS malware disguises itself as a Windows executable file to evade detection. The malware is carried via .EXE file that will not execute on a Windows machine.

The experts discovered the malicious code inside the installer for a popular firewall and network monitor called Little Snitch, the .ZIP files were available for download from various torrent websites.

“By default, attempting to run an EXE file on a Mac or Linux OS will only show an error notification.” reads the analysis published by Trend Micro.

“However, we found EXE files in the wild delivering a malicious payload that overrides Mac’s built-in protection mechanisms such as Gatekeeper. This routine evades Gatekeeper because EXE is not checked by this software, bypassing the code signature check and verification since the technology only checks native Mac files.”

When the .ZIP file extracts a .DMG file including the installer for Little Snitch.

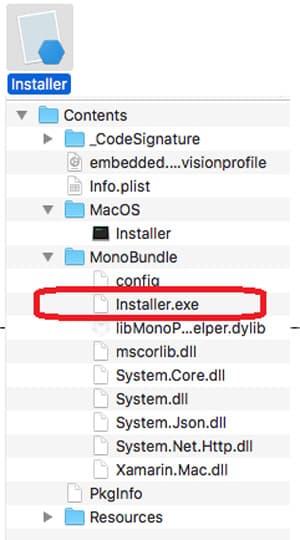
Experts noticed inside the installer the strange presence of a .EXE file bundled with the app that was responsive for the malicious payload.

“When the installer is executed, the main file also launched the executable as it is enabled by the mono framework included in the bundle. This framework allows the execution of Microsoft .NET applications across platforms such as OSX.” continues the report.

The malware initially collects the system information such as ModelName, ModelIdentifier, ProcessorSpeed, ProcessorDetails, NumberofProcessors and send data to the C&C.

Then the malware downloads potentially unwanted applications (PUAs) that include adware masqueraded as Adobe Flash and a potentially tainted copy of Little Snitch.

In this specific attack, malware authors used .EXE files that are not executed on MacOS and for this reason are ignore by anti-malware packages running on Apple systems.

Experts noticed that the execution of the .EXE file on a Windows system will return an error.

Most of the infections were observed in the United Kingdom, Australia, Armenia, Luxembourg, South Africa, and the United States.

Experts believe that the discovery made by the researchers is related to a study conducted by malware authors on new techniques to spread the malware.

“We suspect that this specific malware can be used as an evasion technique for other attack or infection attempts to bypass some built-in safeguards such as digital certification checks since it is an unsupported binary executable in Mac systems by design.” concludes the experts.

“We think that the cybercriminals are still studying the development and opportunities from this malware bundled in apps and available in torrent sites, and therefore we will continue investigating how cybercriminals can use this information and routine.”

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – MacOS malware, hacking)

[adrotate banner="5"]

[adrotate banner=”13″]


