
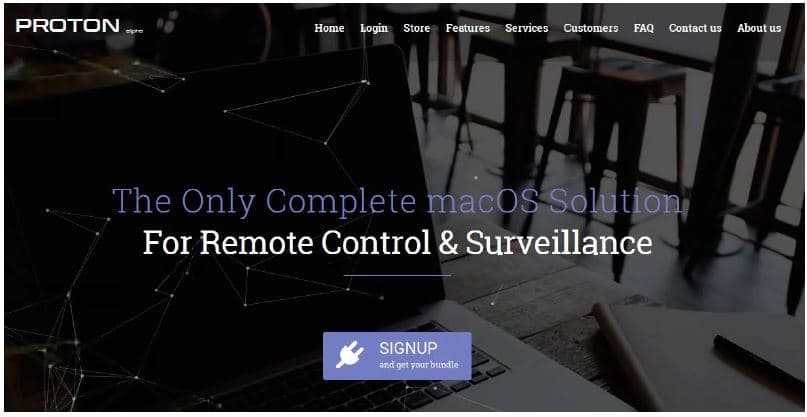
Experts from security firm Sixgill have discovered a new strain of the macOS Proton RAT that is offered for sale on Russian cybercrime underground.
The Dark Web is the right place where to find any kind of illegal products and services, malware such as banking trojan and spyware are very popular in cyber criminal underground.
Recently a new remote access tool (RAT) specifically designed to infect macOS systems is currently being advertised on Russian cybercrime underground. The researchers at security firm Sixgill discovered the advertising on crime forums and on a custom website, this threat is also described in videos published on YouTube.
The Proton homepage went down just after the experts at Sixgill published the report.
“Sixgill researchers have encountered a post in one of the leading, closed Russian cybercrime message boards. The author of the thread announced a RAT dubbed Proton, intended for installation exclusively on MAC OS devices. The author offered this product in one of the leading underground cybercrime markets.” reads a report published by Sixgill.
The Proton RAT first appeared in the threat landscape last year, the variant recently advertised on hacking forums includes many features such as the ability to execute console commands, access the user’s webcam, log keystrokes, capture screenshots and open SSH/VNC remote connections. The malicious code is also able to inject malicious code in the user’s browser to display popups asking victims information such as credit card numbers, login credentials, and others.
“The malware includes root-access privileges and features allowing an attacker to obtain full control of the victim’s computer. Its capabilities include: running real-time console commands and file-manager, keylogging, SSH/VNC connectivity, screenshots, webcam operation and the ability to present a custom native window requesting information such as a credit-card, driver’s license and more. The malware also boasts the capability of iCloud access, even when two-factor authentication is enabled.” continues the report.
According to the author, macOS Proton RAT is written in native Objective-C and it is fully undetected by any existing MAC OS antivirus solution.
Below the list of features described in the ad:

The Proton RAT has root access and is able to elude standard macOS security features, it is also able to bypass two-factor authentication on iCloud accounts.
Researchers speculate macOS Proton RAT leverages a zero-day vulnerability in macOS, but most interesting characteristic of the threat is that the malicious code is signed with genuine Apple code-signing certificates. It is likely the author has managed to falsify registration to Apple Developer ID Program or has stolend the credentials to an apple developer.
“The real threat behind the software is this: The malware is shipped with genuine Apple code-signing signatures. This means the author of Proton RAT somehow got through the rigorous filtration process Apple places on MAC OS developers of third-party software, and obtained genuine certifications for his program. Sixgill evaluates that the malware developer has managed to falsify registration to the Apple Developer ID Program or used stolen developer credentials for the purpose.” reads the report.
The price for the macOS Proton RAT ranged from $1,200 to $830,000 for the entire project (an absurd price). Below the version advertised on the Proton websites:
Standard Edition
I) License to control only ONE remote machine 1) 1 BTC — unsigned 2) 2 BTC — signed
II) License to control 20 remote machines 1) 10 BTC — unsigned 2) 11 BTC — signed
III) License to control infinite remote machines 1) 66 BTC — unsigned 2) 76 BTC — signed
Extended edition
I) License to control infinite remote machines 1) 166 BTC — unsigned 2) 200 BTC — signed
II) License to control infinite remote machines on your own server 1) 366 BTC — without source code 2) 666 BTC — with full source code
Researchers noticed that the authors of the malware try to disguise their spyware as legitimate surveillance software.
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(Security Affairs – macOS Proton RAT, malware)
[adrotate banner=”9″]
[adrotate banner=”13″]


