
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Magecart attacks are still around but are more difficult to detect

Researchers from Malwarebytes warns that the Magecart skimming campaign is active, but the attacks are more covert. Magecart threat actors have switched most of their operations server-side to avoid detection of security firms. However, Malwarebytes researchers warn that the Client-side Magecart attacks are still targeting organizations, but are more covert. The researchers recently uncovered two […]

magecart

Researchers from Malwarebytes warns that the Magecart skimming campaign is active, but the attacks are more covert.

Magecart threat actors have switched most of their operations server-side to avoid detection of security firms. However, Malwarebytes researchers warn that the Client-side Magecart attacks are still targeting organizations, but are more covert.

The researchers recently uncovered two domains, “scanalytic[.]org” and “js.staticounter[.]net,” belonging to the Magecart infrastructure on the same ASN (AS29182) that was used by the cybercriminals.

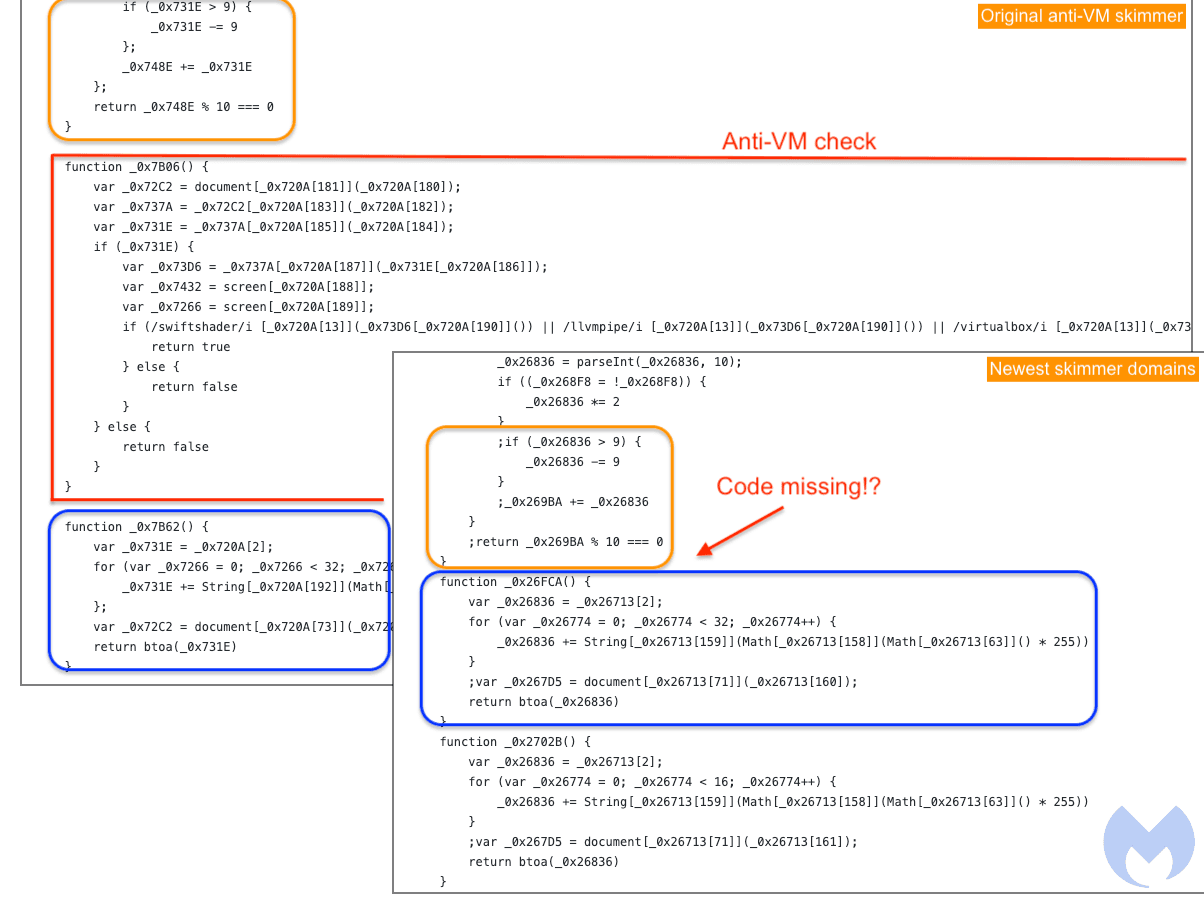
Malwarebytes linked the 2 domains with a previous campaign from November 2021 which was characterized by the first use of a software skimmer designed to check the execution within a virtual machine.

The experts also noticed that the threat actors have now removed the VM detection code, perhaps because it caused more issues than benefits.

magecart

The discovery of additional domains linked to the same infrastructure suggests the campaign dates back to at least May 2020.

Malwarebytes researchers observed the use of 3 different themes by the threat actor to hide their skimmer, named after JavaScript libraries:

The researchers explained that they have generally seen less skimming attacks during the past several months, perhaps because they were more focused on the Magento CMS.

“In addition, we (as several other companies) can only observe client-side attacks and as such we are oblivious to what happens server-side. Only a handful of researchers who do website cleanups have the visibility into PHP-based skimmers.” concludes the analysis. “While stealing credit cards is still a good business, there are other types of data considerably more worth it. Crypto wallets and similar digital assets are extremely valuable and there is no doubt that clever schemes to rob those are in place beyond phishing for them. For an example of a client-side attack via JavaScript draining crypto assets, check out this blog from Eliya Stein over at Confiant.”

Follow me on Twitter: @securityaffairs and Facebook

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, Magecart)

[adrotate banner=”5″]

[adrotate banner=”13″]


