
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Experts believe the Magecart Group 5 could be linked to the Carbanak APT

Security experts linked the Magecart group 5 to the infamous Dridex banking Trojan and the Carbanak cybercrime group. Researchers at Malwarebytes found a link between a scheme associated with the Magecart group and Dridex phishing campaigns and the activities of the Carbanak group.  The Magecart group tracked as Magecart Group 5, one of the most […]

Magecart Group 5

Security experts linked the Magecart group 5 to the infamous Dridex banking Trojan and the Carbanak cybercrime group.

Researchers at Malwarebytes found a link between a scheme associated with the Magecart group and Dridex phishing campaigns and the activities of the Carbanak group. 

The Magecart group tracked as Magecart Group 5, one of the most active crime gangs under the Magecart umbrella, appears to be connected to the Carbanak crime gang. 

Hacker groups under the Magecart umbrella continue to target to steal payment card data with so-called software skimmers. Security firms have monitored the activities of a dozen groups at least since 2010. 

According to a joint report published by RiskIQ and FlashPoint, some groups are more advanced than others, in particular, the gang tracked as Group 4 appears to be very sophisticated.

The list of victims of the groups is long and includes several major platforms such as British Airways, Newegg, Ticketmaster, MyPillow and Amerisleep, and Feedify. 

Millions of Magecart instances were detected over time, security experts discovered tens of software skimming scripts.

In a report recently published by RiskIQ, experts estimate that the group has impacted millions of users. RiskIQ reports a total of 2,086,529 instances of Magecart detections, most of them are supply-chain attacks.

Differently from other Magecart groups, the MG5 specializes in supply chain attacks.

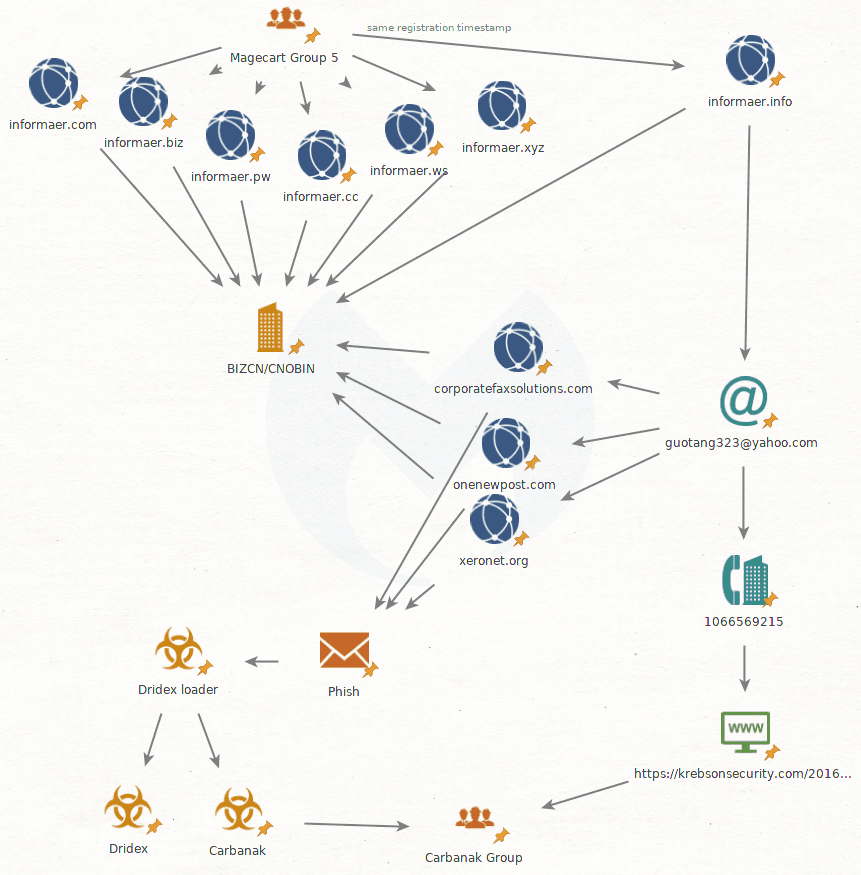
Malwarebytes researchers analyzed a number of domains involved in campaigns associated with the Magecart Group 5 and for those ones registered before the GDPR took effect they discovered that the registrant is connected to Dridex phishing campaigns and the Carbanak group.

The domains analyzed by the experts were registered via the well-known Chinese bulletproof registrar BIZCN/CNOBIN. Experts noticed that the attackers registered the domain informaer under eight different top-level domains using privacy protection services, but they have forgotten to use the same to informaer.info. The analysis of the informaer.info revealed the email address and the phone address used by the registrant, respectively +86.1066569215 and guotang323@yahoo[.]com.

These data were associated with other domains, many of which connected to Dridex phishing campaigns.

Magecart Group 5

Experts also highlighted that the registrants’ phone address for the informaer.info domain (+86.1066569215) is mentioned by Brian Krebs in a blog post exploring connections between tje Russian security firm Infocube and the Carbanak group.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – Magecart Group 5, cybercrime)

[adrotate banner=”5″]

[adrotate banner=”13″]


