
Magecart hackers continuously improve their exfiltration techniques to evade detection, they are hiding stolen credit card data into images.
Magecart hackers have devised a new technique to obfuscating the malware within comment blocks and hide stolen credit card data into images evading detection.
Hacker groups under the Magecart umbrella continue to target e-stores to steal payment card data with software skimmers. Security firms have monitored the activities of a dozen groups at least since 2010.
According to a previous report published by RiskIQ and FlashPoint, some groups are more advanced than others, in particular, the gang tracked as Group 4 appears to be very sophisticated.
The list of victims of the groups is long and includes several major platforms such as British Airways, Newegg, Ticketmaster, MyPillow and Amerisleep, and Feedify.
Millions of Magecart instances were detected over time, security experts discovered tens of software skimming scripts.
Researchers from security firm Sucuri reported that one tactic that some Magecart groups used in their attacks is the dumping of stolen credit card details into image files on the server.
This trick avoids raising suspicion, in the attacks monitored by the experts the attackers later download the data using simple GET requests.
In an incident investigated by Sucuri, the experts noticed a couple of image files on the server that continued to be populated with chunks of base64 encoded data. Once decoded the data to plain text, experts discovered they were credit card and CVV numbers, billing addresses, expiration dates and more.
Although the attribution of the attack to a specific threat actor is difficult, experts speculate the involvement of Magecart Group number 7 due to overlaps in the TTPs associated with this group.
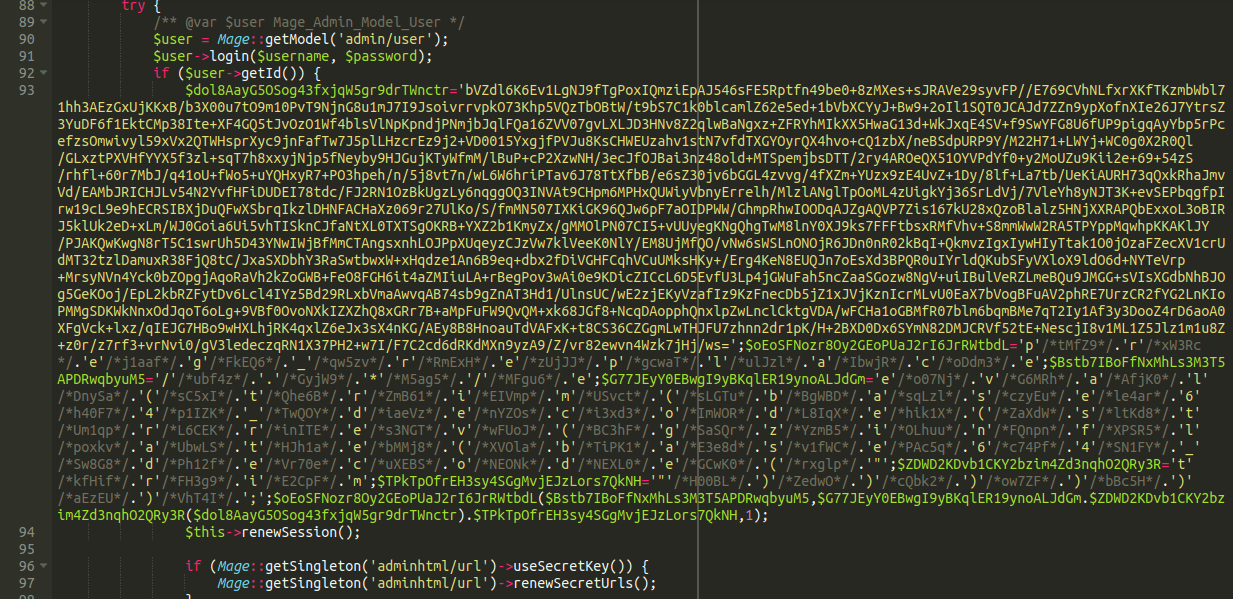
The attackers also used a “concatenation” technique to obfuscate data, below the example provided by the researchers:
<?php echo ""."h"."e"."".""."llo"."w"."o"."".""."r"."l"."d"."";
that is interpreted by the server as simply “helloworld”.
The attackers also used to hide malware with comment chunks that do not functionally do anything but add a layer of obfuscation making the detection harder.
Magecart hackers were also spotted capturing payment card details in real-time on the compromised website, then the data were saved to a fake style sheet file (.CSS) on the server and subsequently downloaded using a GET request.
“MageCart is an ever growing threat to e-commerce websites,” concludes the report. “From the perspective of the attackers: the rewards are too large and consequences non-existent, why wouldn’t they? Literal fortunes are made stealing and selling stolen credit cards on the black market.”
Follow me on Twitter: @securityaffairs and Facebook
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – hacking, credit card data)
[adrotate banner=”5″]
[adrotate banner=”13″]


