
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Magecart group infected over 17,000 domains via unprotected AWS S3 Buckets

The Magecart continues to target websites worldwide, it infected over 17,000 domains by targeting improperly secured Amazon S3 buckets.  The Magecart gang made the headlines again, according to a new report published by RiskIQ, it has infected over 17,000 domains by targeting improperly secured Amazon S3 buckets.  A few days ago, security experts at Sanguine Security have […]

MAgecart attack

The Magecart continues to target websites worldwide, it infected over 17,000 domains by targeting improperly secured Amazon S3 buckets. 

The Magecart gang made the headlines again, according to a new report published by RiskIQ, it has infected over 17,000 domains by targeting improperly secured Amazon S3 buckets. 

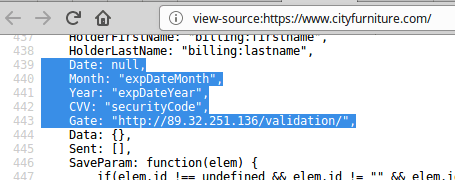
A few days ago, security experts at Sanguine Security have uncovered a new large-scale payment card skimming campaign that already hacked 962 online stores running on the Magento CMS. Security expert Micham spotted another attack attributed to the Magecart gang, hackers injected a skimmer script in the The Guardian via old AWS S3 bucket and exploiting wix-cloud[.]com as a skimmer gate.

According to RiskIQ, since April 2018, Magecart hackers adopted a new tactic that relies on misconfigured Amazon S3 buckets. These buckets allow anyone with an active Amazon Web Services account to read or write them.

“However, the actual scale of this campaign and the number of sites affected is much larger than previously reported. The actors behind these compromises have automated the process of compromising websites with skimmers by actively scanning for misconfigured Amazon S3 buckets.” reads the analysis published by RiskIQ. “These buckets are un-secure because they are misconfigured, which allows anyone with an Amazon Web Services account to read or write content to them.”

The attackers scan the web for misconfigured buckets containing any JavaScript files, then download the files, modify them by appending the skimming code to the bottom, and overwrite the script on the bucket.

RiskIQ experts believe threat actors have already compromised a large number of S3 buckets affecting over 17,000 domains, including websites in the top 2,000 of Alexa rankings.

“However, the ease of compromise that comes from finding public S3 buckets means that even if only a fraction of their skimmer injections returns payment data, it will be worth it; they will have a substantial return on investment.” concludes RiskIQ.

“Perhaps most importantly, the widespread nature of this attack illustrates just how easy it is to compromise a vast quantity of websites at once with scripts stored in misconfigured S3 buckets.”

Security firms have monitored the activities of a dozen Magecart groups at least since 2015. The gangs use to implant skimming script into compromised online stores in order to steal payment card data on, but they are quite different from each other. 

According to a joint report published by RiskIQ and FlashPoint, some groups are more advanced than others, in particular, the gang tracked as Group 4 appears to be very sophisticated.

The list of victims of Magecart groups is long and includes several major platforms such as British Airways, Newegg, Ticketmaster, MyPillow and Amerisleep, and Feedify. ​​

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – Magecart, hacking)

[adrotate banner=”5″]

[adrotate banner=”13″]


