
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Adobe revealed that the Magento Marketplace was hacked

Adobe discloses security breach impacting Magento Marketplace users Adobe discloses a security breach that affected the users of the Magento marketplace website, the incident was discovered last week. Adobe disclosed a security breach that affected the users of the Magento Marketplace portal, the security team discovered the incident on November 21. The Magento Marketplace is […]

magento data-breach-notofications-email

Source ZDnet

Adobe discloses security breach impacting Magento Marketplace users

Adobe discloses a security breach that affected the users of the Magento marketplace website, the incident was discovered last week.

Adobe disclosed a security breach that affected the users of the Magento Marketplace portal, the security team discovered the incident on November 21. The Magento Marketplace is a website for buying and downloading themes and plugins for e-stores running the Magento CMS.

Magento is the most popular content management solution (CMS) for building e-commerce website, Adobe acquired the company for $1.68 billion in 2018.

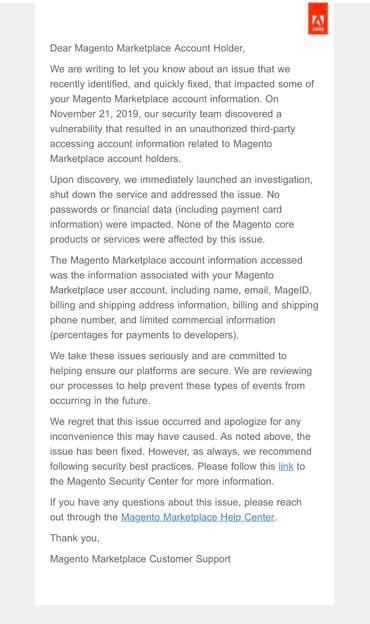
According to the data breach notification sent via email by Adobe to its customers, the hackers exploited a vulnerability in the Marketplace website to access account information for registered users. The company did not disclose the number of impacted accounts.

magento data-breach-notofications-email
Source ZDnet

Hackers accessed data of registered users and developers that registered on the portal to sell their plugins and themes.

Exposed data include name, email, store username (MageID), billing and shopping addresses, phone number, and some commercial information, while financial data and passwords were not compromised. In response to the incident, the company temporarily took down the Marketplace in order to fix the vulnerability exploited by hackers.

“On November 21, we became aware of a vulnerability related to Magento Marketplace. We temporarily took down the Marketplace in order to address the issue. The Marketplace is back online. This issue did not affect the operation of any Magento core products or services.” reads the security update published by Magento.

“We have notified impacted account holders directly. “

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – Adobe, Magento)

[adrotate banner=”5″]

[adrotate banner=”13″]


