
Researchers spotted 5 malicious Google Chrome extensions used to track users’ browsing activity and profit of retail affiliate programs.
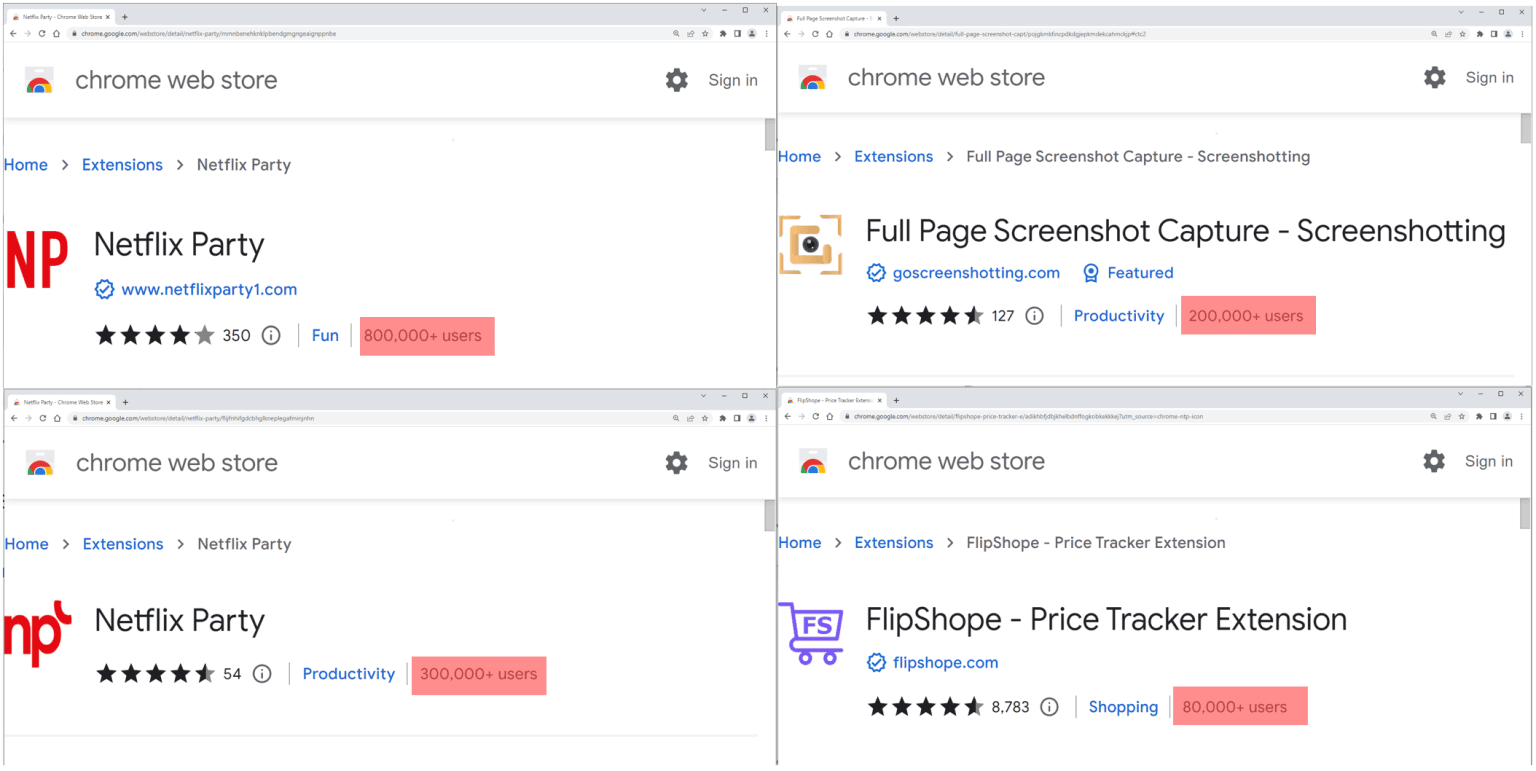
McAfee researchers discovered five malicious Google Chrome extensions with a total install base of over 1,400,000. The malicious Google Chrome extensions were masquerading as Netflix viewers, website coupons, and apps for taking screenshots of a website.
| Name | Extension ID | Users |
| Netflix Party | mmnbenehknklpbendgmgngeaignppnbe | 800,000 |
| Netflix Party 2 | flijfnhifgdcbhglkneplegafminjnhn | 300,000 |
| FlipShope – Price Tracker Extension | adikhbfjdbjkhelbdnffogkobkekkkej | 80,000 |
| Full Page Screenshot Capture – Screenshotting | pojgkmkfincpdkdgjepkmdekcahmckjp | 200,000 |
| AutoBuy Flash Sales | gbnahglfafmhaehbdmjedfhdmimjcbed | 20,000 |
The extensions a designed to track the user’s browsing activity, they are also able can insert code into eCommerce websites being visited. Basically, the extension modifies the cookies on the site so that the extension authors receive affiliate payment for any items purchased.
“Every website visited is sent to servers owned by the extension creator. They do this so that they can insert code into eCommerce websites being visited. This action modifies the cookies on the site so that the extension authors receive affiliate payment for any items purchased.” reads the analysis published by the experts. “The users of the extensions are unaware of this functionality and the privacy risk of every site being visited being sent to the servers of the extension authors.”

The manifest.json sets an HTML background page, which loads the javascript b0.js that sends every URL visited by the victims to the C2 and injects code into the eCommerce sites.
Below is a step-by-step flow of events while the users navigate to the BestBuy website.
- The user navigates to bestbuy.com and the extension posts this URL in a Base64 format to d.langhort.com/chrome/TrackData/
- Langhort.com responds with “c” and the URL. The “c” means the extension will invoke the function passf_url()
- passf_url() will perform a request against the URL
- the URL queried in step 3 is redirected using a 301 response to bestbuy.com with an affiliate ID associated with the Extension owners
- The extension will insert the URL as an Iframe in the bestbuy.com site being visited by the user
- Shows the Cookie being set for the Affiliate ID associated with the Extension owners. They will now receive a commission for any purchases made on bestbuy.com
Some of the extensions implement a time check before they would perform any malicious activity to avoid detection. The researchers noticed that the malicious extensions start operating after 15 days from their installation.
“McAfee advises its customers to be cautious when installing Chrome extensions and pay attention to the permissions that they are requesting. ” concludes the report. “The permissions will be shown by Chrome before the installation of the extension. Customers should take extra steps to verify the authenticity if the extension is requesting permissions that enable it to run on every website you visit such as the one detailed in this blog .”
Follow me on Twitter: @securityaffairs and Facebook
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – hacking, Google Chrome extensions)
[adrotate banner=”5″]
[adrotate banner=”13″]


