
Security Affairs
CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|FBI Blames North Korea for $6 Billion Binance Crypto Theft|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|FBI Blames North Korea for $6 Billion Binance Crypto Theft|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

How to use a malicious JPEG to hack corporate networks

Security researcher Marcus Murray discovered a method to exploit a malicious JPEG to compromise modern Windows servers inside corporate networks. Security expert and penetration tester Marcus Murray discovered a way to use a malicious JPEG to compromise modern Windows servers and elevate privileges over targeted networks. The researcher has demonstrated the attack a few days […]

How to use a malicious JPEG to hack corporate networks

Security researcher Marcus Murray discovered a method to exploit a malicious JPEG to compromise modern Windows servers inside corporate networks.

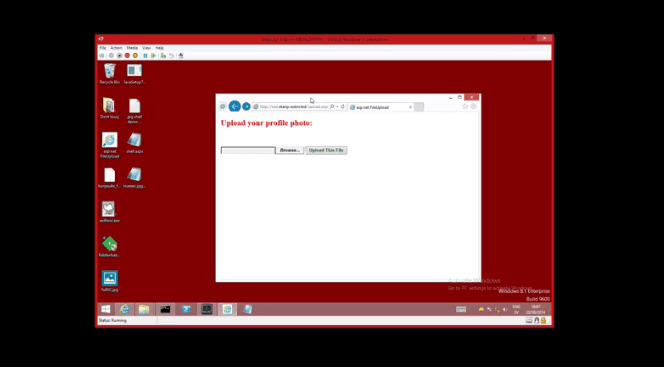
Security expert and penetration tester Marcus Murray discovered a way to use a malicious JPEG to compromise modern Windows servers and elevate privileges over targeted networks. The researcher has demonstrated the attack a few days ago in a live hack for the RSA conference in San Francisco, the hacker used a malicious JPEG to violate the system at an unnamed US Government agency that ran a flawed website that allows photo upload.

malicious JPEG

Murray injected active content into the attributes of a JPEG picture, once compromised the target he elevated its privileges and compromise the domain controller into the network. If an attacker successfully hacks the domain controller he will gain complete control over the network, for example he can install any kind of malware for spying on machines or for example he can install any kind of malware for spying on machines or exfiltrate sensitive data.

“I’m going to try to compromise the web server, then go for back end resources, and ultimately compromise a domain controller,” explained Murray, adding that the attacks is quite simple to run.

Murray exploited the technique to upload a remote access trojan (RAT) created using the popular Metasploit Penetration Testing Software. The experts also used other tools and compilers running on Windows servers to complete the attack.

“Even in mixed environments, when you own the domain controller you usually own the entire infrastructure of that company and that is true because they have Linux server you usually use Windows clients for connect to them.” “From this point [after obtaining the control of the domain controller] we can do anything; we can upload domain admin tools, and manage it like it was our own.”

The attack technique relies on the lack of input validation on the client side, vulnerable uploading portals allow the upload of malicious dynamic content merely because it carries a .jpg extension. Other flawed servers, including the one hacked by Murray, validated the images submitted by the users, but not the file extension types, this means that once uploaded and pre-viewed, the files display as the text that has been inserted into active content fields rather than the expected image.

Below the video PoC for the attack.

Pierluigi Paganini

(Security Affairs –  malicious JPEG, Hacking)


