
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Malicious NPM packages target PayPal users

Threat actors deploy malicious NPM packages to steal PayPal credentials and hijack cryptocurrency transfers. Fortinet researchers discovered multiple malicious NPM packages that are used to target PayPal users. The packages were uploaded to the repository in early March by a threat actor known as tommyboy_h1 and tommyboy_h2, and were used to steal PayPal credentials and hijack cryptocurrency transfers. “Using PayPal-related […]

malicious NPM packages targets PayPal

Threat actors deploy malicious NPM packages to steal PayPal credentials and hijack cryptocurrency transfers.

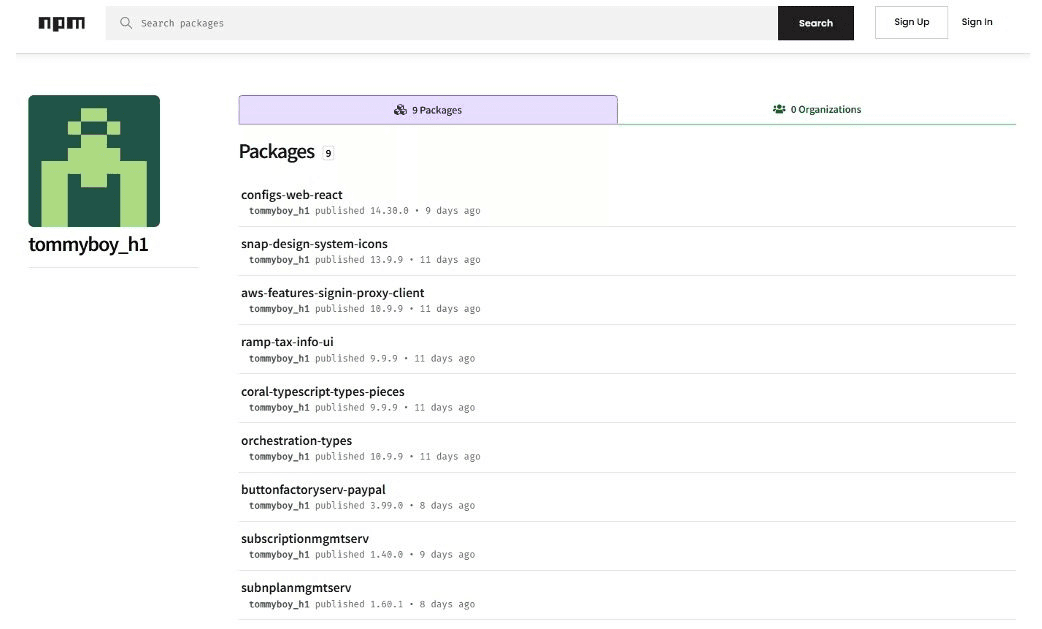
Fortinet researchers discovered multiple malicious NPM packages that are used to target PayPal users. The packages were uploaded to the repository in early March by a threat actor known as tommyboy_h1 and tommyboy_h2, and were used to steal PayPal credentials and hijack cryptocurrency transfers.

“Using PayPal-related names helps these malicious packages avoid detection, making it easier for attackers to steal sensitive information. By including “PayPal” in the name of the malicious packages, such as oauth2-paypal and buttonfactoryserv-paypal, the attackers also create a false sense of legitimacy, tricking developers into installing them.” reads the analysis published by Fortinet. “The code collects and exfiltrates system data, such as usernames and directory paths, which can then be used to target PayPal accounts or be sold for fraudulent purposes.”

Malicious NPM packages use a preinstall hook to run hidden scripts, steal system info, obfuscate data, and exfiltrate it to attacker-controlled servers for future attacks.

Fortinet researchers recommend watching for fake PayPal-related packages, checking network logs for odd connections, removing threats, updating credentials, and staying cautious when installing packages.

The same attacker likely created the tommyboy_h1 and tommyboy_h2 malicious packages to target PayPal users.

“The authors of tommyboy_h1 and tommyboy_h2 are likely the same person, publishing multiple malicious packages in a short time. We suspect that the same author created these packages to target PayPal users.” concludes the report. “We urge the public to be cautious when downloading packages and to ensure they are from trusted sources to avoid falling victim to such attacks.”

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, malicious NPM packages)


