
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Microsoft spotted multiple malspam campaigns using malware-laced ISO and IMG files

Microsoft warns of threat actors targeting organizations with malware-laced ISO and IMG files aimed at delivering a remote access trojan. Microsoft advanced machine learning threat detection models detected multiple malspam campaigns distributing malware-laced ISO. Last week experts from Microsoft detected a COVID-19-themed spam campaign, the messages are crafted to trick users into downloading and mounting […]

COVID malspam

Microsoft warns of threat actors targeting organizations with malware-laced ISO and IMG files aimed at delivering a remote access trojan.

Microsoft advanced machine learning threat detection models detected multiple malspam campaigns distributing malware-laced ISO.

Last week experts from Microsoft detected a COVID-19-themed spam campaign, the messages are crafted to trick users into downloading and mounting ISO or IMG file attachments. The bait ISO or IMG files were infected with a strain of the Remcos remote access trojan (RAT).

The campaign was targeting specific sectors using COVID-19 themed lures, the Remcos campaigns appear to be limited and short-lived to avoid the detection.

“We also saw a campaign targeting manufacturing companies in South Korea. Attackers sent target organizations an email that impersonates CDC’s Health Alert Network (HAN) and carrying malicious ISO file attachments. The ISO file contains a malicious SCR file, which is Remcos.” states Microsoft in a tweet.

Major malspam campaigns monitored by Microsoft include attacks at US small businesses, manufacturing companies in South Korea, and accountants in the US.

In the campaign against US small businesses, the messages pretended to be from the US Small Business Administration (SBA), carrying a malicious IMG (disk image) attachment. The IMG file contained an executable file that uses a misleading PDF icon, which once executes start the Remcos RAT infection.

In the campaign that targeted manufacturing companies in South Korea, threat actors impersonate CDC’s Health Alert Network (HAN). The attacks employed ISO file attachments containing a malicious SCR file used to install the Remcos RAT.

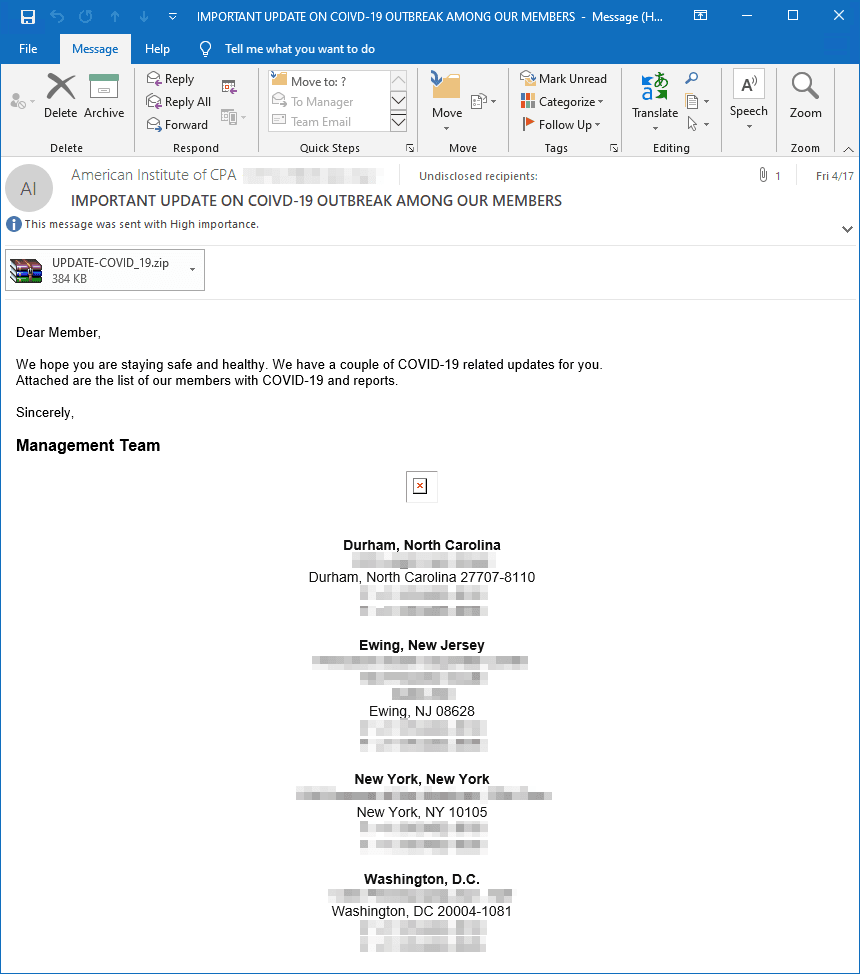
The third campaign observed by Microsoft targeted accountants in the US, in this case with COVID as lures. The messages pretend to provide “COVID-19 related updates” for members of the American Institute of CPAs. In this case, attackers used a ZIP archive containing a ISO file carrying a malicious SCR file with a misleading icon.

COVID malspam

At the time it is still unclear the end goal of the malspam campaigns, the combination of a specific type of attachment and the exploitation of COVID-19 as a lure characterized this malspam.

Please vote Security Affairs for European Cybersecurity Blogger Awards – VOTE FOR YOUR WINNERS
https://docs.google.com/forms/d/e/1FAIpQLSe8AkYMfAAwJ4JZzYRm8GfsJCDON8q83C9_wu5u10sNAt_CcA/viewform

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – COVID-19, malspam)

[adrotate banner=”5″]

[adrotate banner=”13″]


