
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Cyber Crime

Bad actors are using Gmail Drafts to control their bots

Security company Shape Security discovered a new strain of malware which is exploiting Gmail service as a communication channel with control server. Security experts at Shape Security announced to have found a new strain of malware that implements a smart technique to communicate with command and control servers, the commands are hidden in unassuming Gmail drafts that are never even […]

Bad actors are using Gmail Drafts to control their bots

Security company Shape Security discovered a new strain of malware which is exploiting Gmail service as a communication channel with control server.

Security experts at Shape Security announced to have found a new strain of malware that implements a smart technique to communicate with command and control servers, the commands are hidden in unassuming Gmail drafts that are never even sent.

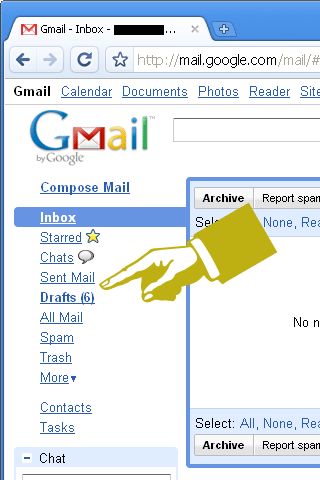
Gmail Drafts 2

The technique is very hard to detect as explained by the researchers at Shape Security:

“What we’re seeing here is command and control that’s using a fully allowed service, and that makes it superstealthy and very hard to identify,” says Wade Williamson, stated one of the experts “It’s stealthily passing messages back and forth without even having to press send. You never see the bullet fired.”

The attack chain is composed of the following phases:

  • The bad actors first set up a Gmail account.
  • The targeted machine is infected by the malicious agent.
  • The bad actors open the Gmail account on the victim’s computer in an invisible instance of Internet Explorer. IE could be run by Windows programs appearing to the victim as a harmless query web page for information.
  • The bad actors set the Gmail account to the drafts folder open and hidden. The malicious code is designed to retrieve commands the attackers enter into that draft field. The malware uses a python script to fetch the instruction and respond with its own acknowledgments in the same Gmail draft form, along with the exfiltrate information.

Once again the attackers exploited a reputable web service to hide the communication between the malware and C&C server as explained in the blog post published by Wired.

“The communication is encoded to to prevent it being spotted by intrusion detection or data-leak prevention. The use of a reputable web service instead of the usual IRC or HTTP protocols that hackers typically use to command their malware also helps keep the hack hidden.”

The malware is a variant of the remote access trojan (RAT) called Icoscript detected for the first time in august by experts at G-Data security firm. The first version of IcoScript spotted by G-Data receives commands from C&C via email services including Yahoo and Gmail

The post confirmed that is hard to detect such kind of attacks, the unique alternative is represented by the blocking of the Gmail service.

Pierluigi Paganini

Security Affairs –  (Gmail, malware)


