
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

WannaCry hero Marcus Hutchins pleads not guilty

The 23-year-old expert Marcus Hutchins pleaded “not guilty” during a court hearing in Milwaukee, Wisconsin. His trial has been scheduled for October. Yesterday, Marcus Hutchins, the WannaCry hero, has pleaded not guilty to charges of creating and selling malware at a hearing in Milwaukee, Wisconsin. The court decided to relax the expert bail terms, allowing him to […]

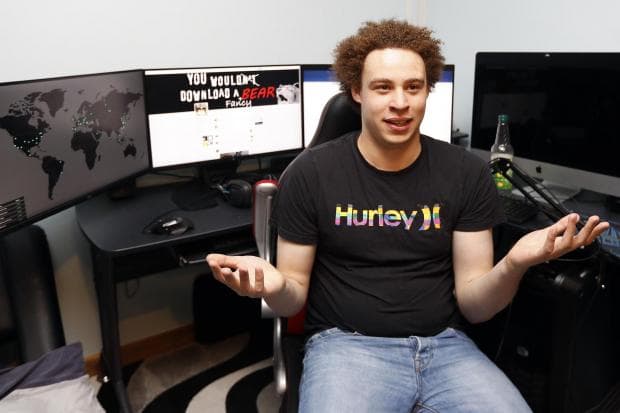
Marcus Hutchins

The 23-year-old expert Marcus Hutchins pleaded “not guilty” during a court hearing in Milwaukee, Wisconsin. His trial has been scheduled for October.

Yesterday, Marcus Hutchins, the WannaCry hero, has pleaded not guilty to charges of creating and selling malware at a hearing in Milwaukee, Wisconsin.

The court decided to relax the expert bail terms, allowing him to access the Internet and continues his ordinary working activities. The only restrictions on Hutchins is that the expert cannot visit the Wannacry server domain.

https://twitter.com/MalwareTechBlog/status/897185734100221952

The decision is unusual because computer crime suspects are not allowed to stay online.

The court allowed him to live in Los Angeles, where the company that hired him is located, but he is obliged to surrender his passport and he must wear a tracking device until his trial in October.

“Marcus Hutchins is a brilliant young man and a hero,” said Marcia Hofmann, founder of Zeigeist Law. “He is going to vigorously defend himself against these charges and when the evidence comes to light we are confident that he will be fully vindicated.”

Marcus Hutchins, also known as MalwareTech, is a 22-year-old security expert who made the headlines after discovering the “kill switch” that halted the outbreak of the WannaCry ransomware. Marcus Hutchins has been arrested in in Las Vegas after attending the Def Con hacking conference and was detained by the FBI in the state of Nevada.

The British security researcher was arrested on Thursday after being indicted on charges of creating the Kronos banking malware.

A second defendant whom identity was not revealed appears to be involved.

According to the investigators, Marcus Hutchins created the malware and shared it online, below the indictment issued by Eastern District of Wisconsin.

The prosecutors believe Hutchins created, shared, and masterminded the Kronos banking Trojan between July 2014 and July 2015.

“We are very pleased today that the court modified his terms to allow him to return to his important work,” said Hutchins lawyer Brian Klein, partner at Baker Marquart LLP.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(Security Affairs – Marcus Hutchins, cybercrime)

[adrotate banner=”5″]

[adrotate banner=”13″]


