
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Matrix Ransomware being distributed through malvertising

Security expert Jérôme Segura from Malwarebytes has spotted that Matrix Ransomware has risen again, it is now being distributed through malvertising. Malware researcher Jérôme Segura from Malwarebytes has discovered that Matrix Ransomware is now being distributed through malvertising campaign. https://twitter.com/EKFiddle/status/923660551095427072 The Matrix Ransomware was first spotted in 2016, in April 2017 the threat intelligence expert Brad Duncan uncovered the EITest campaign using […]

Matrix Ransomware

Security expert Jérôme Segura from Malwarebytes has spotted that Matrix Ransomware has risen again, it is now being distributed through malvertising.

Malware researcher Jérôme Segura from Malwarebytes has discovered that Matrix Ransomware is now being distributed through malvertising campaign.

https://twitter.com/EKFiddle/status/923660551095427072

The Matrix Ransomware was first spotted in 2016, in April 2017 the threat intelligence expert Brad Duncan uncovered the EITest campaign using the RIG exploit kit to distribute this malware.

Since then the Matrix ransomware slightly disappeared from the threat landscape, but now it seems to be back and it is being delivered through malvertising campaign that triggers an Internet Explorer flaw (CVE-2016-0189) and Flash one(CVE-2015-8651).

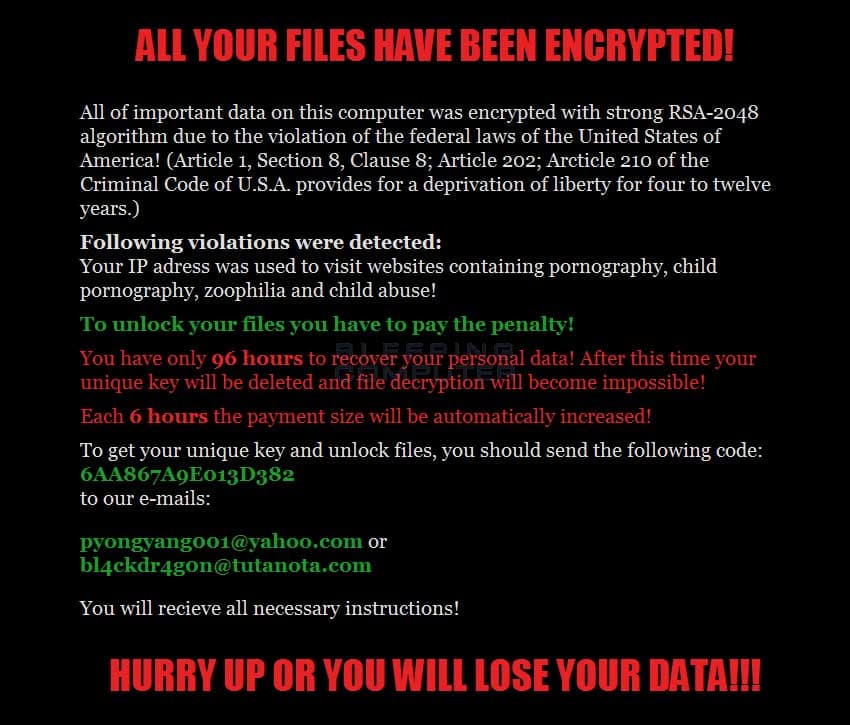
When a computer is infected with the latest variant of the Matrix Ransomware, the malicious code will encrypt the files on the victim’s machine, scramble their file names, and append the .pyongyan001@yahoo.com extension to the file scrambled name.

The ransomware also drops a ransom note (#_#WhatWrongWithMyFiles#_#.rtf) in every folder that contains files it encrypted, then it will display a ransom screen.

Matrix Ransomware

To protect your system, it is essential to install all available security updates for any software installed on the machine, run a security software, and always backup your data.
[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(Security Affairs – ransomware, malvertising)

[adrotate banner=”5″]

[adrotate banner=”13″]


