
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Actors behind Maze ransomware release files stolen from City of Pensacola

Maze ransomware operators have released 2GB of files that were allegedly stolen from the City of Pensacola during the recent attack. On December 7, 2019, the city of Pensacola has been hit by a ransomware attack, the city was forced to disconnect most of its systems following the attack that impacted emails, telephone lines, and […]

Maze ransomware

Maze ransomware operators have released 2GB of files that were allegedly stolen from the City of Pensacola during the recent attack.

On December 7, 2019, the city of Pensacola has been hit by a ransomware attack, the city was forced to disconnect most of its systems following the attack that impacted emails, telephone lines, and online payment services.

At the time experts speculated that the family of malware involved in the attack was the Maze ransomware.

Last week I reported shocking news, the victims of the Maze Ransomware are facing another risk, after having their data encrypted now crooks are threatening to publish their data online.

The Maze ransomware is known for implementing data harvesting capabilities, operators are now threatening to release the data for all those victims who refuse to pay the ransom.

The gang behind the Maze ransomware has set up a website where they have published the list names of eight companies that allegedly refused to pay the ransom.

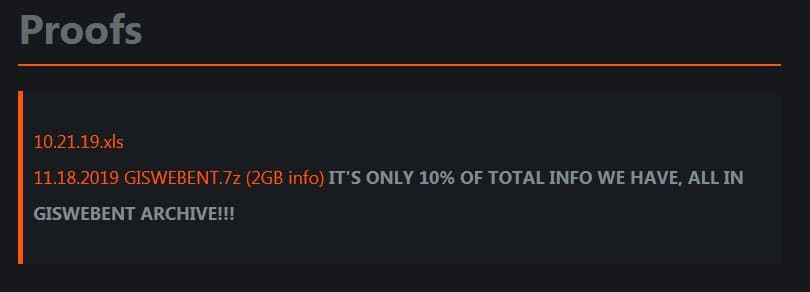
Now the Maze ransomware made the headlines again because its operators have released 2GB of files that were allegedly stolen from the City of Pensacola during the recent attack.

According to BleepingComputer that first confirmed the involvement of the Maze ransomware in the attack against the City of Pensacola, crooks demanded a $1 million ransom to decrypt the victim’s files.

Now the Maze operators released 2GB out of 32GB of files that they claim to have stolen during the attack on the city network.

The Maze gang told BleepingComputer that they released the stolen data as a proof of the hack and of their capabilities.

“This the fault of mass media who writes that we don’t exfiltrate data more than a few files. We did not want to make a pressure on city, we still dont make it right now. We’ve shown that our intentions are real.” the group told BleepingComputer.

Depending on the response of the City of Pensacola, the group could release other files in the next days.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – City of Pensacola, Maze)

[adrotate banner=”5″]

[adrotate banner=”13″]


