
The Maze ransomware operators now use a virtual machine to encrypt a computer, a tactic previously adopted by the Ragnar Locker malware.
The Maze ransomware operators have adopted a new tactic to evade detection, their malware now encrypts a computer from within a virtual machine. This technique was first adopted by Ragnar Locker gang in May, at the time the Ragnar Locker was deploying Windows XP virtual machines to encrypt victim’s files while bypassing security measures.
The malware leverages a VirtualBox feature that allows the host operating system to share folders and drives as a network share inside a virtual machine. The virtual machine mounts the shared path as a network drive from the \\VBOXSVR virtual computer to access their content.
The virtual machine then runs the ransomware in the virtual machine to encrypt the share’s files.
As the security software running on the victim’s host will not detect the ransomware executable or activity on the virtual machine, it will happily keep running without detecting that the victim’s files are now being encrypted.
Now Maze ransomware operators are using the same technique, according to researchers from Sophos that blocked some of their attacks.
“While conducting an investigation into an attack in July in which the attackers repeatedly attempted to infect computers with Maze ransomware, analysts with Sophos’ Managed Threat Response (MTR) discovered that the attackers had adopted a technique pioneered by the threat actors behind Ragnar Locker earlier this year, in which the ransomware payload was distributed inside of a virtual machine (VM).” reads the analysis published by Sophos.
In the two attempts blocked by the Sophos end-point, the Maze operators attempted to launch various ransomware executables using scheduled tasks named ‘Windows Update Security,’ or ‘Windows Update Security Patches,’ or ‘Google Chrome Security Update.’
In the third attack blocked by Sophos, Maze ransomware operators deployed an MSI file that installed the VirtualBox VM software on the server along with a customized Windows 7 virtual machine.
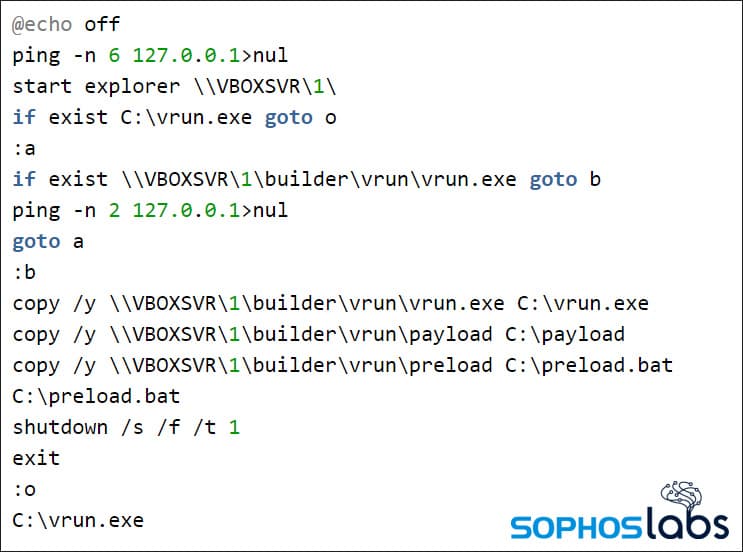
Upon executing the virtual machine, a batch file named startup_vrun.bat batch file would be executed that drops the Maze executables in the machine.
The startup_vrun.bat file is located at c:\users\Administrator\AppData\Roaming\Microsoft\Windows\Start Menu\Startup to achieve persistence.
“The root of that virtual disk contained three files associated with the Maze ransomware: preload.bat, vrun.exe, and a file just named payload (with no file extension), which is the actual Maze DLL payload.” continues the analysis.
“The script copies the same three files found on the root of the VM disk (the vrun.exe and payload DLL binaries, and the preload.bat batch script) to other disks, then issues a command to shut down the computer immediately. When someone powers the computer on again, the script executes vrun.exe.”

The machine is then shut down, after restarting it the vrun.exe will be launched to encrypt the host’s files.
Experts pointed out that the size of the disk used in this attack is greater than the one observed in the previous Ragnar Locker’s attacks.
The Ragnar Locker attack used a VM containing a Windows XP image that was only 404 MB in size. As Maze used Windows 7 image, the size of the file employed was of 2.6 GB.
“The Maze threat actors have proven to be adept at adopting the techniques demonstrated to be successful by other ransomware gangs, including the use of extortion as a means to extract payment from victims.” concludes the report. “As endpoint protection products improve their abilities to defend against ransomware, attackers are forced to expend greater effort to make an end-run around those protections.”
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – hacking, Maze ransomware)
[adrotate banner=”5″]
[adrotate banner=”13″]


