
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

BlackCat gang claims they stole data of 2.5 million patients of McLaren Health Care

The ALPHV/BlackCat ransomware gang added McLaren Health Care to the list of victims on its Tor leak site. McLaren Health Care is a not-for-profit healthcare system based in Michigan, United States. It is one of the largest integrated health systems in the state and serves a significant portion of the population through its network of […]

McLaren Health Care

The ALPHV/BlackCat ransomware gang added McLaren Health Care to the list of victims on its Tor leak site.

McLaren Health Care is a not-for-profit healthcare system based in Michigan, United States. It is one of the largest integrated health systems in the state and serves a significant portion of the population through its network of hospitals, clinics, and healthcare facilities.

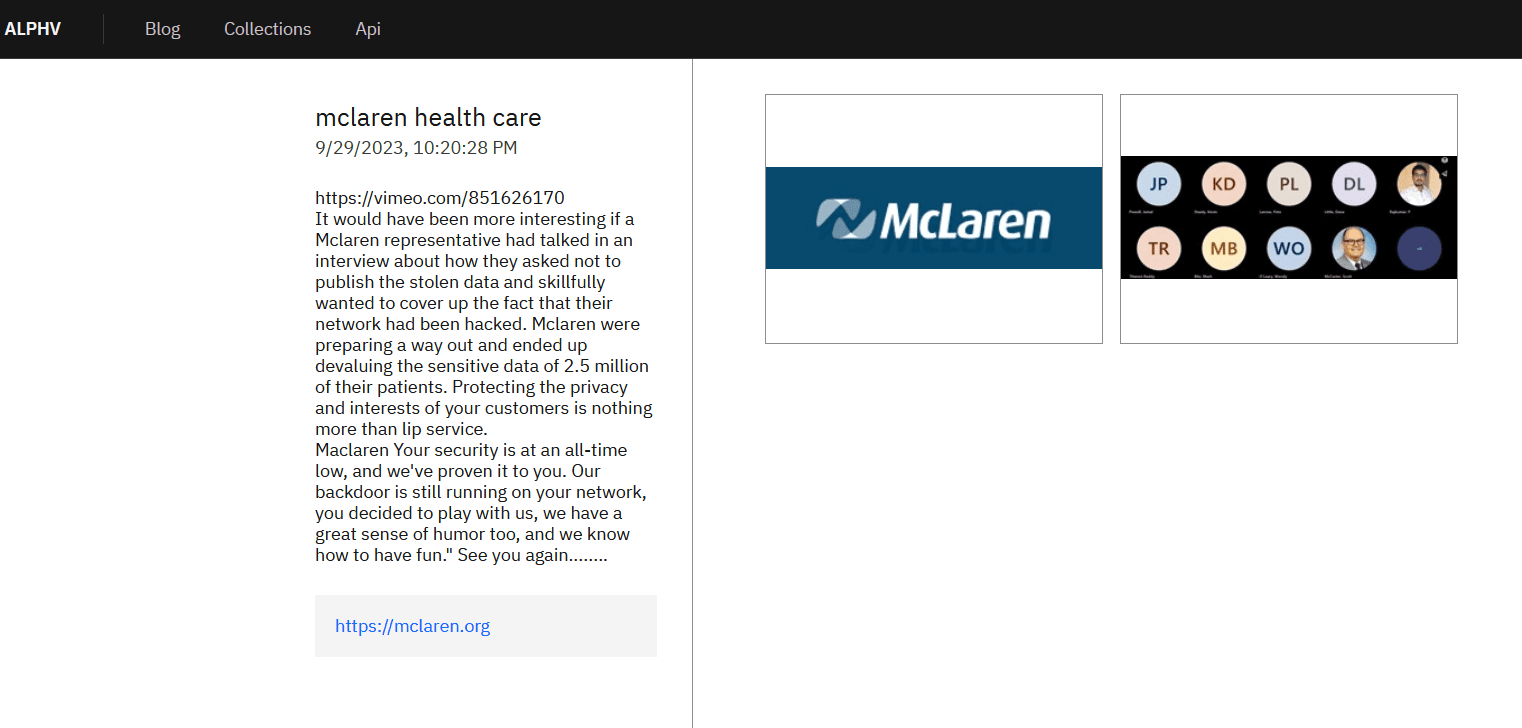
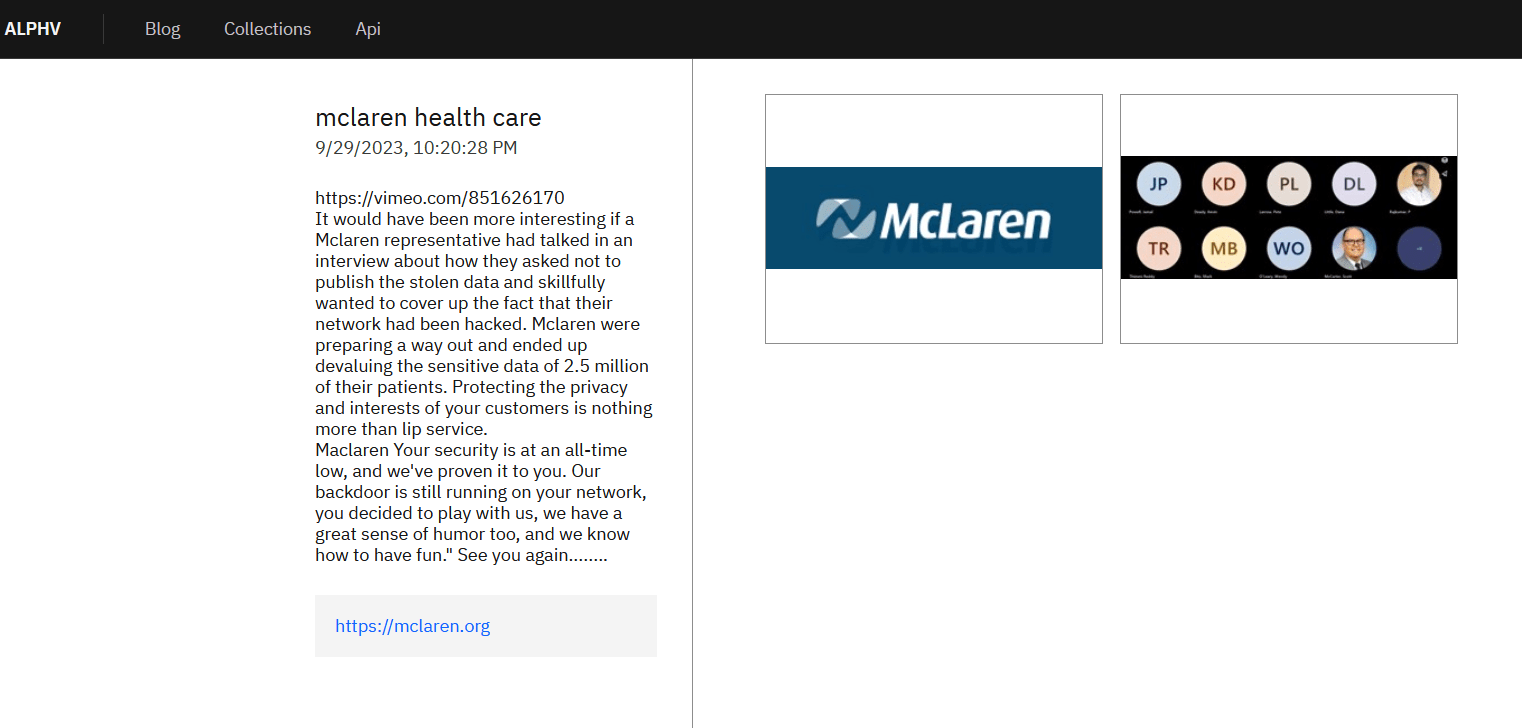
The ALPHV/BlackCat ransomware gang added McLaren Health Care to the list of victims on its Tor leak site. The group claims to have stolen data belonging to 2.5 million of McLaren Health Care patients.
McLaren Health Care

The ransomware group accused the organization of has attempted to cover up the security breach. The ransomware gang also added that they have still access to the network of the organization.

“It would have been more interesting if a Mclaren representative had talked in an interview about how they asked not to publish the stolen data and skillfully wanted to cover up the fact that their network had been hacked. Mclaren were preparing a way out and ended up devaluing the sensitive data of 2.5 million of their patients. Protecting the privacy and interests of your customers is nothing more than lip service.
Maclaren Your security is at an all-time low, and we’ve proven it to you. Our backdoor is still running on your network, you decided to play with us, we have a great sense of humor too, and we know how to have fun.” See you again……..” reads the message published by the ALPHV gang on its leak site.

The Alphv ransomware group has been very active in this period, recently it claimed to have hacked Clarion, the global manufacturer of audio and video equipment for cars and other vehicles, and the hotel chain Motel One.

The cyber security researcher Dominic Alvieri reported that ALPHV BlackCat Ransomware has breached 15 more US hospitals & 2 HMOs.

BlackCat/ALPHV ransomware gang has been active since November 2021, the list of its victims is long and includes industrial explosives manufacturer SOLAR INDUSTRIES INDIA, the US defense contractor NJVC, gas pipeline Creos Luxembourg S.A., the fashion giant Moncler, the Swissport, NCR, and Western Digital.

The ransom demands of the group range from a few tens of thousands of dollars up to tens of millions of dollars.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, McLaren Health Care)


