
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Medusa Ransomware targeted over 40 organizations in 2025

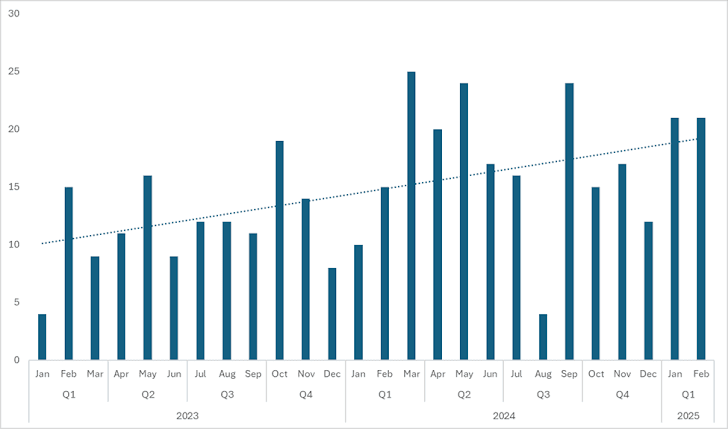
Medusa ransomware has claimed nearly 400 victims since January 2023, with attacks increasing by 42% between 2023 and 2024. The Symantec Threat Hunter Team reported that the Medusa ransomware operators have claimed nearly 400 victims since January 2023. Experts observed a 42% increase in attacks carried out by the group between 2023 and 2024. Experts […]

Medusa ransomware

Medusa ransomware has claimed nearly 400 victims since January 2023, with attacks increasing by 42% between 2023 and 2024.

The Symantec Threat Hunter Team reported that the Medusa ransomware operators have claimed nearly 400 victims since January 2023. Experts observed a 42% increase in attacks carried out by the group between 2023 and 2024. Experts tracked the Medusa ransomware activity as Spearwing.

Medusa ransomware

Between January and February 2025, the ransomware gang claimed responsibility for over 40 attacks.

“Like the majority of ransomware operators, Spearwing and its affiliates carry out double extortion attacks, stealing victims’ data before encrypting networks in order to increase the pressure on victims to pay a ransom,” reads the report published by Symantec.

Medusa demands ransoms from $100,000 to $15 million, victims are organizations in healthcare, non-profits, finance, and government sectors. The group targets known vulnerabilities, mainly in Exchange Server. The researchers speculate that the ransomware group relies on initial access brokers to access target infrastructure.

Upon gaining initial access to the target, Medusa hackers use remote management and monitoring (RMM) tools like SimpleHelp and AnyDesk for maintaining persistence and employ BYOVD with KillAV to disable antivirus, a tactic seen in BlackCat and RansomHub ransomware operations.

Symatec researchers highlighted that Medusa ransomware attackers use PDQ Deploy to drop tools, files, and move laterally across victim networks.

Medusa ransomware attackers use Navicat for database access, and RoboCopy and Rclone for data exfiltration.

Medusa ransomware is expanding amid disruptions to LockBit and BlackCat, highlighting the evolving RaaS landscape and the need for stronger cybersecurity defenses.

“Like most targeted ransomware groups, Spearwing tends to attack large organizations across a range of sectors,” Symantec concludes. “Ransomware groups tend to be driven purely by profit, and not by any ideological or moral considerations.”

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, ransomware)


